I find this move concerning, and wish that the Founder had looked for a new CEO that shared his values rather than a Private Equity and Mergers Expert.

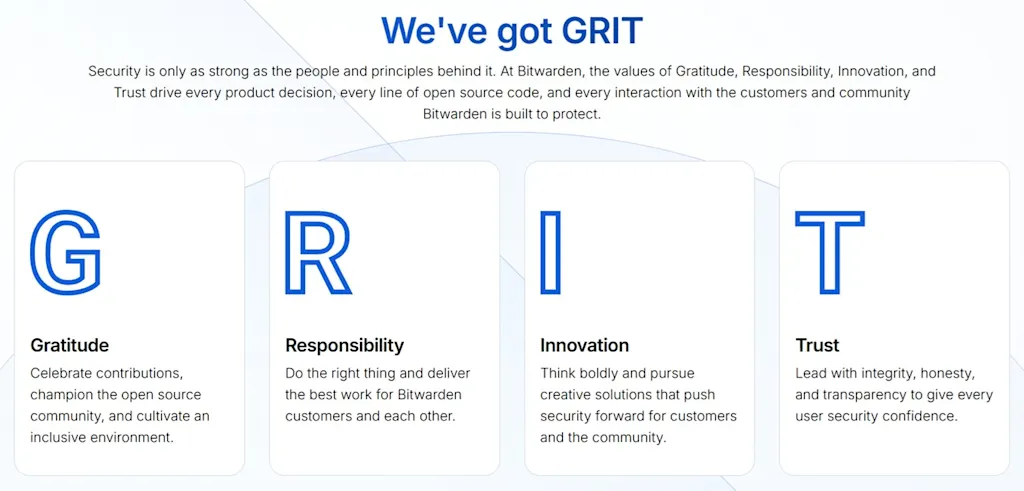
Furthermore, the change to the GRIT motto is worrying. Trust is useless without Transparency when it comes to code and security.

top 96 comments

sorted by: hot top controversial new old
[–] 292 points 5 months ago (49 children)

Is it that time when I say "oh shit!" and starts to look at alternatives? I've seen this scenario a hundred times already and I'm tired.

  • source
  • hideshow 49 child comments
  • [–] 120 points 5 months ago (4 children)

    I don't have the patience to switch to alternatives until they make a change that actually affects the usability of the tool.

    This is absolutely a red flag though.

  • source
  • parent
  • hideshow 4 child comments
  • [–] 62 points 5 months ago (34 children)

    Same question here. What are the best alternatives?

  • source
  • parent
  • hideshow 34 child comments
  • [–] 92 points 5 months ago (20 children)

    KeePassXC is the best FOSS option, but you'll need to figure out self hosting if you want to sync the database between devices.

  • source
  • parent
  • hideshow 20 child comments
  • [–] 40 points 5 months ago (13 children)

    As the database is encrypted in your device, you dont really need to self host. A keepass database in the Google cloud is not really problematic, although you should still choose a more private cloud provider.

  • source
  • parent
  • hideshow 13 child comments
  • [–] 28 points 5 months ago (9 children)

    Syncthing is probably a simple fix.

  • source
  • parent
  • hideshow 9 child comments
  • [–] 30 points 5 months ago (7 children)

    Assuming you have a degoogle'd phone. The syncthing-fork devs announced that they aren't going to certify for Google Play when that's made a requirement in a few months

  • source
  • parent
  • hideshow 7 child comments
  • [–] 18 points 5 months ago (4 children)

    Ugh, I forgot about this. Aren't you still going to be able to install apps from third-party marketplaces? I thought the plan was just that the phone was going to hassle you and require multiple hoops.

  • source
  • parent
  • hideshow 4 child comments
  • [–] 3 points 5 months ago (2 children)

    I think other apps will require ADB to install

  • source
  • parent
  • hideshow 2 child comments
  • [–] 8 points 5 months ago

    And you can use a keyfile separate from the database for even more security. If the database is backed up on Google Drive and the keyfile is saved on a USB or in a (non-Google) email somewhere for the rare times you add a new device, your passwords should be safe even from keyloggers or Google themselves.

  • source
  • parent
  • [–] 7 points 5 months ago (2 children)

    or use syncthing, no hosting experience required

  • source
  • parent
  • hideshow 2 child comments
  • [–] 2 points 5 months ago

    It doesn't need to be complicated. I use syncthing to synch them. It's pretty trivial. You just tell it what folders to synch, between which devices, and it'll synch whenever it's running.

  • source
  • parent
  • [–] 2 points 5 months ago*

    I found the easiest way to sync is to use rclone. This way you can use any cloud provider like Google Drive or OneDrive or DropBox. First create the rclone remote for your cloud provider using rclone config. Second step is to create a second remote using the encryption option (menu item 16), choosing an appropriate path <first remote>:<path to directory>. Upload your KeepassXC database to this encrypted remote using rclone copy.

    On Android you can use the RoundSync app from F-droid to configure the the same remotes, then create a task to copy or sync from that encrypted remote and a trigger to run that task on a schedule. Overall, this one-time setup works really well for me. This is my backup in addition to using Bitwarden for several years. Bitwarden is not going to get my money any more.

  • source
  • parent
  • [–] 34 points 5 months ago* (last edited 5 months ago) (4 children)
  • [–] 23 points 5 months ago* (last edited 5 months ago) (2 children)

    But you still use the official BW client apps, correct?

    Unless you forego usage of the clients and access Vaultwarden through the browser (removing accessibility and convenience especially on mobile), it is not an e2e replacement solution.

    Are there any alternative FOSS clients/apps that work with Vaultwarden?

    Edit: I see further down that the official client is open source, and would get forked in the event of any fuckery. So I'm sticking with Vaultwarden + Official client app approach for now.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 26 points 5 months ago (1 child)

    Coincidentally, I moved to self-hosting Vaultwarden last night, which is open source but compatible with Bitwarden. If you want a simple transition and are capable of hosting it yourself, that would be my recommendation.

  • source
  • parent
  • hideshow 1 child comment
  • [+] -6 points 5 months ago (6 children)

    I’ve been pretty happy with Apple passwords

  • source
  • parent
  • hideshow 6 child comments
  • [–] 3 points 5 months ago (5 children)

    Oh great. Let's go from an open client to a vendor closed-source lock-in.
    Sometimes I am baffled by the polarity of Lemmy.
    From Tryhard-only-libre-software type of users over A-bit-of-each users (but tending to sway towards (F)OSS application) over to this opinion/suggestion.

    Wild.

  • source
  • parent
  • hideshow 5 child comments
  • [–] 4 points 5 months ago* (2 children)

    Vendor lock in is an issue, true, but it's a different issue than the enshittification we're starting to see from Bitwarden. Also, apple passwords isn't "locked in" per se, as passwords aren't difficult to export.

    Lately, I'm starting to feel like finding good software (often FOSS but not exclusively) is increasingly a hook for later increased monetization. The 'agreement' I had with Bitwarden was they provide a solid service, and (while not required) I pay the $10/year honor system fee. That's been upped to $20 now, and now they're appearing to move away from their core principles. I won't be paying for another year.

    With Apple, the unspoken agreement is I "overpay" for my hardware, and they don't have incentive to monetize me otherwise. I'll admit, there are cracks forming in that agreement, but that's my read on it currently anyway, and I think probably the person to which you are replying to as well.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 2 points 5 months ago (1 child)

    Your decision are sound.

    Not a fan of the usability of Apple devices (I have an iPad, so I am not talking ou of my butt) but I can't deny they reduced user hostility is attractive.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 2 points 5 months ago

    iPad usability is in a really weird place. It's definitely the least "usable" of Apple's platforms, and to be honest I probably wouldn't be an Apple user at all if all they had was iPadOS and iOS. macOS is still attractive to me (the Liquid Glass theme notwithstanding). For the record, I split my password manager use between Apple Passwords and [now] self-hosted Vaultwarden. Each has advantages, and while I'd like to just use one, having two is working okay for me for now.

  • source
  • parent
  • [–] 200 points 5 months ago (9 children)

    Why the fuck does everything that's good turn to shit? This world sucks. This timeline sucks.

  • source
  • hideshow 9 child comments
  • [–] 84 points 5 months ago (6 children)

    it's all motivated by the accumulation of wealth = capitalism

  • source
  • parent
  • hideshow 6 child comments
  • [–] 11 points 5 months ago (5 children)

    Accumulation of power is a common motive regardless of political system. Money is just one way power gets expressed.

    Not claiming our system is perfect by any means. But this thought, to me, always felt like kicking the can down the road.

  • source
  • parent
  • hideshow 5 child comments
  • [–] 3 points 5 months ago

    That might qualify as an argument but the enshittification of everything hasn't gained anyone power, only money. Cuba was curing cancer before we started more war crimes in order to prove socialism doesn't work, while we're financing fast food.

  • source
  • parent
  • [–] 2 points 5 months ago

    I think there's a difference though, in that capitalism rewards this kind of innate motive, while socialism doesn't, so I think it would be much easier to build a system based on that that's not fucked from the foundations like capitalism is. The societal benefits of capitalism always feel like an accidental side effect at most, when it should be at a heart of any economy system.

    Also it definitely seems that holding power over others warps the human mind, so I would definitely advocate for distributing policy-making power as evenly across the population as possible.

  • source
  • parent
  • [–] 2 points 5 months ago (2 children)

    Kicking the can down the road implies you have a better solution?

  • source
  • parent
  • hideshow 2 child comments
  • [–] 4 points 5 months ago (1 child)

    A solution that stops evil people from being greedy for all of future society, gaming whatever our system is to hoard resources? No, I don't.

    Whether under capitalism or socialism, either system would need frequent attention and intervention by thoughtful, socially responsible people to watch for abusers of the system.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 1 point 5 months ago

    Right, but Capitalism incentivises this behaviour, thus making the checks and balances required both more robust and needing to be applied for regularly - while the powerful are capable of preventing this.

    On the other hand, Socialism has incentives that are completely different - managing the abusers would be a much simpler task.

  • source
  • parent
  • [–] 120 points 5 months ago (8 children)

    reading this as someone who migrated the rest of the household to Bitwarden literally yesterday: 😒

  • source
  • hideshow 8 child comments
  • [–] 36 points 5 months ago (5 children)

    It took me years after the lastpass breach to get my wife and 1/3 of my kids to switch to Bitwarden. I am not looking to having to migrate again.

  • source
  • parent
  • hideshow 5 child comments
  • [–] 14 points 5 months ago (1 child)

    but exporting is easy with bitwarden. this is annoying. after the age check laws, i have been moving off big companies because it will be bad snd i know my migration will take a bit. i finalized bitwarden a couple weeks ago and was just about to assist my family.

    i would not be as upset if ram and harddtives didnt cost a mortgage right now.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 10 points 5 months ago

    It does not matter how easy exporting is, the difficulty is going someone who really does not understand why they should be using a password locker to use one, much less change to a different one.

  • source
  • parent
  • [–] 4 points 5 months ago (2 children)

    You won't have to. Bitwarden is FOSS. The server is able to be self hosted so "migration" will just be you moving their account to the self hosted one if things go south

  • source
  • parent
  • hideshow 2 child comments
  • [–] 85 points 5 months ago (8 children)

    Luckily BW is open source, and VaultWarden exists. If they enshitify, all it takes is a fork of the browser extensions and apps with a rebrand.

  • source
  • hideshow 8 child comments
  • [–] 35 points 5 months ago (3 children)

    This right here is the only answer

    Companies can try to steal the app but they can only steal the name

  • source
  • parent
  • hideshow 3 child comments
  • [–] 8 points 5 months ago (2 children)

    Exactly, IMO Vaultwarden should just fork the clients and extensions and officially take the lead. Bitwarden can just go the way of OpenOffice for all I care.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 3 points 5 months ago (1 child)

    I'm out of the loop, what happened to OpenOffice?

  • source
  • parent
  • hideshow 1 child comment
  • [–] 3 points 5 months ago*

    OpenOffice was maintained by sun Microsystems and they were bought by oricale. At the time it was seen so negatively that a fork called libreoffice was created and almost immediately became the default office suite for most people who were using OpenOffice.

  • source
  • parent
  • [–] 84 points 5 months ago

    1Password took investor funding, moved to subscription and focusing on corporate.

    Bitwarden heading the same way. Great…

  • source
  • [–] 59 points 5 months ago* (6 children)

    This is troubling and I am going to accelerate my migration to Vaultwarden. I'm not going to leave Bitwarden yet but I saw how this played out with LastPass, and I was a happy LastPass customer until I wasn't.

  • source
  • hideshow 6 child comments
  • [–] 12 points 5 months ago* (5 children)

    Docker and caddy make this pretty easy. Even easier if you have a static ip and go to porkbun for a domain.

    And that’s only if you wanna access it outside your network. Mostly you can get away with syncing before you leave.

  • source
  • parent
  • hideshow 5 child comments
  • [–] 21 points 5 months ago (3 children)

    Or just use ZeroTier/Tailscale/NetBird/Wireguard and you can access your server from anywhere without exposing it to the imternet directly.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 5 points 5 months ago (2 children)

    Yeah I know but I’d rather just expose the services I want.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 55 points 5 months ago* (last edited 5 months ago) (5 children)

    The company has long defined its values with the acronym “GRIT,” which used to stand for “Gratitude, Responsibility, Inclusion, and Transparency.” After May 4, it changed the acronym to stand for “Gratitude, Responsibility, Innovation, and Trust.”

    It's not as bad as the headline seems. Transparency is still in the motto. The actual change is:
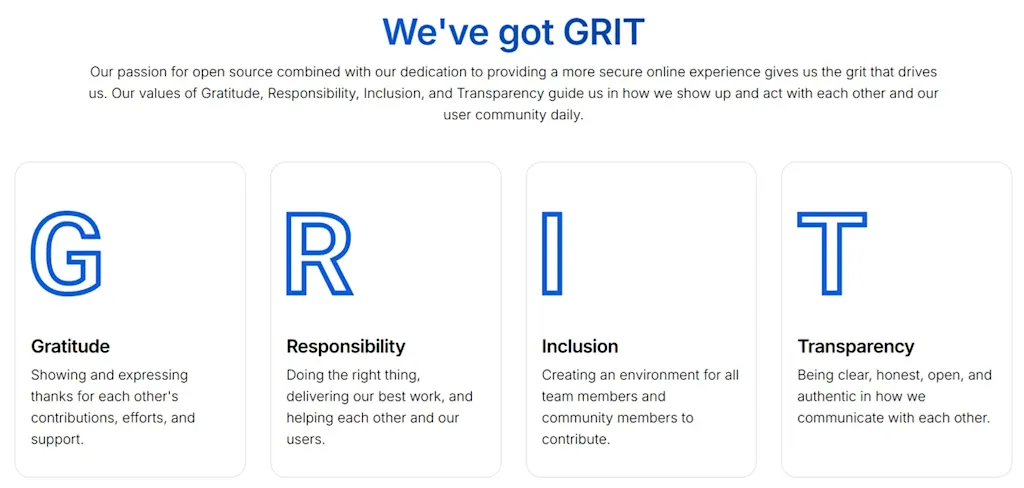
    before

    after

    But still. Why change it at all? Why replace "inclusion" with "innovation"?

    It smells like Tech Bro.

    There's just no way to spin that positively, even giving them the benefit of the doubt, especially since they aren't rolling it back. Someone spent effort to make that values change, so its not an accident nor a "nothingburger".

  • source
  • hideshow 5 child comments
  • [–] 4 points 5 months ago

    Ty. So many comments here didn't see your post and others did but didn't read it. My take is innovation is a greater priority, and trust protocols. I'll watch but I'll wait for it to be a something burger.

  • source
  • parent
  • [–] 51 points 5 months ago

    “You either die the hero, or you live long enough to become the villain”

  • source
  • [–] 50 points 5 months ago (2 children)

    Why does every good thing always have to go to shit. Sigh.

  • source
  • hideshow 2 child comments
  • load more comments
    view more: next ›
    213 comments in c/selfhosted@lemmy.world view that post
    30 comments in c/privacy@programming.dev view that post
    21 comments in c/bitwarden@discuss.tchncs.de view that post
    4 comments in c/hackernews@lemmy.bestiver.se view that post