…except the local bird population.

You should ask your AI chatbot if this is a fitting community to post this in. Because it isn't.
So I built Crabshell
The git says Claude did it though.
I had painful diarrhea for the glory of the empire!
2.85 for e.g. TPU is a serious upgrade. Can't wait for manufacturers who respect their customers to implement this cool new feature.
Aren't we talking about someone logging in remotely?If you're on premise it would be a VLAN with its own wifi hotspot (or similar setup), but those systems running day and night in grocery stores aren't monitored by someone locally.
No, but it's a start and pretty much standard security practice for internal or critical tools.
Now that I think about it, Yani Neko must be phenomenal with blowjobs. Though you might get second-hand nicotine addiction through your dick.
Not saying fixed bugs aren't good, I'm just so fed up with this marketing-driven fearmongering. They're overhyping every god damn bug they can because they know most people won't know how bad it actually is. They do worse security practices than most homelab enthusiasts and then prophesize the AIpocalypse because their linear algebra "escaped" (the door was wide open). Hell, they don't even manage to understand proper bug disclosure practices. They're playing the "Social" Media outrage game on a global scale to drive sales and everyone is suffering for it. I'm so, SO done with all of this bullshit. When the bubble finally crashes I'll throw a raging party with blackjack and hookers.
For server crashes, but not for RCEs. The only proven case of this I know of was with a specifically prepared PHP instance as honeypot that had an optimal attack surface and was done by Perplexity (another AI company). Outside of that there's no credible large-scale RCE exploitation that's any worse than the bugs that get fixed on a daily basis. It doesn't even remotely justify the panic and media frenzy.
it was merely dangerously exploited by AI bros.
This is shady as hell. It's an AI company again (Anthropic), they do not follow rules of responsible disclosure (again), it's a race condition again, they do not provide a proof of concept (obviously since they shouldn't talk about it at all until after we got the patch) but instead create big media fuzz about their glorious AI… hell, they do not even tell us the kernel versions or anything.
If we find out eventually that you have to disable default mitigations for this to become dangerous (like the stunt they did with Firefox) it's too late, the media won't give a shit anymore. Like we just had with PHP - huge panic, enormous media circus, barely any real-life consequences in the end and the responsible disclosure process being a total mess to blow it up even more.
Honestly, every time I see some AI company hyping yet another huge and super dangerous exploit only their superior AI found "after X years of nobody seeing it" I now expect a nothingburger.
We're probably fine, nothing out of the ordinary to see here.
They have really bad railway, or so I've heard.
It got a standard camera as well.
It got a standard camera as well.
…except the local bird population.
Well… shit.
At least they confirmed they're working on enabling EAC correctly… at some point.

Because of course it now does. Welcome to Bambu.
(Subscription-based after 14 days, they don't mention it to catch people)
Source: https://connectified.com/@masukomi/116736929422875166

EDIT NOTICE: I accidentally wrote "A1 Mini" in the meme instead of just "A1" out of habit. There's no proof for the Mini to also be affected yet. My bad, sorry. It's the A1 that might burn your house down.

I'm somewhat puzzled which settings I need to look at in PrusaSlicer to solve those thin slits between perimeters. I've dialed in the flowrate optimally for dimensional correctness and 245°C (PETG) works really well for both flow and overhangs.
At first I thought of extrusion width, but that also increases the distance between each line. Raising the flowrate closes them, but also makes the printed parts grow in each dimension outside if the intended size.
Where am I missing something? Which settings do I need to adjust to not screw up everything else?
EDIT: It's not just corners!

I'm trying to find the reason why my bigger printer suddenly decided to constantly create blockages as high as the PTFE tube in the cooling block (so a little bit above the heatbreak).
It's an older V6 head. The discolouring on the heating block comes from the single time the nozzle came lose and PETG was pressed through the threads upwards, that was a year ago though. I didn't change anything, from one day to another it just decided that (for both PLA and PETG) it'll now stop working properly.
Waiting on a stronger cooling fan (strongest Sunon I could find, the one with 9000rpm). Other than that I'm just confused why this suddenly happens.

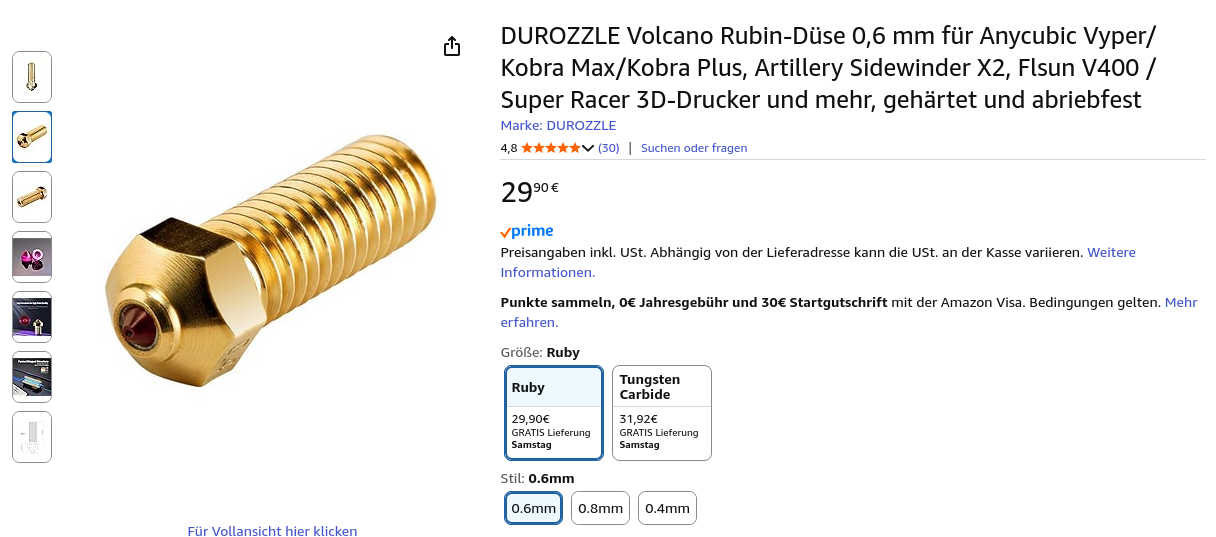
I'm thinkin about getting one of those ruby nozzles for my printers to basically be able to print anything without ever having to worry about a degrading nozzle. I've seen quite a few videos about it, but I still don't know two things:
And also