I tried testing a movie from my home server in plex through firefox and repeatedly got this message, even after reloading.

I knew that they had paywalled the apps on mobile and streaming from outside the network but now they have also blocked watching your own movies through your own hardware.

I do get the point that making software should be able to sustain people but I dont see the move of plex as a fair thing to do. Yes, they have made great software but taking your home server hostage feels like the wrong move.

Even a pop up that says "we need you to donate please" would have been fine. make it pop up before every movie, play donation ads before any movie but straight up disabling the app is kinda cruel.

Anyway, i have switched to jellyfin and it is insanely good. please give it a try. you can run it alongside plex with not issues (at least i had none) and compare the two.

In any case, good luck. Let me know if you need help.
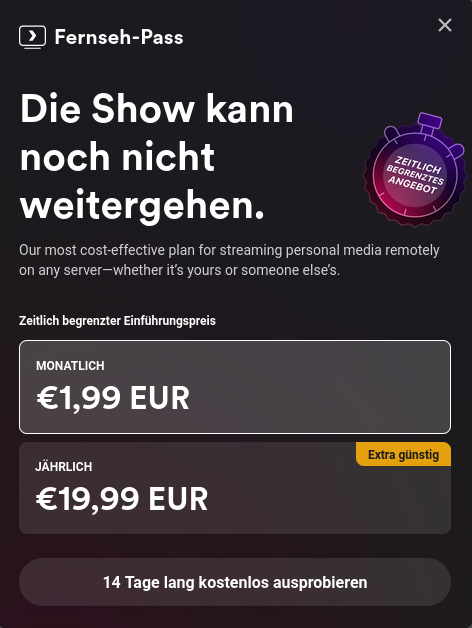
Screenshot of a pop up in plex media center saying "die show kann noch nicht weitergehen" which means the show cant go on yet. below are pricing options to buy a subscription. this is displayed on a home server in the same network. plex has worked for years.

top 96 comments

sorted by: hot top controversial new old
[–] 38 points 1 year ago (38 children)

It's pretty rare that a company starts taking away free features and doesn't end up fucking payers in the end.

The biggest bar to Jellyfin is TV clients, the second biggest is security.

TV clients can be fixed with a one-time purchase of a $20 android TV stick. If viewing your familys ARR content isn't worth $20 you probably don't need to do it anyway.

Security for remote streaming is a harder thing to handle. Most people are capable of port forwarding, But just hanging a smallish public project out there in the open is always a dicey proposition. It honestly needs real fail2ban, probably SSL, 2FA and password complexity requirements.

We could probably make a jellyfin helper container to handle some of this. Walk people through Let's Encrypt, dynDNS, port forwarding tests, add fail2ban with a firewall, maybe even slap suricata in it.

We need to convince the project to add 2FA and password complexity requirements.

I don't know guys what do you think is it crazy? does it make sense? Would anybody actually use it?

  • source
  • hideshow 38 child comments
  • [–] 19 points 1 year ago (5 children)

    I access my stuff via VPN. As for sharing with others, I simply don't do that. VPN is still an option though. Or temporary client whitelisting, etc.

  • source
  • parent
  • hideshow 5 child comments
  • [–] 1 point 1 year ago (3 children)

    Now that's an interesting thought.

    A web page with Authelia, login and a firewall.

    If you're not logged in, All you get is a login page. If you are logged in, It passes you straight through to jellyfin.

    So any device and client would be able to access it without issue once a phone or computer on the network had logged in just once.

    The web page modifies the HA proxy ACL and forces a reload.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 2 points 1 year ago (2 children)

    This will work fine over the web, but won’t work with clients.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 1 point 1 year ago (1 child)

    They have instructions on jellyfin forums on setting up HAProxy, that part totally works.

    But you don't put 2FA on the jellyfin server, for that you just deny all IPs except whitelisted.

    You did the 2FA on the whitelister only using path-based routing.

    You don't have access to the root site, you go to a path and login to a separate database to whitelist yourself then your client should work from that IP.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 1 point 1 year ago

    This will work fine over the web, but won’t work with clients.

    They have instructions on jellyfin forums on setting up HAProxy, that part totally works.

    But you don’t put 2FA on the jellyfin server, for that you just deny all IPs except whitelisted.

    You did the 2FA on the whitelister only using path-based routing.

    You don’t have access to the root site, you go to a path and login to a separate database to whitelist yourself then your client should work from that IP.

    edit:

    I just tried it, it appears to work so far.

    I can send websocket traffic inbound to 8096: to the JF server and it loads on web, Android and Roku clients with an ACL limiter on originating ips. and send 8096/whitelist to another server altogether with no ACL limits.

    On that process, I'd load nginx, authelia, fail2ban and what flask? Surely someone has a python longin/admin framework that I could hijack for this. Then have that app reack over in shared container storage to twiddle the haproxy config to add some ip's and reload it?

    I wonder if I could do something to the haproxy side to detect non-use of an IP and remove it.

  • source
  • parent
  • [–] 0 points 1 year ago

    Yeaaah ! Most people anyway have some kind of VPN installed on their device... Just slap in a wireguard VPN config to tunnel your traffic home... bOOm jellyfin everywhere and 99% secure !

  • source
  • parent
  • [–] 4 points 1 year ago (12 children)

    You can address the 2fa by putting it behind something like authelia, but still, the project needs to step it up

  • source
  • parent
  • hideshow 12 child comments
  • [–] 1 point 1 year ago (10 children)

    I thought that you can still access media directly via the URL without any authentication, how would authelia change that?

  • source
  • parent
  • hideshow 10 child comments
  • [–] 2 points 1 year ago (9 children)

    Yes! You just have to set up your reverse proxy to send everything through it and it'll block the unauthenticated access.

    The downside is that apps stop working since they don't have a way to authenticate with authelia. I've installed it as a PWA on my phone and use an old laptop with the TV interface on my TV, but it's not perfect

  • source
  • parent
  • hideshow 9 child comments
  • [–] 1 point 1 year ago (8 children)

    Are you sure that works? I'm pretty sure they mentioned that reverse proxies are an unsupported (and not working) use case with Jellyfin, but I might have to look into authelia some time then.

  • source
  • parent
  • hideshow 8 child comments
  • [–] 3 points 1 year ago (4 children)

    I just put it behind an HAProxy a few minutes ago, It appears to be fine. You just need something capable enough to handle web sockets. I've made it all the way through an episode of The real monsters without any problems.

    Again, you're not going to be able to 2FA it that way, what I'm looking at doing is IP whitelisting it in HAProxy using a small web helper that is 2FA, accessed via the same port but on a separate path.

  • source
  • parent
  • hideshow 4 child comments
  • [–] 1 point 1 year ago (3 children)

    Maybe I was thinking of this from back in 2024?

    https://github.com/jellyfin/jellyfin-android/issues/123

    "Hacking around with a reverse proxy is strongly discouraged and we won't provide any support for it."

  • source
  • parent
  • hideshow 3 child comments
  • [–] 1 point 1 year ago (2 children)

    Yeah part of doing this is keeping a ci pipeline up and unit testing against rcs and telling them exactly what's failing. The report in that ticket gave them absolutely no choice but to try to set up an entire system to reproduce whatever the user did which they obviously don't want to do.

    WebSocket relays are poorly implemented in a lot of proxies, Even cloudflare has its fair share of issues.

    The downside of using HA is reinventing the let's encrypt pipeline for the 40th time, the upside is it's dead simple, web sockets go in, web sockets go out, The logs are good, it's easy to debug it with TCP dump If things start to get sketchy.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 1 point 1 year ago (1 child)

    How can you debug it with a TCP dump if it's encrypted?

  • source
  • parent
  • hideshow 1 child comment
  • [–] 1 point 1 year ago

    You are doing the https unwrapping in tf/HA proxy. It's clear text between the proxy process and the JF server

    You can do a dump off the entire network stream when it's working, install the release candidate and do another dump of the network stream with it not working. Sift through to find the changes.

    When the person posted that there was a problem with the RC, It was probably a web socket being mishandled by the proxy due to some change. You can't just go oh there's a problem with my third party middleware. They're going to need to know which of their changes broke the problem. Why it breaks it, and what should be done instead if you expect them to make any kind of changes.

    The alternative is you ask them to support traffic or HA or NPM, and on a volunteer project I could see that being a bridge too far

  • source
  • parent
  • [–] 2 points 1 year ago* (2 children)

    Both jellyfin and authelia support reverse proxies.

    Here's jellyfin's guide: https://jellyfin.org/docs/general/post-install/networking/reverse-proxy/

    And here's authelia's: https://www.authelia.com/integration/proxies/introduction/

    There's some restrictions (like websocket support) but it's not too bad to set up.

    Still, if you don't need to expose it to the internet, put it behind a vpn.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 1 point 1 year ago

    The problem with putting it behind a VPN is then all your users have to be on VPN.

    Self-service IP whitelisting would be easy and let all clients work without trying to hack in a separate VPN client.

    The only thing that would suck would be if you were on a mobile link while moving and swapping towers your IP would change so you constantly get kicked off.

    But if you were so inclined you could VPN to your own house and your IP would stay the same.

  • source
  • parent
  • [–] [S] 3 points 1 year ago (1 child)

    I think you make a hugely important point and I would definitely use it and I might even be able to help making it.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 3 points 1 year ago* (1 child)

    Security for remote streaming is a harder thing to handle. Most people are capable of port forwarding, But just hanging a smallish public project out there in the open is always a dicey proposition. It honestly needs real fail2ban, probably SSL, 2FA and password complexity requirements.

    Yeah.

    It's tough because I get they're an open-source project, and they're volunteers, but at the same time, security is something that should be the highest priority.

    Though, you could just make it so that it's not accessible via WAN and instead has to go through a VPN, though that'd make it harder to share with others.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 2 points 1 year ago

    That's what I do myself but in a lot of cases VPN is beyond the grasp of the grasp of the friends and family that are being shared with.

    Tailscale is somewhat approachable for this, there are a number of streaming devices that support TS clients. But then tailscale will eventually enshittify their free offering. Wrapping headscale into this will add yet another layer of complication. VPN is far more secure but I think it makes it unapproachably complicated for many.

  • source
  • parent
  • [–] 3 points 1 year ago (5 children)

    As someone who is … lazy and took advantage of some Amazon Black Friday Fire TV stick deals, and who doesn’t want to drop the $200 for a Shield:

    Any Android sticks/players you might recommend?

  • source
  • parent
  • hideshow 5 child comments
  • [–] 1 point 1 year ago (2 children)

    Basic functionality, I've heard good things about the crappy Walmart ONN branded ones.

    I know there are Alibaba options, But I'm awfully afraid of a lot of those have worst security issues than opening up jellyfin.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 3 points 1 year ago (3 children)

    What are my realistic security concerns with a jellyfin server that I let friends and family watch while trying to minimize the troubleshooting and steps they need to take to get started?

  • source
  • parent
  • hideshow 3 child comments
  • [–] 1 point 1 year ago (1 child)

    realistic security concerns

    If you're running a binary installation of Jellyfin on your server and exposing it to the public internet, you can face significant risks:

    • Remote execution vulnerabilities might allow attackers to exploit bugs to run malicious code on your server.

    • Buffer overflows. Poorly handled data can let attackers manipulate memory, Bypass logins, touch things in the host that aren't meant to be twiddled with

    • Network exposure. If compromised, the server could become a launchpad for attacks on your network.

    There might not be any vulnerabilities at this moment, but they might come in a future release. And we might not even know they exist. It's a small team of volunteers, and they'll do their best. This is just what is reasonably possible when installing the server as an application on your OS and exposing it to the Internet.

    You can minimize risk with a safer setup, as someone else in the comments here mentioned (and I think they even linked to their setup)

    Using a Docker container version of the app significantly reduces your attack surface. This isolates the app from your host system. If they get in, they only get into the container and whatever that container is allowed to do.

    Mount your media files as read-only to prevent accidental modifications or potential malicious changes. Now that container can't do any real harm do your data.

    Avoid making the container privileged. A privileged container can interact with the host system in risky ways.

    Use reasonable unique usernames and passwords. If the container does manage to get compromised, they will likely be able to read usernames and passwords stored in the container.

    Regularly update your container – Ensures you have the latest security patches.

    Short of some massive Docker vulnerability, (which is on you to keep updated) the worst case should be public enumeration of your media, exposure of your JF users/passwords, and denial of service. Which IMO isn't very serious.

    For even tighter access control, don't whitelist the entire world.

    Whitelist specific IP addresses. Have users visit WhatIsMyIP to get their IP, then configure port forwarding to allow only trusted addresses. This allows the clients at their houses in without any serious hinderance, but would block them from accessing your media when they're not at their house.

    If they're accessing you through a phone or PC, setup headscale or tailscale or any VPN and allow them to get to you through VPN

  • source
  • parent
  • hideshow 1 child comment
  • [–] -3 points 1 year ago (4 children)

    probably SSL

    *TLS

    SSL has been deprecated for a decade at this point

  • source
  • parent
  • hideshow 4 child comments
  • [–] 12 points 1 year ago (3 children)

    Would you consider this a particularly constructive comment?

  • source
  • parent
  • hideshow 3 child comments
  • [–] 2 points 1 year ago (2 children)
  • [–] 1 point 1 year ago

    The term SSL has been colloquially used for the last decade, and it would be difficult, if not impossible, to confuse the two and issue the wrong type of security at this point. Are there even packages that old available to Docker?

    We're having an informal discussion here about how to make Jellyfin security less daunting to the average user. Taldan is apparently knowledgeable about the situation and could lend a conceptual hand to the process, but I suspect they chose instead to nitpick terminology that's still used in common parlance. Since I have some doubts, but don't wish to assume, I asked a simple question.

  • source
  • parent
  • [–] 30 points 1 year ago (4 children)

    Welp, i killed mine yesterday as it wouldnt let me stream while offline. Modem died so no Internet for me. Why do i have everything local if it dosent work while offline...

  • source
  • hideshow 4 child comments
  • [–] [S] 18 points 1 year ago (2 children)

    Exactly. Thats why i use jellyfin now. Try installing it alongside. For me it worked well.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 2 points 1 year ago

    FYI you can definitely watch while your network is offline. You just net to tell it that you're happy with that (it's not activated by default for security reasons).

    • In your Plex server settings, go to Network, enable "Show Advanced".

    • Near the bottom, find the textbox that says List of IP addresses and networks that are allowed without auth

    • In this field, enter the local IP address of any Plex client(s) you want to keep using if your internet (or the Plex cloud) is down.

    • A example: 192.168.0.50

    • Save the setting, done.

    #Important thing to be aware of:

    What this setting does is tell your local Plex server to simply give any Plex client that connects from that specific IP full admin access to your Plex server, ignoring any account restrictions. This means that if you have things in place to restrict access to some libraries (kids blocked from 18+ movies etc) those restrictions will have no effect. Also if you have the option set to allow file deletion, then any client from that IP could also delete items. And they could of course change any settings in your Plex server. So your kids can watch anything on your server, if you have a guest in your network and they browse to the Plex web interface, they can mess with things.

    Because of that I would recommend to limit the amount of IP's you enter in that field to the absolute bare minimum. For example, only whitelist the "main living room device" plus one device you to admin the server, such as a laptop.

    If you want to whitelist multiple devices, this is a example:

    192.168.0.50,192.168.0.77,192.168.0.80
    

    If you want to whitelist a entire network, these would be examples:

    192.168.0.0/24 (this means 192.168.0.0 - 192.168.0.255)
    
    192.168.0.0/16 (this means 192.168.0.0 - 192.168.255.255)
    

    And of course those involved network devices should use static IPs in your home network.

  • source
  • parent
  • [–] 95 points 1 year ago (16 children)

    Every non-Free Software will betray you eventually. It's only a matter of time.

  • source
  • hideshow 16 child comments
  • [–] 20 points 1 year ago (3 children)
  • [–] 6 points 1 year ago (2 children)

    I just wonder if plex will ever sell the list of movies and IP address of everyone. Many people have the ARRs to auto download, even stuff still in theaters. What good is a VPN when plex knows your email and IP.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 9 points 1 year ago

    Honestly, I'd be rather shocked if this wasn't already the case.

    Moreover they probably have a database of everything you've ever watched and your IP and email address, just waiting to be leaked to the internet through sale or ransom.

  • source
  • parent
  • [–] -3 points 1 year ago (7 children)

    I thought free software was when you were the product and non-free software actually supported developers.

    Or do you mean non-OSS?

  • source
  • parent
  • hideshow 7 child comments
  • [–] 17 points 1 year ago (3 children)

    Free as in freedom, not as in free beer.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 4 points 1 year ago (2 children)

    I thought we switched to libre for that definition and since then used free only as in free beer.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 6 points 1 year ago

    I thought we switched to libre

    Maybe some people did. Thing is there's a whole rest-of-the-world out there, and they didn't necessarily get the memo or are happy with the existing way.

  • source
  • parent
  • [–] 4 points 1 year ago

    Libre (from French) is sometimes used to solve the ambiguity of the word free in the English language, but it sounds kinda awkward in English and there's certainly no consensus that this should be the official replacement, or that the term free even needs replacement.

    Furthermore, the FSF who originally came up with the idea of "free software" still exists and is still called the Free Software Foundation, though Stallman uses both terms interchangeably.

  • source
  • parent
  • [–] 4 points 1 year ago

    Yeah, the wording is confusing. A long time ago, there was no paid software, there was only software where you got the source code and other software where e.g. it was pre-installed on some hardware and the manufacturer didn't want to give the source code.

    In that time, a whole movement started fighting for software freedom, so they called their software "free".

  • source
  • parent
  • [–] 41 points 1 year ago (5 children)

    Remote, yes, they announced you need Plex pass one side or the other for it to work.

    Local, no, that shouldn't happen. Your device isn't reaching your Plex server locally.

    To work around the remote issue, you can VPN to your local network.

    But you're better off in the long haul with Jellyfin as you're doing now.

  • source
  • hideshow 5 child comments
  • [+] [S] -22 points 1 year ago (4 children)

    Yeah no. That is local. But thanks for the suggestion. Jellyfin works well.

  • source
  • parent
  • hideshow 4 child comments
  • [–] 22 points 1 year ago (1 child)

    It isn't hitting it locally is the issue. Not an uncommon problem with plex unfortunately, its going out to come back in, so the server and client see it as remote.

    Without playback you wouldn't even be able to see that in the dashboard, which just makes the direction Plex is going so much more problematic.

    Like I said, better off using JF.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 14 points 1 year ago (1 child)

    Its not a local connection if you're getting this message. You might be in the same network, but for some reason it's not connecting directly.

  • source
  • parent
  • hideshow 1 child comment
  • [+] [S] -10 points 1 year ago

    You're assuming something that you just cant. I run this network alongside 5 others, some of them professional, for years. My configuration is standard and i'm using the software the same way i did for years.

    If plex redirects my call to their server, that is their problem, not mine. I dont care what their inner workings are. I use a local address and this has happened for the first time.

    Is it possible that it is an honest mistake on the side of plex? Yes.

    That does not absolve them from the end result.

  • source
  • parent
  • [–] 34 points 1 year ago (28 children)

    Old news, but time for Jellyfin. I made the switch a couple months ago. Some minor teething issues, but better, IMO, especially now as my family all have LDAP users and that just works.

  • source
  • hideshow 28 child comments
  • [–] 3 points 1 year ago (7 children)

    I made the switch a few months back as well. Have you had the issue where"Recently Added" just straight up doesn't work? It's about 50/50 for me whether my new downloads show up there or not, and if they do, it's usually inserted somewhere down the list between other things I added months ago. Not sure if there's a workaround, but it's my #1 complaint with Jellyfin. Otherwise, it's been great.

  • source
  • parent
  • hideshow 7 child comments
  • [–] 3 points 1 year ago (6 children)

    How is your underlying file system set up?

  • source
  • parent
  • hideshow 6 child comments
  • [–] 1 point 1 year ago* (last edited 1 year ago) (5 children)

    It's an Unraid share on a local NAS, and the array is formatted as xfs.

  • source
  • parent
  • hideshow 5 child comments
  • [–] 1 point 1 year ago (4 children)
  • [–] 1 point 1 year ago (3 children)

    I'm actually not 100% sure how to answer that. It's just a "share" configured through the Unraid UI, being accessed by a docker container running on the same machine (binhex's Jellyfin image.) I think that the "share" in this context is essentially just a mount point, but it's also (optionally) exposed as an SMB share externally.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 2 points 1 year ago (2 children)

    Ahh OK, a Docker bind. 3 things to check:

    1. That you added the folders in that weird way Unraod requires, see: https://forum.jellyfin.org/t-solved-jellyfin-not-detecting-media-in-unraid (this probably isn't it, but worth checking)

    2. Make sure for newly added, Jellyfin is configured for Date File Scanned into Library, vs the Created Date on the file

    3. Ensure the Arrs aren't set to change the date on file import. By default they modify created/modified dates to be the release date, which can put things in an unexpected order.

  • source
  • parent
  • hideshow 2 child comments
  • [–] [S] 3 points 1 year ago (16 children)

    awesome. thanks for chiming in. I will have to check how to do external streaming without opening my network up to the world (metaphorically).

  • source
  • parent
  • hideshow 16 child comments
  • [–] 9 points 1 year ago* (last edited 1 year ago) (8 children)

    ...wireguard

    (there are android TV apps for wireguard, not that any normie can actually move a client file to it and turn it on, or could be bothered to)

  • source
  • parent
  • hideshow 8 child comments
  • [–] [S] 4 points 1 year ago (7 children)

    Thats not what I meant. I of course have wireguard set up for administration and my own streaming needs. But friends of mine who were able to use plex by just making an account but now they cant because of course there is no relay server etc. I'll have to think of a way to make it available to them (easily!) without putting my network at risk.

  • source
  • parent
  • hideshow 7 child comments
  • [–] 3 points 1 year ago (6 children)

    Mine is public, but I block every state but the one all of my users live in(family) and I never get unwanted visitors. Couldn't say the same if I lived in NY or CA.

    If they have static IP addresses, you may be able to whitelist them in your proxy, or maybe there's some sort of dyndns client/relay software you can run if their ips change.

  • source
  • parent
  • hideshow 6 child comments
  • [–] [S] 2 points 1 year ago (5 children)

    yeah, thanks. but thats not gonna work for me. i live in a big city and none of us (me and my server included) have static IPs nor am I gonna get them (at all) and I dont want to pay for them either (because ISPs here want you to pay for them). in any case, thanks for trying to suggest something. it might help someone else who has a different setup. :)

  • source
  • parent
  • hideshow 5 child comments
  • [–] 1 point 1 year ago (4 children)

    Welp, I guess they'll just have to start their own servers or you'll have to get out your credit card. Pity.

  • source
  • parent
  • hideshow 4 child comments
  • [–] [S] -1 points 1 year ago (3 children)

    yeah no. there are a lot of other solutions to this. they're just a little annoying. others have confirmed there are similar setups like plex is doing with a relay server, but selfhosted.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 2 points 1 year ago* (2 children)

    there are a lot of other solutions to this

    Jellyfin servers don't connect to eachother, or relay themselves to anything else beyond simple reverse proxies. I looked over the entire thread and didn't see anything but ldap and tailscale/wireguard suggestions.

    You said there were a lot of other solutions, so wherever those solutions are, I'm sure they'll work out. Good luck!🙃

  • source
  • parent
  • hideshow 2 child comments
  • [–] 2 points 1 year ago (3 children)

    I used synology and reverse proxy. It was pretty easy to set up. The tricky part was going into jellyfins setting and connecting your reverse proxy to the path you made.

    Overall my kids and family can now access it anywhere.

  • source
  • parent
  • hideshow 3 child comments
  • [–] [S] 2 points 1 year ago (2 children)

    I run a reverse proxy too. are you talking about a public one? I'm probably gonna use a relay server for it which essentially is the same I guess.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 2 points 1 year ago (1 child)

    Can your router open ports from a hostname vs an IP? If so, clients could run dynamic DNS.

    WG client side isn't really that hard, though. All the fam run WG 24/7 on devices, and only traffic for the internal network goes through it.

  • source
  • parent
  • hideshow 1 child comment
  • [–] [S] 1 point 1 year ago

    I know. the issue is my friends dont have networks run by me. So I have to gain access to them and have to change setups which makes the situation likely to blow in my face. its just not a good solution imo. People have already suggested a relay server which will likely be the best solution.

  • source
  • parent
  • [–] 1 point 1 year ago (2 children)

    Give me a package that runs on my ds214play and I'll switch in a heartbeat

  • source
  • parent
  • hideshow 2 child comments
  • [–] 2 points 1 year ago (1 child)

    https://github.com/SynoCommunity/spksrc/issues/5941 ?

    I really wanted Jellyfin working in my DS214Play with DSM6, and I noticed that a package for these evansport CPUs doesn't exist and it's officially not supported, so I tried myself and I succeeded.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 3 points 1 year ago

    Thanks for the link. It seems they got it somehow working on DSM6, but if I check the thread, it's a lot of ducttape and locktight involved especially to run with DSM7. Might try it out on a rainy sunday

  • source
  • parent
  • load more comments
    view more: next ›