top 99 comments

sorted by: hot top controversial new old
[–] 242 points 1 year ago (3 children)

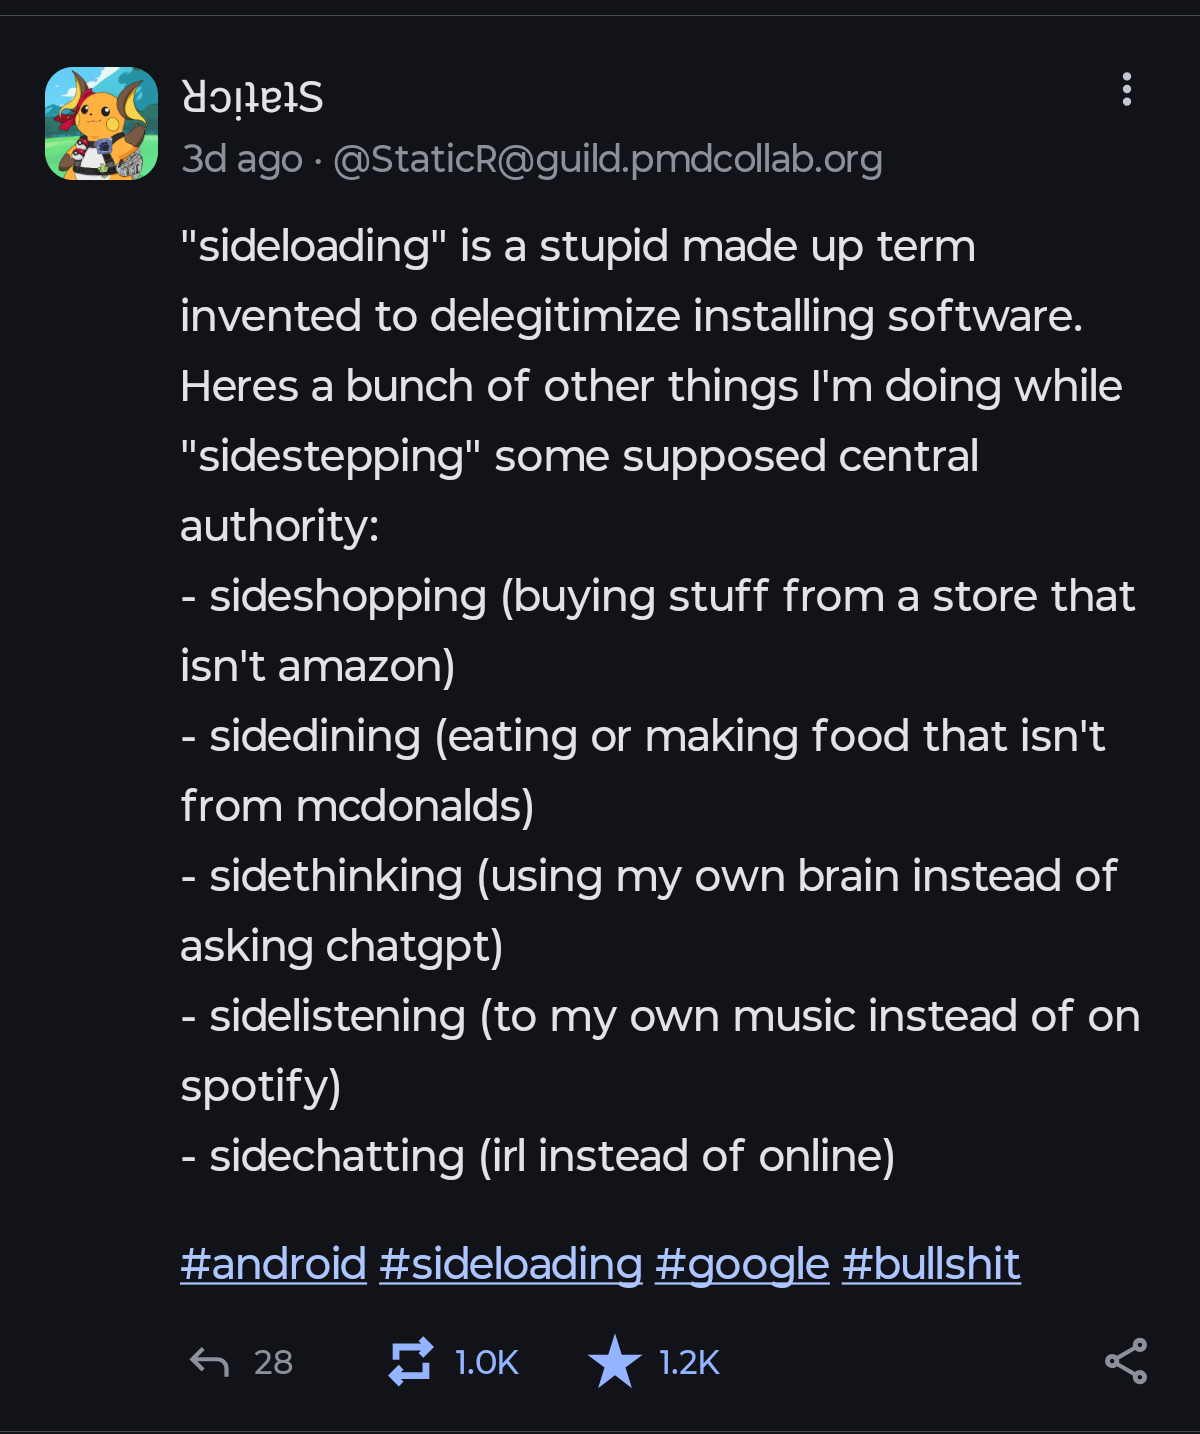
Call sideloading what it is, installing apps.

  • source
  • hideshow 3 child comments
  • load more comments (1 reply)
    [–] 204 points 1 year ago (5 children)

    Since Google’s goal is to improve security

    Is it though? Really?

  • source
  • hideshow 5 child comments
  • [+] -15 points 1 year ago (2 children)

    What ulterior motive do they have for blocking sideloading?

  • source
  • parent
  • hideshow 2 child comments
  • [–] 27 points 1 year ago (1 child)

    Essentially banning any apps that would hurt googles profits.

    I thought that was pretty obvious.

  • source
  • parent
  • hideshow 1 child comment
  • [–] -4 points 1 year ago* (last edited 1 year ago)

    It’s not. They already allow multiple app stores so they are not profiting off of every app.

    EDIT: people keep downvoting me like I’m bootlicking or disagreeing. I’m actually trying to understand what the suspicion actually is over ending sideloading. There’s definitely a security case to be made, but people don’t seem to buy that. What actually ARE you thinking?

  • source
  • parent
  • [–] 197 points 1 year ago (12 children)

    Since Google’s goal is to improve security

    This is an obvious lie.
  • source
  • hideshow 12 child comments
  • [–] 24 points 1 year ago (4 children)

    They never specified who’s security…

  • source
  • parent
  • hideshow 4 child comments
  • [–] 6 points 1 year ago (2 children)

    Whose*

    Who's = who + is

    Whose = an indication of possession

  • source
  • parent
  • hideshow 2 child comments
  • [–] 44 points 1 year ago (6 children)

    they want to improve thier AI and datamining capabilities.

  • source
  • parent
  • hideshow 6 child comments
  • [–] 5 points 1 year ago (5 children)

    What am I not seeing? How does this improve datamining capabilities?

  • source
  • parent
  • hideshow 5 child comments
  • [–] 25 points 1 year ago (4 children)

    Target can track your purchases when you shop at Target, but can't really do that when you're shopping at a local store. Same applies here.

  • source
  • parent
  • hideshow 4 child comments
  • [–] 2 points 1 year ago (3 children)

    But you can't shop at Target with some random app, only the Target app. Even a small business has an accessible pathway to publish their app. Besides Fortnite and my gimbal nobody out here trying to educate customers on how to install their apk file.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 4 points 1 year ago (1 child)

    They mean a physical Target store, not a phone app. Target can track customers walking in and out the door and what they buy, how long they stay, etc. but they can't track anything about you if you just go to a different store, especially something like a small business which isn't hooked into the ad data sponge.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 300 points 1 year ago (14 children)
  • [–] 82 points 1 year ago* (last edited 1 year ago) (1 child)

    It is, because it's actually the term that defines the process of transferring files not from an external networked device - downloading - or to an external networked device - uploading - but between two local devices - sideloading.

    It's over two decades old, you downloaded an mp3 from kazaa, and then sideloaded it to your player.

    For android apps, I believe the term originates from the method of using ADB to directly write the app to the phone memory, the command of which is "adb sideload filename"

  • source
  • parent
  • hideshow 1 child comment
  • [–] 38 points 1 year ago

    And companies ofted do it. Thay recoined jaywalking to put the blaim of the accidents to pedestrians and take away the road from them. They change what littering means in attrmpt to delute the responsibility for polution... We are better than that this time, right?

  • source
  • parent
  • [+] 60 points 1 year ago (4 children)
  • [–] 12 points 1 year ago (2 children)

    And "littering" is the "real" culprit why we all drawn in uneccesey plastic. We should blame consumers not the polluters.

    Corporations do it all the time.

  • source
  • parent
  • hideshow 2 child comments
  • [+] -17 points 1 year ago (6 children)

    Don't forget "side effects", when really, medications only have "effects". Whether the effects are intended or not doesn't change the fact that they happen.

  • source
  • parent
  • hideshow 6 child comments
  • [–] 31 points 1 year ago

    Cough medicine can induce drowsiness, but you probably shouldn't be taking it as a sleep aid. The distinction between intended vs unintended effects is an important distinction to make, in my opinion, to prevent drugs from being unintentionally misused.

  • source
  • parent
  • [–] 5 points 1 year ago (1 child)

    you shouldnt be taking medication not for his intended purpose, it has many warnings.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 3 points 1 year ago

    Talking to the wrong guy here, I've taken many a medications against their intended purpose: I am a curious guy.

    But that sounds like saying, in the context of Google's intention of disabling app sideloading, that warning users that it poses a security risk because it's their intended purpose for android, is fine because the authority on android is Google.

    Don't just take the word of authority at face value, when they prioritize profit and mindshare over personal freedom.

  • source
  • parent
  • [–] 3 points 1 year ago* (2 children)

    Wait, so now I have to talk to a doctor before installing from F-Droid? Well, shit.

    For all intents and purposes, your comment actually invalidates the premise of using 'sideloading' as a term for installing from outside the 'official' method.

    You buy cough syrup because you're coughing, not because you want to be drowsy (I would hope that's the case). In the same way, you install Spotify to listen to music, not to get all your data extracted and sold. Getting drowsy is an inconvenient side effect of the medication, the same way that data grab and ads are an inconvenient side effect of the app.

    You're not 'side-medicating'.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 2 points 1 year ago

    You are the master of your body, the person who decides ultimately what goes in and out of your body, No doctor can force you to take anything. That's what I mean, The play store aka the doctor wants to become the master that decides what apps go in or out of your phone, instead of the user. My comment doesn't invalidate the premise of the use of the term sideloading, because I don't agree with the term to begin with.

    Whether the effect is ideal or not does not change what is chemically happening in the body. The body can't tell apart side effects from the main ones, so this distinction exists because humans deemed it so, just like the distinction between play store sanctioned apps, and everything else. It's a distinction that Google is now abusing for it's own monetary benefit.

  • source
  • parent
  • [–] 62 points 1 year ago (23 children)

    If Google wanted to add developer verification without being evil, it could use SSL certificates connected to domain names. I think the whole concept is ill-conceived, though I'll admit to a modest bias against protecting people from themselves.

  • source
  • hideshow 23 child comments
  • [–] 3 points 1 year ago (5 children)

    They couldn't. Domains and SSL certificates can be obtained very easily anonymously and thus wouldn't let Google identify the developers of malicious apps, which is the goal of this

  • source
  • parent
  • hideshow 5 child comments
  • [–] 28 points 1 year ago (2 children)

    The trouble is Google’s definition of malicious apps. Are adblockers malicious? How about alternative apps for YouTube? Based on the recent history, I don’t think you will be able to install those apps on the phone you purchased.

  • source
  • parent
  • hideshow 2 child comments
  • [–] -2 points 1 year ago (16 children)

    The problem with that is that certificates expire before someone would want to keep using the app.

  • source
  • parent
  • hideshow 16 child comments
  • [–] 5 points 1 year ago (4 children)

    Code signing certificates work a little differently than SSL certificates. A timestamp is included in the signature so the certificate only needs to be valid at the time of signing. The executable will remain valid forever, even if the certificate later expires. (This is how it works on Windows)

  • source
  • parent
  • hideshow 4 child comments
  • [–] 1 point 1 year ago (3 children)

    Doesn't work, the reason they can expire is to make certificate rotation possible. If an expired ssl certificate is cracked it doesn't matter because no browser will accept the expired certificate, with your idea the expired certificate just signs an app with the date of 1984 and it works.

    Certificates in SSL can't change the date because that date is signed by a certificate higher in the hierarchy.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 2 points 1 year ago* (last edited 1 year ago) (2 children)

    This isn't "my idea", this is how the industry already does code signing. You can't sign something with a date of 1984 because your certificate has a start and end date, and is usually only valid for 1 year.

    You can read more about how this works here: https://knowledge.digicert.com/general-information/rfc3161-compliant-time-stamp-authority-server

    https://en.wikipedia.org/wiki/Trusted_timestamping

  • source
  • parent
  • hideshow 2 child comments
  • [–] 2 points 1 year ago (1 child)

    Then you need a Trusted Third Party, right? Still requires some though on how to prevent that third party from blocking applications they don't like but I can see how a group of trusted authorities could work.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 2 points 1 year ago

    The trusted 3rd party in this case is actually multiple 3rd parties. There's several options for trusted timestamping just like there's multiple trusted root CAs for SSL. Since the timestamping service is free and public, anyone can use it to sign anything, even self-signed certificates. There's no mechanism to deny access, at least for this portion.

    There's always a risk the root CAs all collude and refuse to give out certificates to people they don't like, but at least so far this hasn't been a problem. I don't have a better solution unfortunately. If we could have a 100% decentralized signing scheme that would be ideal, but I have no idea how you would build such a thing without identity verification and some inherit trust in the system

  • source
  • parent
  • [–] 5 points 1 year ago (10 children)

    It need only check at install time.

  • source
  • parent
  • hideshow 10 child comments
  • [–] 4 points 1 year ago (9 children)

    Correction: SSL certificates can expire before someone would want to continue being able to install any given app.

  • source
  • parent
  • hideshow 9 child comments
  • [–] 5 points 1 year ago (7 children)

    Sure, the developer needs to keep the certificate up to date and re-sign the APK on occasion.

  • source
  • parent
  • hideshow 7 child comments
  • [–] 3 points 1 year ago (6 children)

    So any APK I download will just expire at some point in time that's probably really annoying to know, and then I have to dig through the internet again so I can install the app again?

  • source
  • parent
  • hideshow 6 child comments
  • [–] 1 point 1 year ago (4 children)

    Another option is to allow otherwise-valid signatures after expiration. It's generally still possible to check them.

  • source
  • parent
  • hideshow 4 child comments
  • [–] 1 point 1 year ago (3 children)

    That completely nullifies the entire point of signature validations.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 1 point 1 year ago (2 children)

    How? Expiration doesn't grant an unauthorized party access to the private key.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 1 point 1 year ago (1 child)

    There's zero cryptographic reason to have a signed date at that point.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 1 point 1 year ago

    Which nullifies the point of certificates having an expiration date (limited window for exploiting a compromised certificate, possibility of domains changing hands), not the point of validating the signature (tie responsibility for apps to who owned a domain on a specific date, allow third parties to create blacklists of bad developers).

  • source
  • parent
  • [–] 54 points 1 year ago (10 children)

    This is actually worse than integration in Play Protect which can be disabled very easily. Now you can only install unsigned apps via ADB which means just developers can do it.

  • source
  • hideshow 10 child comments
  • [–] 30 points 1 year ago (3 children)

    And very annoying too since some government apps don't like it when you have developer mode on.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 20 points 1 year ago (2 children)

    Not only government. I can't see my daughter's insulin pump status if I don't disable developer mode.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 15 points 1 year ago (3 children)

    Or anyone with a computer who installs ADB. You don't have to be a developer.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 6 points 1 year ago (2 children)

    Nah you can't realistically distribute your app with adb requirement. No one will bother to go through such friction.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 8 points 1 year ago (1 child)

    Leaving ADB open to unverified apps is more than I was expecting. ADB is reasonably straightforward to use even without actually being an Android developer.

    There was never any way they'd integrate it to play protect and still allow play protect to be disabled. I prefer this to being required to use play protect personally, though the services do seem somewhat redundant. Presumably the whole point of doing this is to create an Apple style walled garden (which is of course very profitable). Google likely doesn't want to fully lock it down and risk legal trouble, they just need to make it difficult enough that the masses don't bother installing unapproved apps that may not act in Google's interests.

    I still hope the EU takes legal action against this anyway.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 6 points 1 year ago

    I don't think this adds anything tbh as peoppe with adb would always be able to bypass this. The issue is that this kills distribution and thats exactly what Google wants - have full competitive control. Once they don't like your app they'll block your account and what do you do with your customer base? Give them adb install instructions? That's basically a death sentence for any app.

  • source
  • parent
  • [–] 109 points 1 year ago (7 children)

    I'm not sure why google is over engineering this, proper mainline distros have this solved since forever. Let the community setup trusted repos with gpg keys, then let me trust the repos. If Fdroid trusts the package and I trust Fdroid, who should care?

  • source
  • hideshow 7 child comments
  • [–] 119 points 1 year ago (5 children)

    Probably because they want to target software that cracks theirs to avoid ads, like ReVanced.

  • source
  • parent
  • hideshow 5 child comments
  • [–] 7 points 1 year ago (4 children)

    Then why aren't they already doing that by blocking DuckDuckGo?

    The DuckDuckGo app blocks all apps from sending to Google (and other advertisers) tracking/ad data on a system level. And it's freely available on the Play Store (has been for years.

    https://play.google.com/store/apps/details?id=com.duckduckgo.mobile.android

    If they wanted to prevent apps from blocking their ad abilities, this app would never have been allowed on the Play Store.

  • source
  • parent
  • hideshow 4 child comments
  • [–] 8 points 1 year ago* (last edited 1 year ago)

    Does it actually block ads in apps?

    Blokada 5 blocks ads in apps and it was removed from the google store years ago. You have to sideload it in order to use it.

    There's a neutered version on the google store, but it doesn't block ads effectively.

    Google also removed an addon called Adnauseam, which clicked ads in additional to blocking them. That way, advertisers still have to pay site owners for your visit. Google removed it without justifiable reason, then kept it removed since there was no sufficient backlash.

    It's the main reason why I switched to Firefox. That kind of abuse is for useful idiots.

  • source
  • parent
  • [–] 49 points 1 year ago (1 child)

    We hope that Google keeps its word and preserves ADB installation

    lol, adb is the first loophole that will be closed.

  • source
  • hideshow 1 child comment
  • [–] 33 points 1 year ago* (13 children)

    why can google not just code something like this into android:

    allow apps from:
    ( ) All sources (how it is now; allow each app to install apps from external sources)
    ( ) Just Google Play
    ( ) Apps which have been verified by Google Developer Program

  • source
  • hideshow 13 child comments
  • [–] 9 points 1 year ago* (6 children)

    Taking Google at their word for a moment, it's far too easy to scam the clueless masses into selecting the first one. Might work okay if it's strictly an ADB command, tho.

  • source
  • parent
  • hideshow 6 child comments
  • [–] 10 points 1 year ago (2 children)

    I'm inclined to think that's not the job of an OS vendor to prevent. Sure, put a warning label on it, but it's the user's device; once they say they know what they're doing, that should be that.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 4 points 1 year ago (1 child)

    The implication here is, if they implement this, is that they volunteer to assume liability, should e.g., your bank account be drained despite undergoing their forced strict lockdown on paid and owned devices.

    Fat chance, because laws are meaningless to crime syndicates

  • source
  • parent
  • hideshow 1 child comment
  • [–] 6 points 1 year ago

    It might be a reasonable trade for users to make if Google assumed liability. In fact, that would be an interesting way to implement laws to discourage practices like these.

  • source
  • parent
  • [–] 1 point 1 year ago (1 child)

    but they could make it be google play or samsung store only as the default as a compromise

  • source
  • parent
  • hideshow 1 child comment
  • load more comments (1 reply)
  • [–] 4 points 1 year ago

    I can see it already:

    () Just Google Play (safe)

    () Verified apps (not recommended)

    Advanced settings

    click on Advanced settings

    () All sources (Unsafe. Will probably kill your cat and burn down your house)

    tick the box

    Are you sure?

    click yes

    ARE YOU SURE?

    click yes again

    ONE HUNDRED PERCENT SURE?

    wait for the 30 seconds timer to count down

    click yes

    ( ) I do not love my cat and want him to die.

    tick the box

    ( ) I accept the very real risk of my house burning down

    tick the box

    Please wait 24 hours for the change to apply. You can reverse it at any time from this menu.

    get spammed every hour for the next 24 hours with notifications asking me to fix my security settings

    get a bigass ⚠️ every time I turn on the phone

    every once in a while the change just straight up reverses and I have to do it all over again

  • source
  • parent
  • [–] 17 points 1 year ago (4 children)

    We should embrace oldschool SciFy and go for (DIY) Cyberdecks.

  • source
  • hideshow 4 child comments
  • [–] 11 points 1 year ago (3 children)

    Thankfully, for those of us without the time for all that there are Linux phones such as this one I'm considering.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 3 points 1 year ago (1 child)

    I’d love to play around with something like this, as a programmer myself, but unfortunately the cost is prohibitive in my country.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 2 points 1 year ago*

    Yeah, that's why it's still in the "considering" phase for me as well - especially considering Trump's tariffs crap. It also seems a tad underpowered for the price, and they still don't have the promised removable battery replacements in their store.

    It's worth remembering, though, that the cost covers the constant software updates, as well as their user support. As such, it's much like the Apple model of business, except much more open - so in the end it's probably worth it.

  • source
  • parent
  • load more comments
    view more: next ›
    1 comment in c/android@lemdro.id view that post