[–] [S] 13 points 4 hours ago (1 child)

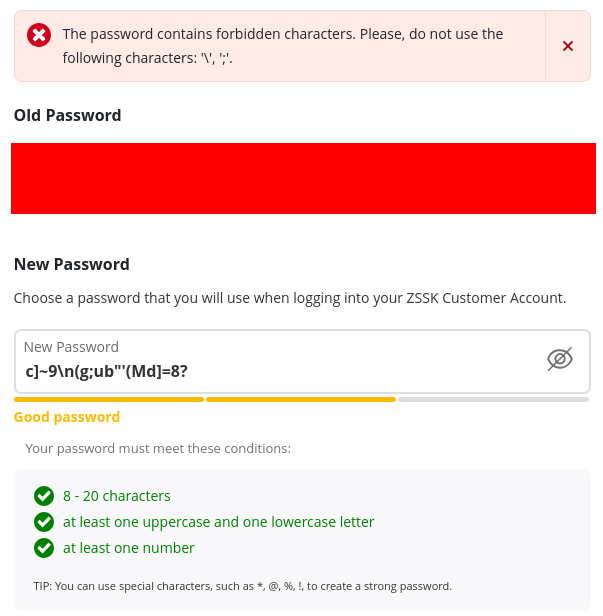
My bank doesn't support any special characters in the password, and letters are case-insensitive. At least the limit is 30 characters, so that's still good enough. Though I really wonder what kind of system doesn't differentiate uppercase and lowercase letters.

Yet, somehow, they did implement OpenPGP for e-mail signing and encryption.

  • source
  • parent
  • context
  • [–] 9 points 11 hours ago (2 children)

    OS tooling

    I was once writing an assignment last minute. On a full train. Where I could only use my phone while standing.
    Not the best experience, but using Vim and LaTeX in Termux is pretty doable.
    Although in that case I didn't have LaTeX directly on my phone, instead I SSHd into my computer, and then rsynced PDFs to preview the document. But TeX Live is even in the Termux repository, if you want. After all, you can SSH into your phone just the same.

    Termux is awesome. I sometimes even use it to off-load stuff I don't want my computer to be choking with, such as large downloads, video encoding or compressing large files with high xz settings.
    It's just a battery-powered highly portable passively cooled computer.
    But of course, a full-fledged Linux phone would be even better.

  • source
  • parent
  • context
  •  

    One one hand, if I lose the database or manage to forget that password, I am fucked.
    On the other hand, that's also the case with 2FA.

    The latter has already happened to me, but I have since switched to different software that lets me properly manage backups rather than doing only cloud bullshit.
    Cisco Duo. That piece of shit doesn't even do version control.
    I just turned on an old phone, and there goes my backup, overwritten by old data.


    Recently I finished my switch from memorized and re-used passwords to KeePassXC and KeePassDX based on recommendation of other Lemmy users, and I like the workflow.

    In a similar fashion, I also recently purchased a domain name, and set-up paid e-mail account(s) at Purelymail with that domain.
    I use Thunderbird on desktop and phone for now.

    It's OK-ish on desktop, but the phone experience is poor.
    On desktop, during set-up it requires filling fields such as "Full name" to continue, which can even be deleted later. Thankfully, there is some advanced option to skip guided setup after this.

    On a phone, the name field is equally mandatory, only to then be flagged as "Optional" in settings after setup.
    It also requires BOTH IMAP and SMTP. Not only that, it verifies that the SMTP server is valid and the user can be authenticated (I didn't try without IMAP).
    Trying to load that account via export from desktop shows an "invalid data" error.
    Furhtemore, I can't receive e-mail notifications.
    I have them enabled, I allowed necessary permissions, there is a permanent notification stating it works, RethinkDNS shows active connection to the IMAP server, when I open the app, the e-mail is immediately there.


    I've recently registered a .eu domain name.

    EURid registry has a portal where you can generate a transfer code, thus not fully relying on access to registrar (as well as check and verify your info).

    Welp, security.

    The only security is a code sent to e-mail associated with the domain. While the portal requires entering this address to log in, it can also be pulled from WHOIS where it is mandatorily published.
    Regardless, e-mail (as a string) should not be affecting security.

    The code, as I mentioned, is just lowercase letters and numbers. Precisely 6 of them. This is valid for 2 hours and one use.
    While there is a "Request new code" button, I wasn't able to generate multiple codes for one 2 hour window, so that's good.

    But now we get to rate-limiting. After 9 attempts, I get:

    You have exceeded the allowed number of requests.
    Please try again in 10 minutes.

    Sounds good, BUT, clearing cookies bypasses this.
    I have not (yet) tried any automation, I just quickly manually repeated this tomfoolery from same IP 3 times without actually being rate-limited.


    I find this... at least strange. Especially since everyone is doing at least 2FA, while some sites even support physical security keys, and then there's "we email you 6 characters".


    So many online services, so much legal information, usually written in confusing ways.

    For example, in data processing addendum, Porkbun uses the term "Controller", which is defined as:

    (d) “Controller” as used in this DPA, means Customer.

    Why not just call it Customer?

    Worse yet, just like many services, Purelymail has this in their ToS:

    The Company reserves the right to change this agreement at any time. You are responsible for regularly reviewing these Terms. Continued use of the Service after such changes shall constitute your consent to them.

    In this case, there isn't even a date of last update. Am I supposed to have some scripts scraping all legal documents of most services every hour and comparing checksums to figure out if something has changed?

    But how should I even keep track of legal agreements of many many companies including any affiliated third parties I implicitly agree to use?

    Because it sounds like I should also be concerned about those:

    Sub-processors authorised under Section 7 of the DPA process the personal data described above for the purposes listed above and only for the duration necessary to perform the sub-processed activity.


    If I was to read, understand, and keep track of everything, I feel that would in fact just become my full-time job. Especially since they often also reference laws, something I would also need to know and understand.

    Subject to applicable law [...]

    Which is what?


    Assuming a password manager is used, even jfav0ohjau4gvncgan19@domain should be OK.

    On the other hand, I might just be overthinking it. It could even look suspicious to customer support, or is that again just overthinking?

    Also, there already will necessarily be some predictable ones, such as work@domain, although servicename@domain would provide even more possible matches.


    I couldn't find any mention of this issue and I kept fucking around with it for an hour.

    Disclaimer: I am dumb.

    Symptoms

    After reaching end of track on its own, playback won't continue. The UI remains responsive, but with no effect.
    Dragging slider all the way to the end of a song behaves as expected, without issues.
    Running VLC with -v 3 provides no additional information.
    Closing VLC GUI will not stop VLC, neither does signal 15 (sigterm), only 9 (sigkill).
    After downgrading VLC (and associated vlc-* packages), the issue persists.

    Solution

    Switch away from pipewire ALSA audio device or away from ALSA altogether (recommended).

    Switching ALSA to different device

    GUI

    The drop-down "Audio" menu doesn't appear to persist settings.
    Instead, navigate to Tools -> Preferences, in bottom left corner under "Show settings" select "All", then on the left, under "Audio" expand "Output modules", select "ALSA" and finally change "Audio output device" to something else than "PipeWire Sound Server" (e.g.: "Default") and click "Save" in the bottom right.

    Config file

    The file lives in ~/.config/vlc/vlcrc.
    Search for alsa-audio-device=pipewire, and change pipewire to something else.
    Example:

    # Audio output device (string)
    alsa-audio-device=default
    

    Switching from ALSA to PulseAudio

    Or at least the option says PulseAudio, this is probably pipewire-pulse since I don't use PulseAudio.
    Anyway, this will also show VLC in list of playback applications, as well as allow for multiple audio sources to output at once (rather than exclusive access to audio device).
    Basically same as using PipeWire ALSA "device".

    GUI

    Navigate to Tools -> Preferences, in bottom left corner under "Show settings" select "All", then on the left select "Output modules", and change "Audio output module" to "Pulseaudio audio output" and click "Save" in the bottom right.
    Then restart VLC.

    Config file

    The file lives in ~/.config/vlc/vlcrc.
    Search for aout=alsa, and change alsa to pulse.
    Example:

    # Audio output module (string)
    aout=pulse


    (Not the registrar. E.g., .com TLD is operated by Verisign.)

    I wanted a domain for my e-mail. Sounds simple.
    But I am a major overthinker, so over the period of past 2 weeks (damn!) I've been deciding between e-mail providers, choosing potential domain names, choosing a TLD (round 1 - by price and looks), looking through registrars, deciding whom to choose for nameservers, and now I am comparing registry operators (TLD round 2).

    There are differences, such as who can register a domain, restrictions on domain privacy, and some TLDs like .dev are on HSTS preload list.


    Currently, I am mostly looking at EURid with .eu TLD.
    What piqued my interest is being able to transfer a domain directly through the registry. So, if a registrar locked me out or shut down, I could still transfer my domain.
    From EURid:

    From your registrar: Your first point of contact should be your registrar.
    From the My .eu platform: You can also issue the transfer authorization code yourself on the My.eu account.
    From EURid: This should be done only as a last resort. After proving you are the holder of the domain and cannot obtain an authorization code from your current registrar or via the My .eu platform, you can request an emergency transfer authorization code directly from EURid

    Alright.
    But I must wonder, how do I prove my ownership?

    First sign that this may not be that secure is right on the same page:

    Print the form, sign it and send it to us via email at authcoderequest@eurid.eu. If the requester is an organization, please print the form on company letterhead paper or add a company stamp.

    OK, the form. Here's the request page. Fields are domain name, first name, last name, job title, email address, and reason for the request.

    I generated the form to see what's there. So... is this the security?:

    I hereby confirm that I am the rightful holder of the domain name mentioned above, or that I have obtained the legal power to represent the holder, and that all data provided is true and correct. I am fully aware that making a false statement in this matter is considered fraud and may have judicial consequences.

    I mean, it doesn't even sound like they collect your signature during the verification, not that a picture provides much security. This is one of the methods:

    You can receive a small bank payment (less than one euro) from EURid, which includes a 10-character code that starts and ends with “EU”, with six digits in between (EUXXXXXXEU). After receiving this payment, the domain holder logs in to the My .eu platform and enters the code to verify their registration data.

    Either way, it seems this might be mitigated by registry lock:

    The Registrar Lock Service will also protect your domain name from accidental changes, but the difference from Registry Lock is that a locked domain name can still be transferred with an authorisation code sent to your My .eu account or an emergency authorisation code received from EURid.

    Enough about safety. What about privacy?
    The T&C [PDF] prohibits the domain having info of the registrar:

    Your registration data must be your own data and must not be that of your Registrar, or of a proxy holder or a representative of a natural person or legal entity who does not meet the eligibility criteria. You may at any time check your registration data via the web-based WHOIS or the secure registrant portal available on our Website.

    But it gets a bit better in the WHOIS policy [PDF]:

    When the Registrant is a natural person the Registry publishes the Registrant´s e-mail address and language.


    Alright. I hope there's someone else who took a similarly overcomplicated route in choosing a domain name.


    Possibly it would make more sense to ask on the 196 community based on the company's energy.

    Anyway, I was browsing EURid's list of registrars, and this company's logo took my attention. However, I can't find any experiences online.

    I've checked through their websites, and so far my feelings are a bit mixed. Although most of it is just outdated or somewhat inconsistent bits across their websites.

    Things that make me unsure

    First and least important is info about one of the people behind the company, "Alfie". Links on the about page are just completely outdated and dead. Website link in docs is at least alive, but also outdated, as can be seen by navigating in manner of URL in docs -> keybase -> GitHub -> newer website.

    Second, the "Email us" button on the contact page redirects to a contact form, which really contradicts the text below:

    If you want to send us a PGP encrypted email, please use the below key. Remember to attach your own key (as application/pgp-keys), so we can encrypt our reply to you.

    That sounded so cool when I've seen it, but what e-mail address?
    The contact form is on a "support" subdomain of their other website. This seems to be centered around the contact form, but there is also a "Manage PGP keys" button which redirects to a login page.
    Maybe they migrated to that?
    But then going to contact page on the domain's second level does show an email, as well as linking to the same contact form.

    Third, in the list of services, there's also "Email"... which presents a self-signed certificate. Ignoring that, there's just an "Unknown URL" error page.

    We're probably not responsible for this domain.

    Lastly, and most importantly, right on ther main page it says:

    Proxy registration for .eu

    And that's the only mention of that feature. But what is it? If following ICANN's definition...

    Proxy Services – Proxy services allow a domain name to keep certain identity and contact details from appearing in public Whois information. The proxy service becomes the registered name holder of record, and its identity and contact information is displayed in Whois data.

    ...it might be a problem. Because, let's take a look at T&C of EURid (PDF):

    Throughout the Term of your Domain Name registration, you must: [...] b. keep your registration data accurate, complete and up-to-date at all times. Your registration data must be your own data and must not be that of your Registrar, or of a proxy holder or a representative of a natural person or legal entity who does not meet the eligibility criteria. [...]

    There's also an annoying requirement for tax reasons, but that's not their fault:

    In short things are about to get a lot more complicated. We will need to collect at least two pieces of non contradictory evidence about which country you’re resident in, so we can pay the correct tax authority.

    And what caught my attention (in a good way)

    As I've said, I checked them based on their logo. That's not a usual company logo.

    Pricing for .eu TLD is OK.

    Their ToS is short.

    One button on bottom says "there's no ai here!".

    Looking at the about page, this seems to be a small company operated by 2 people.

    Looking at their mailing list archive, they've used to have a VPS service, gave shutdown information in advance (though less than 2 months), and set-up a migration route with another provider.
    They've also informed about a security incident at one of their registries.

    WHOIS privacy includes email forwarding from a funny domain name:

    If you do not select it we will generate an anonymous @owowhosth.is email and publish that instead.

    On their Mastodon, they describe themselves with

    On a mission to make interneting a little easier, join us at http://glauca.digital/. Possibly anarchist, definitely antifascist.

    Oh, and speaking of Mastodon, that is listed as one of their services. Based on this disclaimer...

    MOBILE APP USERS: if you're trying to sign up with a mobile app go back and select login to authenticate with our SSO.

    ...it does indeed sound like being their customer includes account on their Mastodon instance. Pretty cool if true.

    Also, try whois with their ASN:

    aut-num:        AS207960
    as-name:        AS-TRANSRIGHTS
    descr:          Trans Rights! Hell Yeah!
    [...]
    remarks:        ----------------------------
    remarks:        Hmmmmm tasty routing policies...
    remarks:        ----------------------------


    In the past when deciding between VPN (as in proxy) providers I went with Mullvad because their ToS and Privacy Policy was by far the shortest.

    So just the same I now checked all the related links, copy-pasted all the text into Writer (to use as a simple word counter), and found that Cloudflare sits at 22,490 words while Porkbun at 22,554 (excluding contact info).
    So that's not helping me make the decision.

    The most commonly quoted average reading speed is 238WPM, so that's around 95 minutes each...
    ...after which I should remember enough to compare them. Or take notes.


    It's already both happened to me that I didn't notice I couldn't move a piece without exposing the king or that I won by accident. Had the game not announced this, I wouldn't have known.

    And perhaps the opponent might not notice my mistake either. Or it could just be a strategic high-risk scenario, rather than a mistake.

    view more: next ›