I was at a restaurant earlier this year, and I actually saw someone take a picture of their food, screen shot that picture, and send it on their messaging app of choice. Was so cool seeing it happen in person in my tiny town, and not just in the big cities or the internet
post
I’m pretty sure Lemmy strips it
Feels like an honorable site would make the uploader aware of this and offer a checkbox or something to do it for you.
Every social-media platform strips EXIF metadata before publishing the photo.
So the issue is the trustworthiness of the social-media platform itself. Personally I always strip the metadata before sharing anything anywhere.
Of course they strip it before publishing and of course they use the stripped data for themselves. Anyone assuming that they won't should come and buy that bridge that I'm selling, it's a great opportunity!
Strips metadata so that the public can't see it, isn't the same as stripping metadata after the corporation has already collected and linked it to your profile. 😫
Always clean the metadata BEFORE it touches their upload UI.
Sure, but let’s say you don’t allow Facebook to track your location. Well, as soon as you upload a photo with location exif data, they know it anyway.
While this is true, especially with all the Palintir tracking stuff and the insatiable thirst for data to market, it's far more valuable now than ever to the platform. The platform is happy to keep it and sell it to marketers who will share it for you.
This. Literally every social media site strips EXIF data from photos you post or else you would be hearing about 100x the number of doxxes you do these days. This tip would've been good in 2006 or if you're communicating over something unusual like Email or Onionshare
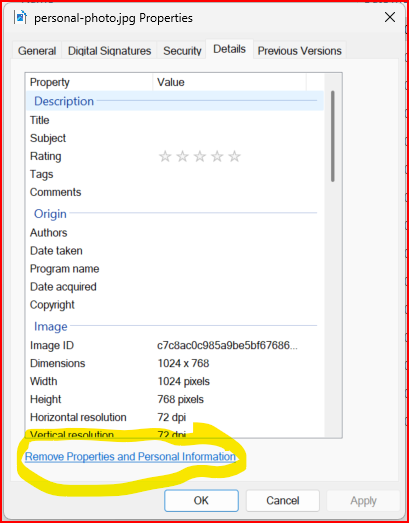
Frankly I would extend that distrust to this little miscrosoft button too. With no proof or alternative in mind, it just feels like that button would feed the data to an AI before deleting it.
For iPhone you can make a simple shortcut to do this. Here’s what it would look like:

Thanks for that. I’ve made one exactly as you describe. Anyone can download it here https://www.icloud.com/shortcuts/9adfbc6f62084faa81fbe5da71515a7b
For linux I use exiftool
exiftool -all= image.jpg
Can it be made into a Cinnamon extension or even a tool with which I would run it for all new image files while idle (if needed)?
I discovered that recent versions of the built-in photo apps on Android flat out refuses to do this. The UI for removing location info is there, but it is intentionally blocked if the exif info was added automatically by GPS (i.e., it only works if you manually have set a location). It seems so weird, and outright evil, to block one of the key ways for people to stay safe.
Scrambled Exif has served me well.
Alternatively, you can (probably should) decide to not upload any photo to social media.
That would destroy the majority of Lemmy though
The data is different for a 'photo' one took vs one of many other types of image. Your camera/phone can often include a lot of surprising data, possibly even your PII or location. An image you made in krita or with a screenshotting tool is somewhat less likely to have such data.
What the actual hell is all that?
Check their history. They are stalking and harassing a couple of users they have a disagreement with.
Dude, block them and move on. It's not healthy to obsess about stuff like that. It's just adding stress that you could easily avoid.
I read through that conversation. They didn’t doxx you. You appear to be having some sort of mental health crisis, maybe log off the internet for a bit and talk to someone you trust.
I really think you should reach out to a friend or family member.
Use the block button and move on. Otherwise you are breaking Lemmy's harassment rules.
Then report their comment and move on. This form of "consequence" is but harassment that doesn't cast you in a good light either. We all have bad days, we all get agrivated by things sometimes. If you need someone to vent with you can message me directly if you like, but I would advise taking a step back after reporting the original comment because you may look back on this as them being mean, but regret your actions as well.
Pretty sure posting the exact same unhinged comment 100 times is not going to get you anywhere that posting it...uh...once?...would have.
That said, maybe screaming into the void is your idea of a good time.
You should be able to prevent your device from adding the location to your photos. I never felt the need to have it, given the date and the photos around, it is easy to remember where it was.
By default I always turn off the location setting on the camera. I disabled it as soon as they introduced it as a "feature". I thought it was creepy as fuck and dangerous. Without the location most of the rest of the information is pretty benign.
For example her is the full metadata from a picture I took yesterday.
Aperture: 182/100 Date: 2025-07-30 15:40:26 Date digitized: 2025-07-30 15:40:26 Original date: 2025-07-30 15:40:26 Digital zoom: 1.0 Exposure bias: 0/6 Exposure mode: Auto Exposure program: Normal Exposure time: 4.7824007651841227E-4 sec. Flash: Off Focal length: 5590/1000 35mm focal length: 24 F-number: 1.8 Image width: 2304 Image length: 4096 Lens model: OnePlus 13R back camera >5.59mm f/1.9 Light source: D65 Camera make: OnePlus Camera model: OnePlus 13R Camera maker note: {"PiFlag":"0","nightFlag":"4","nightMode": "-1","asdOut": ["0"],"apsAsdOut": ["1"],"apsAsdClsOut": ["1", "0"],"iso": "286","expTime": "0","fType":"50","bkMode":"0","aideblur":"0","aisState":"8","algo": ["65,72,16,19"],"filter": ":-1"} Lens max aperture: 182/100 Metering mode: Center weight average Orientation: Normal Photographic sensitivity: 80 X dimension: 2304 Y dimension: 4096 Scene capture type: Standard Scene type: Directly photographed User comment: oplus_2097184 White balance: Auto
The only thing they would get is the model of phone I use. Which is essentially public information for every app maker I have installed on my phone anyways.
Yes, but the company could still keep the data somewhere.
You guys are uploading personal photos to social media?!
That's how 99% of social media works
There are a million ways to do this, as have already been described in other comments. This is one more. I built https://photostripper.com/ a while back, when I was practicing building small web applications to learn different tech stacks. Lemmy is not the target audience - you folks know how to do this already, and why would you trust that I’m not keeping copies of your photos (I promise I’m not, but what is that worth?)
Anyway, I’m only mentioning it because it’s my thing and I enjoyed making it.
https://guardianproject.info/apps/org.witness.sscphase1/
Above you will find the link for an app called a obscure cam. It's open source and made by the Guardian Project. It allows you to sensor faces and automatically removes exaptata from your photos so that you don't put your geolocation on dating apps.
If all of the Tea users used this, that breach wouldn't be even a quarter as bad. Also would help if they didn't post their fn drivers license to a dating app.
I haven’t looked into this, but if it doesn’t already, Lemmy and PieFed should scrub this data before writing it to disk. Would be a lot easier to implement this in one place than teach everyone to scrub the data themselves. If either of them don’t do that, we should put up a feature request.
most social media sites already do that for you . Unless you upload the image as a document, most media sites automatically remove the exif and compress the img.
I run it through my 1995-era photo editor that doesn't support all the metadata.
Also on mobile what works for me when uploading a photo, I generally screenshot and upload that screenshot. Never upload the "original" photo.
I've always been curious how one could verify that all that exif data was certainly removed fully
There are EXIF data viewers. You can just look at it. ExifTool and so forth. You can also use it to remove such data if you don't trust Windows to do it for you.
At least a subset of EXIF data can be viewed in Windows Explorer in your file properties. Technically any device or app can store any custom field within the EXIF data so long as it fits within the data size limitations, so it's certainly possible there could be gumpf in there that Explorer won't display.
I bet there are some poorly-built automatic scrapers out there harvesting EXIF tag data and not being too careful about sanitizing what they find.
ehhh
Screenshot
Paste Screenshot
Works on all platforms
Apple puts a little exif data in there, but it's not very useful data.
On linux you should use exifcleaner. The amount of info exiftool can pull from your photos is shocking. I thought Signal exifcleans but not clean enough apparently
Since we're on Lemmy, most people probably use Linux. You can use mat2 for this. It's CLI tho
If you are on android: https://f-droid.org/packages/com.jarsilio.android.scrambledeggsif

all 74 comments