"The initial attack vector for these scenarios uses a malicious document. The malicious document contains a JSON-formatted malicious prompt that triggers the attack when the document is included in Copilot’s context. The prompt can be rendered as white text on a white background and in a small font size to conceal it from the victim. Since Copilot for Word strips all text formatting like color and font size before passing the text into the underlying Large Language Model (LLM), this text remains fully readable to Copilot even though the victim cannot see it.”

This is so silly. I can’t believe it worked until very recently (and probably still works, except not exactly in this way).

all 9 comments

sorted by: hot top controversial new old
[–] 37 points 3 months ago (6 children)

So this is what they meant when they said that thanks to AI even silly grandmas like me can be a hacker! I still remember how to change font colour and size in Word, time to earn billions of dollars 💰

  • source
  • hideshow 6 child comments
  • [–] 24 points 3 months ago* (5 children)
  • [–] 8 points 3 months ago* (4 children)

    She be fucken rollin in fridge magnets and quirky collectibles.

  • source
  • parent
  • hideshow 4 child comments
  • [–] 4 points 3 months ago (3 children)

    I just want to acknowledge that my comment is sandwiched between schmorpel and schipelblorp.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 2 points 3 months ago (2 children)

    Lemmy is a smorgasbord for user names.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 5 points 3 months ago* (1 child)

    I dont use Microsoft Word

    Is this basically clippy asking you if you want to write a letter, but with prompt injection?

  • source
  • hideshow 1 child comment
  • 2 comments in c/programmer_humor@programming.dev view that post
    [–] 6 points 3 months ago (1 child)
  • [–] 9 points 3 months ago

    It would seem so: https://www.theregister.com/security/2026/07/29/word-worm-crawls-into-copilot-spreads-chaos/5280588

    It makes sense: with LLMs and agents based on them, even plain text becomes effectively executable, so any document can carry malicious instructions. It's worse with complex document formats like DOCX, ODT, or PDF, since text can be hidden from the human eye and escape detection by review. Very risky tech...

  • source
  • parent
  • 2 comments in c/programmerhumor@lemmy.ml view that post
    [–] 9 points 3 months ago (1 child)

    An attacker places hidden instructions in a document that is later used as source material in Copilot for Word. Copilot may interpret those instructions as part of the user’s request, causing it to manipulate the document being drafted or edited. Copilot may then also copy the hidden instructions into the resulting document, turning that document into a new carrier.

    Its Bobby tables all over again! Sanitize your inputs please.
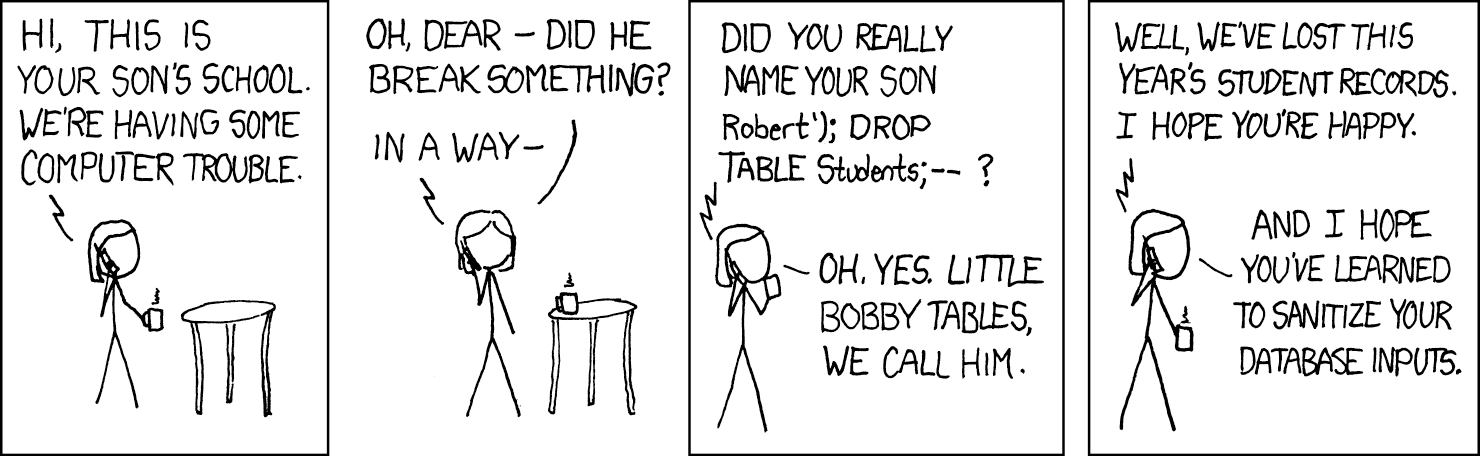
    The XKCD comic in question with the Bobby tables joke about not sanitizing inputs to SQL databases

  • source
  • hideshow 1 child comment