you are viewing a single comment's thread
view the rest of the comments
[–] 25 points 3 days ago (7 children)
  • [–] 8 points 3 days ago (2 children)

    Sorry, a kid in China tried to ssh into amazon.com, no shopping today!

  • source
  • parent
  • hideshow 2 child comments
  • [–] 5 points 3 days ago (1 child)

    After the '4' incident my calibration for guessing if something like this is a joke is completely broken.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 2 points 2 days ago

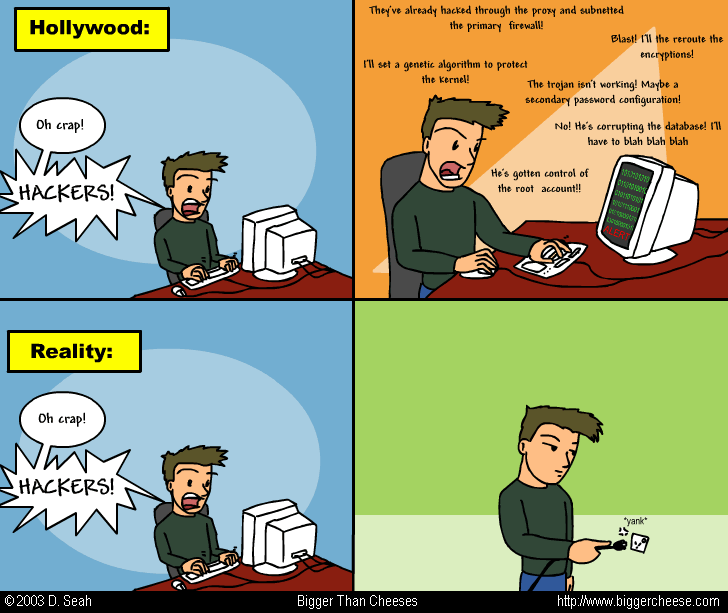
    My point is that hackers usually try to get into productive servers. You cannot just shut them down for every hacker attack, or you would never be online. You need to keep the business running while at the same time defending from attacks, so while the top scenario has a bunch of technobabble, it is more realistic.

  • source
  • parent
  • [–] 8 points 3 days ago (2 children)

    you set that root account to 'no' in the config, right?

    ... RIGHT??

  • source
  • parent
  • hideshow 2 child comments
  • [–] 1 point 3 days ago

    Remind me of a time where I was working in Asia and our instant messaging server went down because... it was a Windows server, the 2 elite IT guys were casually using it to go on Internet using the admin account to avoid all the limits put by the company (I guess porn...) and of course they managed to D/L a virus on the machine (I guess from a porn site...).

    Root config to no? Real men use root as their primary account to go where no one has should never have gone before on Internet!!

  • source
  • parent