Or my ad blocker for that matter. Sorry TV Tropes, I’ll miss you.
post
Your browser is unsupported. Switch to Chrome to enjoy the full experience.
Download our app to get the full experience.
Please sign in to confirm you're not a bot. This help protect our community.
Turn off ad blockers to access our website and help fund our data mining blog.
Access the full article for only $100 a month!
"Something went wrong. Try again later" (turn off VPN)
Xitter doesn't support strict tracking protection in Firefox.
Create an account to do this thing you don't need an account for.
Also we have 3 captchas and 7 MFA steps you must complete. Please verify your birthday and social security number.
blank white page after sign in, with password manager pop-up attempting to save a passkey
"Upgrade" to Windows to use this website.
This content is 18+ only and requires an ID/face/genital scan.
"Ask me later"
No, no, and have I mentioned no. Furthermore, fuck you.
Those newsletters you never signed up to, you click "unsubscribe", then the site you get directed to just happens to not function... block domain it is.
This app does not allow rooted device. Click here to see how to unroot.
Cookies: Click to accept all, or drop down where you painstakingly have to uncheck all bullets.
Every gadget needing internet access. Forced firmware updates.
I had this shit the other day. Legit laughed out loud.

That's because THEY FOUND MALWARE IN A RELEASE i saw a post about it yesterday. Think the devs have fixed it now but BEWARE if you had sensitive info on your device.
Could be one of the fake ones. Need to get it from the drv's git, not the websites claiming to be him.
SmartTube’s developer told me that the computer used to create the APKs for the project’s official GitHub page was compromised by malware. As a result, some official SmartTube releases were unintentionally released with malware.
The news post going around: https://www.aftvnews.com/smarttubes-official-apk-was-compromised-with-malware-what-you-should-do-if-you-use-it/
The new versions should be clean however:
Users who may have installed the malware-infected versions of the app are recommended to reset their devices and take additional steps to review their YouTube and Google account information. https://www.androidauthority.com/smarttube-malware-fix-3620773/
If you were logged into anything, probably best to change your password to be safe (and delete all sessions to unauth every device)!
Next time you see an alert like that, definitely research it before trying to work around it and install possibly infected software (i know there possibly wasn't any news when the alert went up, but i'd way a day then look it up again before continuing).
Ah, okay. Good to know. I dismissed the alert because it was after a recent update on the TV which also installed an Advertisement ID that allowed for AV ads on the home screen as soon as I turned it on. Definitely been in a "What bullshit is this now?" mode.
It's funny that the mindset has shifted to distrusting Google and Sony this much based on all the times they've tried to sneak things in or block the things that block them. Kind of like a persistent but low-level malware themselves, it's likely I'll dismiss/block their next attempt as I usually do. Having a warning from them is like listening to the boy that cried wolf, sort of.
Updated my shield and play protect disabled smartube, WTF. Fyi go to github and update smartube, because the original version signature was compromised and the developer has an alternate version.
blank white page after sign in, with password manager pop-up attempting to save a passkey
Haven't seen this one, not surprised. Seems sketchy as fuck.
100€ a month might be exaggerated but still.
Might as well require a log-in with a free* account (No monetary payment required, please don't read the part about data sharing in the TOS).
"That thing you use for security? Disable it before you come in. Come on, live a little, huh? 😏 Nothing bad's gonna happen. Pinky swear."
Yeah. Never you mind where the fuck I'm actually from. You don't need to know. It's funny how badly you want to know though.
Well, some companies are now using location data to jack up prices
So, the problem with VPNs is that the cheap ones / resellers have known IPs.
So if you use them you get lumped in with all the people using them maliciously.
If you run a site with any kind of desirable the content the crawlers and scripters hound you endlessly and eventually if you don't want it to be your full time job you just end up banning the entire IP/ ASN that the malicious traffic is coming from.
It sucks and if anyone has any solutions I'm all ears.
first, the ips of all vpn providers are known, the problem with the cheap/free ones is that they spy on you.
instead of blocking ips use proof of work for those sus ips https://github.com/TecharoHQ/anubis
(it's the anime girl that checks if you are a bot. :3)
it drives the cost of crawling at scale high up while being minor for individual, "legit" requests
all the cool kids are using it
Governments could actually shut down the scammers. They know who and where but they don't act.
From visiting Core77 and being active in the forums every day to haven't gone on once overnight
I have them in RSS and have no problem opening their links over Mullvad
Might be my browser. Do you access them off Firefox? Site crashes on me every time since they must've updated something over the summer
I access them with Cromite over VPN and on the computer with Ablaze Floorp (based on ff) but without VPN.
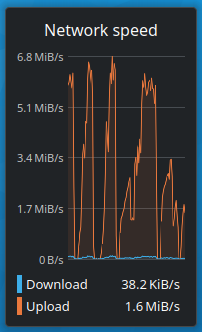
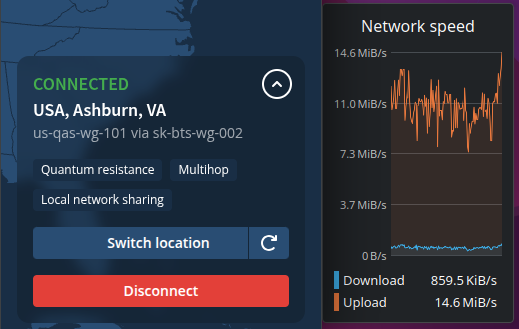
And then there's the mysteries like OneDrive, where I cannot upload without VPN. Either it keeps failing or it's slow.
With a graph, here's what it does without and with VPN, and eventually fails without one:
Google drive/photos downloads also fail when I'm on vpn.
I want to switch to self hosting but I'm only just getting to the point where I can think about doing projects like that and I have several priorities ahead of it. So don't come at me for using google lmao.
Amusingly I had to disable my vpn to post this
How odd. I have never heard of .world filtering based on VPN usage, although it's been some time since I used that instance regularly.
I can read without issue but more often than not posting comments or indeed posts fails unless I pause for 5 mins.
E. This went through without disconnecting as an example. Can't figure out if threshold a pattern
In my experience, many Lemmy instances block what looks like bot traffic. I don’t think it’s as simple as VPN = blocked, but that’s probably one of the signals they pay attention to. I’ve noticed most comments will fail to post when I’m using Mullvad.
Yeah its usually certain ip addreses that got abused and are now flagged
I’m totally guessing but I’m guessing it’s more similar to:
- Accessing from a business owned IP: +20% risk of abuse
- Accessing from C country: +10% risk of abuse
- The rate that you’re making requests: +5% risk of abuse
- Etc
Block if risk of abuse exceeded X%
I have no idea what I’m talking about, but I can’t imagine these companies aren’t using some pretty advanced detection of bot traffic
Joke's on you when their website is wrapped in an app that you have to use.
Happened to me recently with the app I use to buy train tickets.
On iOS I go into App Privacy Report and grab all those domains and put them into Tailscale to route through the correct exit nodes.
Usually it’s just one or two domains like api.example.com, CDNs typically don’t care and I block the other third-party shit via DNS (Blocky).
Stuff like this shows you who is just there to sell your data, and not sell you an experience.
This is sort of amusing because you need to disable your VPN to make an account on WAFRN last I checked.
I swear I saw this exact post from the same handle but the profile pic was vegeta.
But then how will you apply for a passport to emigrate* when they start making applications online only and probably require facial scans using your phone?
(*I'm assuming you're already inside those countries that made such laws)
You dont? When my country goes fascist I'm not gonna run, it's my home and I'll fucking defend it.
Its a brave thing to fight, I admire it, but please don't shame others for leaving. People have the right to choose.
Sometimes you can save it. Sometimes it's beyond saving.
My family left China about 15 years ago, to be clear I didn't choose it, I was just a kid, but I mean like... what the fuck was the point in "fighting", nobody was fighting there, zero resistance.
So, it really depends, how much of a hope there really is, sometimes shit is so fucked there is nothing left to fight for.
I can't blame people for leaving, even if I may or may not agree with their decisions.
Sadly, it's food delivery I've had to add exceptions for :(
Justeat and its local variations (liferando, pyszne) work just fine over VPN and can even be paid with gift cards
You’re ordering food delivery through a VPN? Why?
I do ALL my Internet activity via a VPN. Why? No particular reason, other than I like privacy
I’ve done it several times (though I prefer pickup).
DoorDash isn’t known for being an ethical company so I don’t share my location with them, and I purposely use Apple Pay because like NFC it generates a one-time card number with only enough funds for the transactions.
Thankfully DoorDash has never denied me service even while ordering from what looks like across the planet to it.
If you don’t tell them your location, how does the food reach you?
I’ve done it several times (though I prefer pickup).
Besides, you can give it whatever address you want. You don’t have to give it access to location services at all.
If you give it some random address then they’ll get the food, not you?
Also why even use the app if you’re going to pick up at the restaurant yourself? Just call the restaurant and give them your order. You’ll pay less for the food because there’s no fees going to the app!
Unfortunately, geolocation is a valid thing for that business to want. But can't you install a location spoofer?
Er... maybe? First I've heard of one. I just assumed it's the IP addresses that are blocked - I can't even load the site even with a home-country VPN connected
Ah, that's also possible. Have you considered switching your VPN server to a more local one? And yes, location spoofers do exist; they're widely, if coyly, used in some communities for Niantic games (Pokemon Go, etc).
I really want to take this same approach but so many websites and apps that I use for shopping for things like groceries now just cease working unless I either manually force cycle through them, or just temporarily disable them. I really hate it.
there's always the old walk into the store
but yeah the convenience of pickup is nice
On iOS I go into App Privacy Report and grab all those domains and put them into Tailscale to route through the correct exit nodes.
Usually it’s just one or two domains like api.example.com, CDNs typically don’t care and I block the other third-party shit via DNS (Blocky).
Is there a guide you could point me to on how to do all that? I’ve not used Tailscale or “routed any exit nodes” before.
They’re called App Connectors in Tailscale lingo.

all 80 comments