Welcome to 2025@memes@lemmy.world
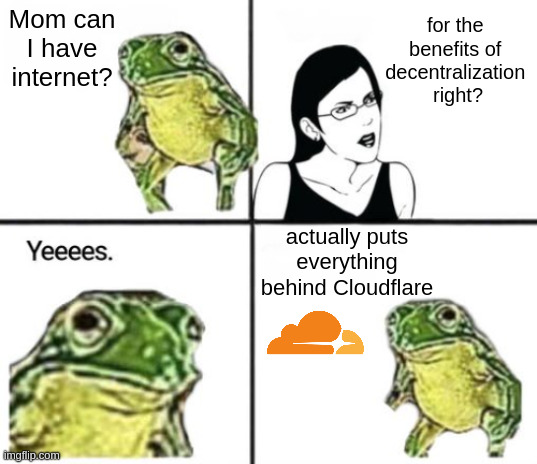
top 61 comments

sorted by: hot top controversial new old
[–] 98 points 1 year ago (1 child)

I deadass got a cloudflare error after reopening this post:

  • source
  • hideshow 1 child comment
  • [–] 126 points 1 year ago (33 children)

    if you can provide me a better way to keep my homelab from getting DDoSed every five minutes then by all means, please share it

  • source
  • hideshow 33 child comments
  • [–] 14 points 1 year ago* (1 child)

    Is you homelab getting ddosed constantly?

    I had had it for years and never ever got ddosed.

    Are you sure it's actually ddos and not just the typical bots scanning for vulnerabilities? Which are easy defended for by keeping updated.

    It's weird as a DDOS is not something that's just happens, it's a targeted attack. It's a rare occurrence that someone decided to attack a homelab.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 7 points 1 year ago

    I spent multiple days getting SYN flooded to the point my router would crash and reboot over and over, and it stopped the moment I set up cloudflare and asked my ISP to change my IP. This was the instance which pushed me over the edge, but there had been smaller attacks lasting a few minutes each for years leading up to this.

  • source
  • parent
  • [–] [S] 27 points 1 year ago (9 children)

    @DaPorkchop_@lemmy.ml @memes@lemmy.world Is that an actual issue or a hypothetical one? I've never had an attack in 10 years of publicly hosting stuff.

  • source
  • parent
  • hideshow 9 child comments
  • [–] 17 points 1 year ago (1 child)

    As someone else who used to host via an open port, you get random connections all the time. Almost constantly and the request paths make it obvious they are scanning for vulnerabilities. Via cloud flare the number of those requests is much lower, as they have to know at least the DNS to do so, (and can't guess it from a presented SSL cert.)

  • source
  • parent
  • hideshow 1 child comment
  • [–] 10 points 1 year ago

    Yeah, I see random https and other connections all the time blindly scanning for vulnerabilities. Not enough to cause any real problems though. One time I publicly exposed redis or rabbitmq (can't remember which) and didn't set a password, so someone set a password for me :). That's about the worst that's happened to me.

  • source
  • parent
  • [–] 5 points 1 year ago (6 children)

    It's the reason I set up cloudflare in the first place, so yeah. I was getting SYN flood-ed to the point that my router would just crash almost immediately, and after rebooting it the attack would resume after a minute or two.

  • source
  • parent
  • hideshow 6 child comments
  • [–] 6 points 1 year ago (1 child)

    Get a router that has flood protection? This is like.. Extremely basic network protection.

    OpenWRT has had configurable syn-flood protection (enabled by default) since like 2010.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 3 points 1 year ago

    Even if the SYN packets were being ignored, the connection would still be unusable if there's enough incoming traffic for most legitimate packets to get dropped. And as mentioned in other comments, the router in question is a shitty ISP router which can't be replaced (although I do have a much fancier router with OpenWRT running behind that).

  • source
  • parent
  • [–] [S] 7 points 1 year ago (3 children)

    @DaPorkchop_@lemmy.ml @memes@lemmy.world Hm weird, I don't see why they would spend their resources attacking random people without any kind of demand. Even at work I've never seen one happening.I still believe Cloudflare has most of its customers because of fearmongering tbh.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 6 points 1 year ago (2 children)

    It's a bit like saying "having a password on your account is fearmongering, why would anyone try to access your data".

    It's only fearmongering until you get attacked, and it's already too late when you do. Better to be proactive.

  • source
  • parent
  • hideshow 2 child comments
  • [–] [S] 7 points 1 year ago (1 child)

    @Alaknar@sopuli.xyz @memes@lemmy.world Being proactive doesn't mean you have to hide your personal service behind a billion dollar company. That is precisely the kind of overreaction triggered by fearmongering. If you don't know how to secure access points or harden configurations, no service will be able to do it for you as if by magic. Not to mention your responsibility towards your users, who may not want to be tracked by a third-party company without their knowledge every time they visit your site (or half of the internet by now).

  • source
  • parent
  • hideshow 1 child comment
  • [–] 1 point 1 year ago

    If you don’t know how to secure access points or harden configurations, no service will be able to do it for you as if by magic

    That's the point. Cloudflare does this as if by magic.

    Not to mention your responsibility towards your users, who may not want to be tracked by a third-party company

    Cloudflare doesn't track your users.

    As a sidenote - am I reading you correctly? Your main issue with Cloudflare is "they're large"? Like, if they were "two dudes in a basement" and provided the same quality product as they do now, you'd be happy to use their service?

  • source
  • parent
  • [–] 11 points 1 year ago (4 children)

    Host your own cloud worthy anti DDOS solution with fail2ban /s

  • source
  • parent
  • hideshow 4 child comments
  • [+] 3 points 1 year ago (3 children)
  • [–] 1 point 1 year ago

    fail2ban is good for preventing spam and DDOS on authenticated endpoints, but it's harder to prevent attacks on public endpoints against a botnet or even a lazy proxy chain spam, which is why cloudflare adds some cookies and a buffer to handle a wave of new connections and maintain an address rank to drop any bad clients.

    Although that being said, cloudflare can be bypassed via other timing tricks and even just using a specific request chain to get fresh cf cookies to avoid getting blocked.

  • source
  • parent
  • [–] 56 points 1 year ago* (6 children)

    Just put it behind a wireguard server and don't expose any ports?

    If you absolutely must expose some stuff, get a cheap 3$/mo vps that connects via wireguard to your home and setup a reverse proxy? They almost all come with DDoS protection.

  • source
  • parent
  • hideshow 6 child comments
  • [–] 42 points 1 year ago* (3 children)

    How do I stop a DDOS attack of my website without having port 80 or 443 open, so you can access the website?

  • source
  • parent
  • hideshow 3 child comments
  • [–] -3 points 1 year ago* (2 children)

    Don't expose the website. That's the point. Only connect remotely via wireguard.

    If you must expose the website, I also provided options in my original post.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 6 points 1 year ago

    Could you shell out for a decent firewall? It should be able to protect against majority of ddos attacks unless someone is paying for something big.

    But it really is fine to use cloudflare if you want the ddos protection. I wouldnt feel bad at all.

  • source
  • parent
  • [–] 14 points 1 year ago (3 children)
  • [–] 21 points 1 year ago (9 children)

    Though I'm not a big fan of centralization, I use cloudflare. Their DDoS protection is unmatched, they have scraping protection, and just in case they decide to screw their users over, switching to another service is trivial.

  • source
  • hideshow 9 child comments
  • [–] 2 points 1 year ago (5 children)

    I don’t know what cloud flare is and at this point im afraid to ask

  • source
  • parent
  • hideshow 5 child comments
  • [–] 4 points 1 year ago (3 children)

    Basically they work as a bouncer in front of your website and stop all the undesirables getting in. I.e. AI scrapers. Also if somebody decides they want to try and hack you or otherwise cause problems the bouncer beats them up and you never have to hear about it.

    If you use a VPN the bouncer is very suspicious of you and you have to jump through all sorts of hoops to get in, which is why some people don't like websites using it. Unfortunately there isn't really a solution since there are a lot of illegitimate uses for having a VPN connection as well, so you have to be suspicious of them.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 1 point 1 year ago (2 children)

    Ah, thanks, I was wondering this too. What shady stuff are they up to?

  • source
  • parent
  • hideshow 2 child comments
  • [–] 1 point 1 year ago (1 child)

    Well mostly it's AI scrapers at the moment (I wouldn't mind as much if they just chilled out, but it's like hundreds of connection attempts per second).

    The other thing is DDoS which I don't really have to deal with, but it's nice to have just in case.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 2 points 1 year ago

    You use it as reverse proxy, to not expose your hosting servers (e.g. websites, Lemmy instances or what not) directly to the Internet. The idea is that they take care of a lot of security concerns for you, which can otherwise be very demanding if you are self hosting

  • source
  • parent
  • [–] -2 points 1 year ago (2 children)

    I can stop drinking whenever I want.

    If switching is trivial, why not do it now?

  • source
  • parent
  • hideshow 2 child comments
  • [–] 26 points 1 year ago (1 child)

    cloudflare ddos protection is cetralization?

  • source
  • hideshow 1 child comment
  • [–] 27 points 1 year ago (2 children)

    Don't forget your SSL certificate to prevent man-in-the-middle attacks. 🤪

  • source
  • hideshow 2 child comments
  • [–] 6 points 1 year ago (6 children)

    I mean I don't really have a choice because i don't see a better way to put my home server on a url because I live in a dorm and can't port forward or get a static ip

  • source
  • hideshow 6 child comments
  • [–] 2 points 1 year ago (5 children)

    If you don't have a static IP, how did you get a domain?

  • source
  • parent
  • hideshow 5 child comments
  • [–] 2 points 1 year ago (3 children)

    That's what they're saying. They're dependent on cloudflare who offer a DNS service that routes traffic to one of their static ips, down a tunnel initiated by the server without an IP address.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 1 point 1 year ago (2 children)

    I'd like to know how to create a tunnel; do you have the docs? I need to host my home server and noip isn't working for me.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 3 points 1 year ago

    I unfortunately use cloudflare. They apparently charge the same price they pay for domain names.

    What better options do we have? I really want to know.

  • source
  • [–] 2 points 1 year ago

    Yeah well if it weren't for all of the LLM bots and scrapers in general and of course all the Russian and Chinese hackers (they may mostly be script kitties, but they're still annoying), we wouldn't need cloud flare. But they do exist so we don't really have a choice.

  • source
  • [–] 1 point 1 year ago

    I use Cloudflare Turnstile because hosting without it is just begging for bots to join my service.

  • source
  • [–] 1 point 1 year ago

    Alright who actually ARE cloudflare? I'm seeing them on every website but idk who they are

  • source