all 37 comments

sorted by: hot top controversial new old
[–] 59 points 2 weeks ago* (last edited 2 weeks ago) (14 children)
  • [–] 12 points 2 weeks ago* (last edited 2 weeks ago) (10 children)

    Ublock blocks this for some reason

    EDIT turns out the reason is it appears to be infected with a botnet

  • source
  • parent
  • hideshow 10 child comments
  • [–] 2 points 2 weeks ago (7 children)

    That's weird. I did some digging and can't find its name, ip, or hosting company servrex.com on any block list. I checked HaGezi on github based on your post.

  • source
  • parent
  • hideshow 7 child comments
  • [–] 2 points 2 weeks ago (6 children)

    I used this https://github.com/hagezi/dns-blocklists#listlookup and searched https://motherfuckingwebsite.com

    If you search the closed github issues, you'll see more details for the url

  • source
  • parent
  • hideshow 6 child comments
  • [–] 1 point 2 weeks ago (5 children)

    Which list? I searched the Multi Ultimate Full list and it wasn't there.

  • source
  • parent
  • hideshow 5 child comments
  • [–] 3 points 2 weeks ago (4 children)
  • [–] 5 points 2 weeks ago* (last edited 2 weeks ago) (3 children)

    Well that's even weirder. It is in a list labeled malicious/scammer/fishing.

    It absolutely isn't any of those.

    Someone else claimed it pulls resources from a botnet but if you view source, that isn't true.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 18 points 2 weeks ago (4 children)

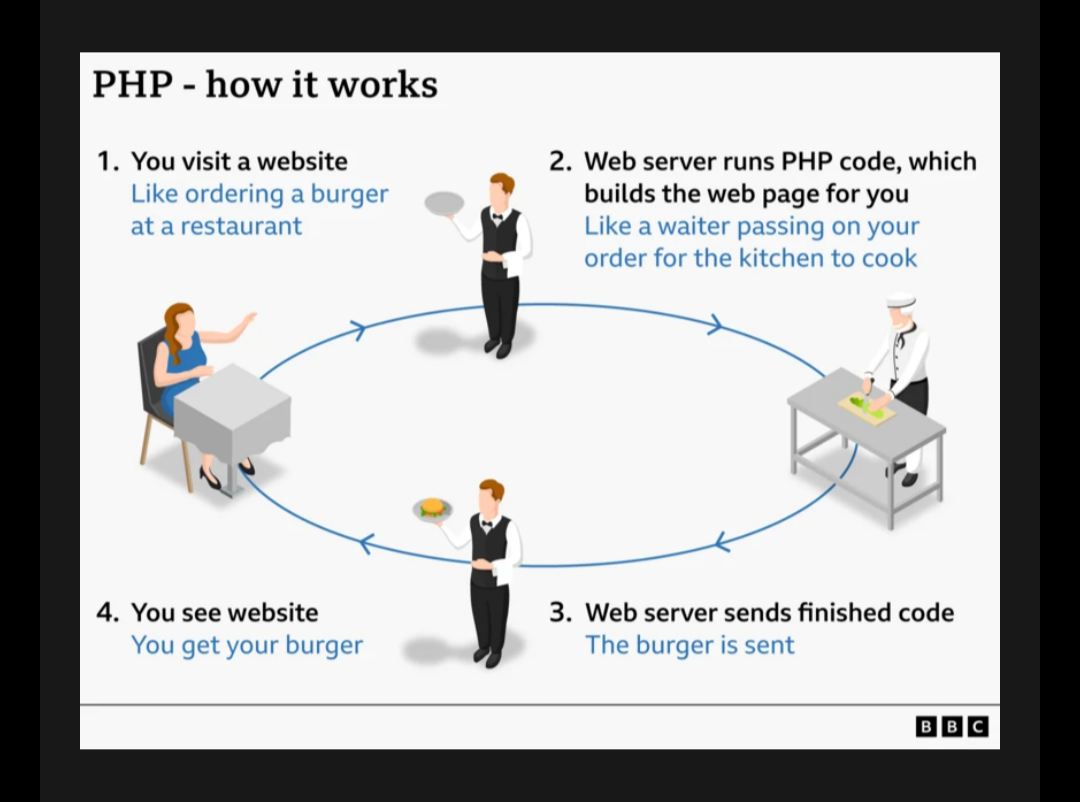
    Wow! That's why I love analogies -- in most cases they don't make any sense especially if you are not a specialist in the theme.

  • source
  • hideshow 4 child comments
  • [–] 2 points 2 weeks ago (3 children)

    Well, they do have some prose in the link that OP also posted, but yeah, it is a bit rough, especially if you're trying to understand the vulnerability..

  • source
  • parent
  • hideshow 3 child comments
  • [–] 6 points 2 weeks ago (2 children)

    holy fuck

    70% of websites are running PHP?

    are they sure?

    Am I going to find a php binary in a node_modules directory

  • source
  • parent
  • hideshow 2 child comments
  • [–] 16 points 2 weeks ago

    Step 5. you inject poison in your burger and send it back. Causing the cook to die and you take over as the owner of the restaurant

  • source
  • [–] 13 points 2 weeks ago (1 child)

    Wait till you learn about this new CGI thing, you'll be amazed about what it can do: https://en.wikipedia.org/wiki/Common_Gateway_Interface

  • source
  • hideshow 1 child comment
  • [–] 9 points 2 weeks ago (6 children)

    Why is everybody talking about PHP lately? Am I out of the loop?

  • source
  • hideshow 6 child comments
  • [–] 14 points 2 weeks ago (5 children)

    They fixed a bunch of vulnerabilities there which were known for years but neither hackers nor PHP developers cared much until recently.

  • source
  • parent
  • hideshow 5 child comments
  • [–] 3 points 2 weeks ago (4 children)

    Wait it was known!? They didn't just discover it and fixed it quickly?

  • source
  • parent
  • hideshow 4 child comments
  • [–] 16 points 2 weeks ago (1 child)

    It's not a quick or easy fix. The patch is a 10000 line nightmare. No really it's actually 10k. A lot of that is test code, but there are also significant changes to deep engine internals.

    PHP did really really bad memory limit handling. Now it's only really bad.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 10 points 2 weeks ago (1 child)

    No, they chewed snots for years because there wasn't a trivial and straightforward fix and exploit looked too "theoretically possible". But some time ago(months? year?) some company showed them a working exploit, so they started to think how to actually fix the problem. All that time they kept all in secret so hackers wouldn't know. But the fix had leaked, letting hackers to figure out what was the vulnerability in the first place, so snot-chewing was replaced with running-and-screaming. By now everything is fixed for those who cared to update\recompile. Something like that.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 6 points 2 weeks ago

    Most of my experience with PHP is from pen testing so most of my orders look something like <?$_GET[0]?>

  • source
  • [–] 5 points 2 weeks ago* (last edited 2 weeks ago)

    The cook should be represented as the database.

    Back in the 80's, my brother "hacked" a pizza place because he knew how they wrote green olives and black olives on their ticket. He dated a girl who worked there for a stint.

    I don't remember how it worked and he has since passed, but it was something with the order that he would list the toppings that would fuck up the cook, so the order always came out wrong and boom! Free pizza.

  • source
  • [–] 4 points 2 weeks ago

    Dam, I guess I was a programmer at KFC, and I didn't even know it...

  • source
  • [–] 2 points 2 weeks ago

    the person getting the burger actually has a user agent which fetches the burger for them. Its a food delivery app and the browser is doordash/uber eats etc. Instead of packets its human beings who read a screen and understand obligations.

  • source
  • [–] 2 points 1 week ago* (last edited 1 week ago)

    Explaining PHP to an anglo: so imagine ordering a burger...

  • source
  • [–] 1 point 2 weeks ago

    What if I visit a website to order a burger

  • source
  • [–] 0 points 2 weeks ago