Mr Lovenstein | Mastodon | Patreon
Secret Panel 💦
Transcript
4 Panel Comic
Panel 1: A doctor lifts up a healthy baby in front of a tired mom
Doctor: Welcome to the world, little guy!
Panel 2: The doctor holds the child up in front of a tablet
Doctor: You need to create a life account
Panel 3: The baby is frustrated as the tablet rejects the input
Tablet: Sorry, that username is taken
Panel 4: The baby facepalms as the tablet needs even more info to create the account
Tablet: You need to make an email account for Two-Factor Authentication
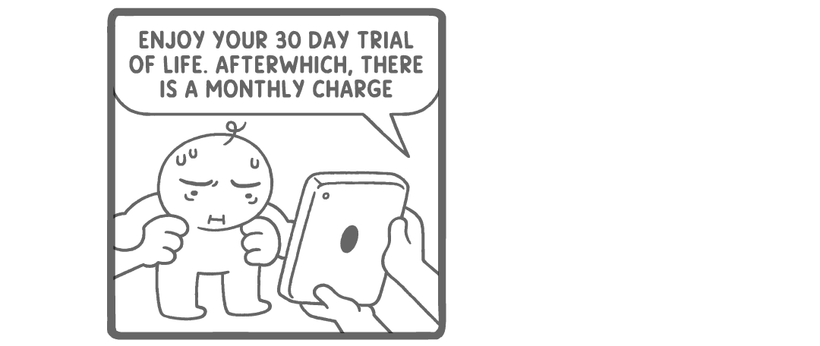
Secret Panel: The baby sweats as the tablet continues
Tablet: Enjoy your 30 day trial of life. After-which, there is a monthly charge.
