after almost 15yrs my plex server is no more. jellyfin behind nginx with authentik is running very nicely.
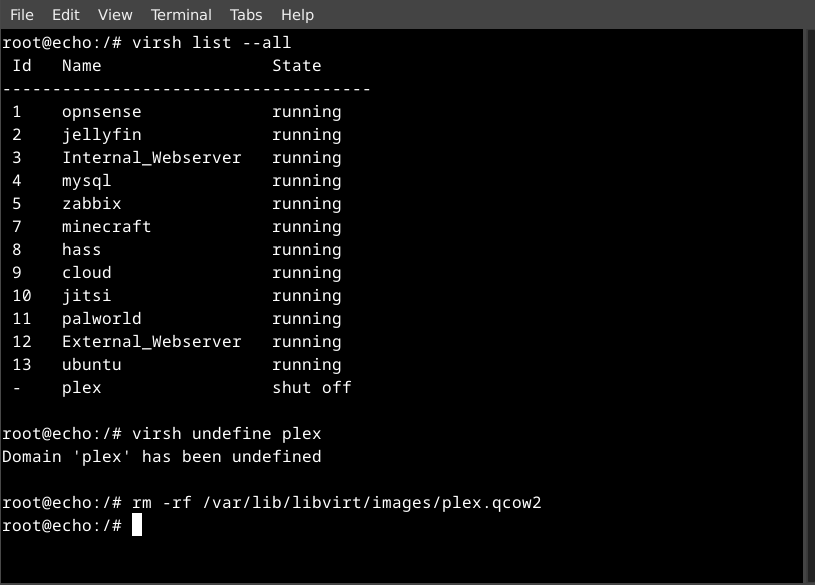
after almost 15yrs my plex server is no more. jellyfin behind nginx with authentik is running very nicely.
I’ve heard jellyfin has a lot of security issues
The biggest known stuff I saw on their GitHub is that a number of the exposed service URLs under the hood don't require auth. So, it's open-source with known requirements, you can tell easily from the outside that it's running, and you can cause it to activate a LOT of packages without logging in. That's a zero-day in any package that can be passed a payload away from disaster.
AS far as TVOS, I'm kinda surprised swiftfin doesn't service you.