Top tip: don’t use Google’s products.
post
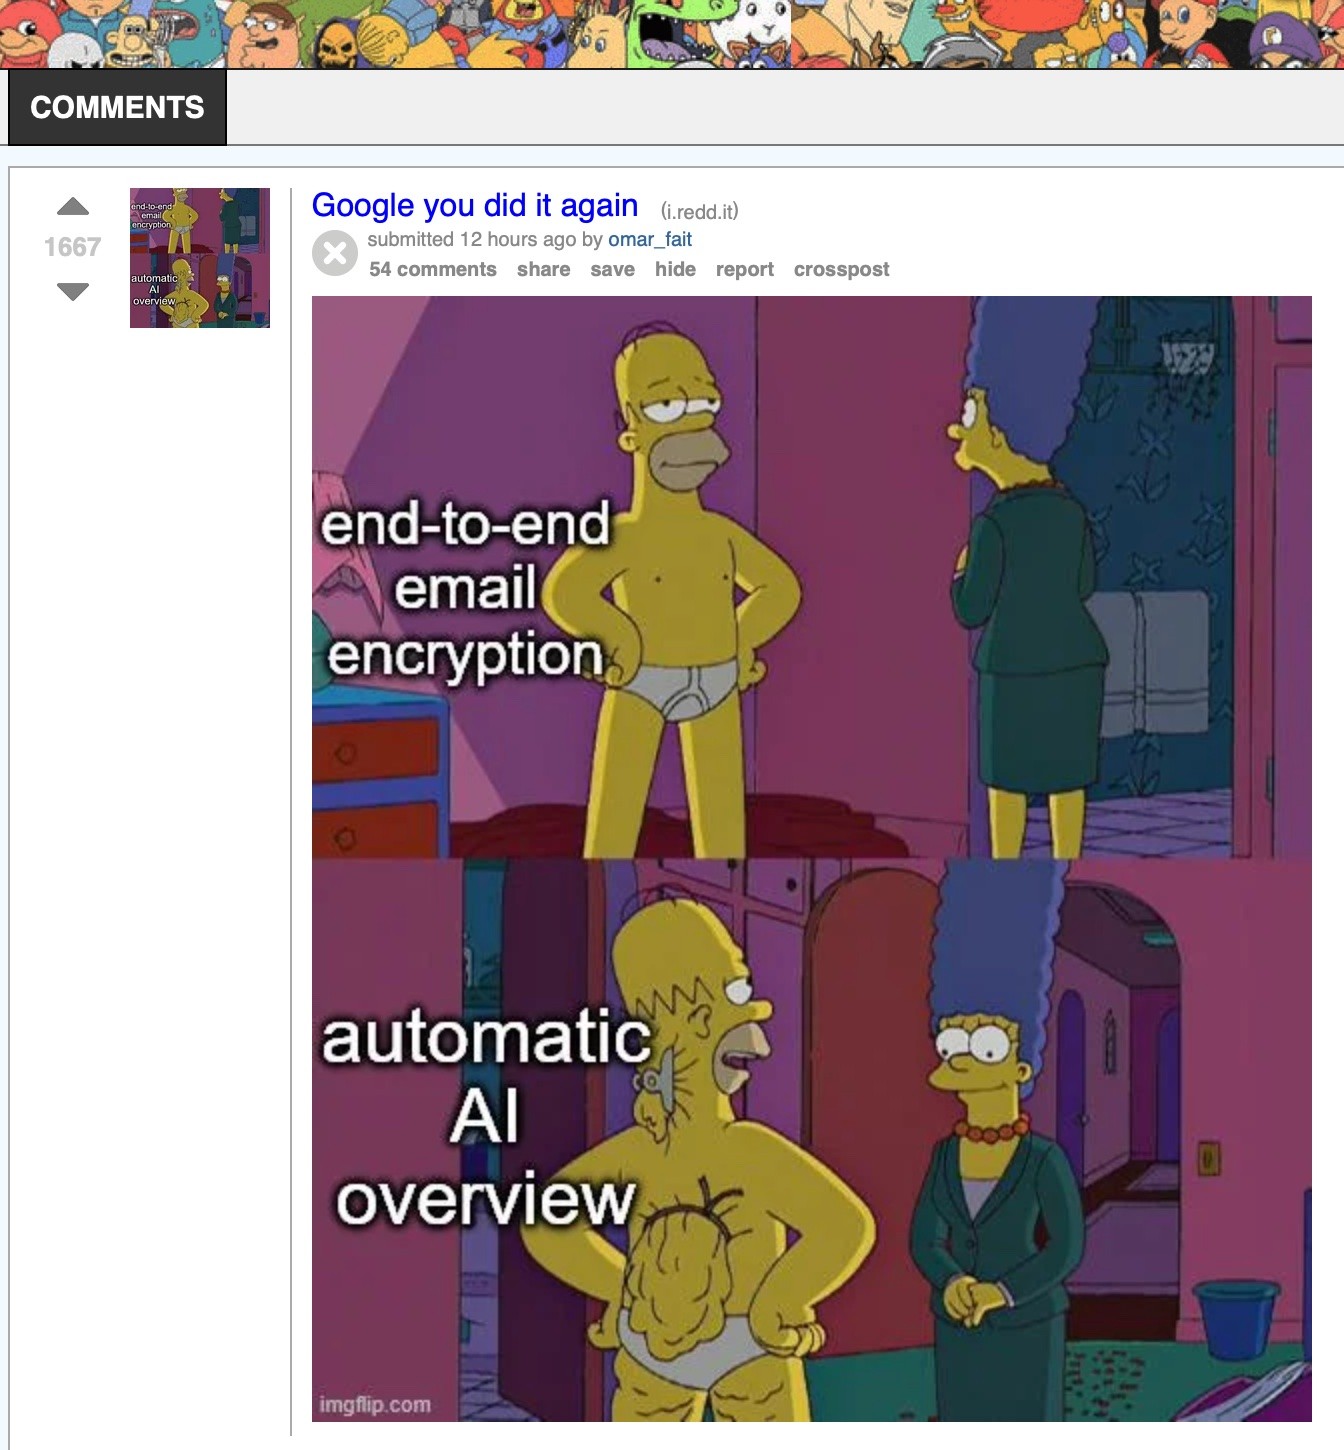
Hey they never said exactly where those “ends” are.
That's why Apple really needs to prove they are sticking with AI locally indexing information and not sent out. Whether it's an RCS or iMessage and you say it's E2E, but your calendar app on another device is now recommending an event based on that text... People should be verifying that at no point did that data leave their encrypted cloud data. If it did... Neither is E2E
Some companies think end to end encryption is when you check the content on both ends.
End to end encrypted except for the runtime of users which is where you do the data harvesting
I mean, just learn how to GPG and you can send the message encrypted between y’all.
I just opened a Proton email account, and it claims to be encrypted; however, I still suspect they hold the keys for warrants and shit so I won’t trust it that far.
In court, many times, it has been shown that proton cannot decrypt the emails
I mean, they don't have to. It's kind of pointless to have encrypted storage when everything that enters and exits is plaintext.
In theory it should be possible to keep things encrypted strictly among Proton mailboxes but that's more like a private message board than email.
I don't like how proton requires you either use their proprietary mail app or bridge. Mailbox.org just pgp encrypts messages, which you can read through regular imap with any mail client that supports pgp decryption
Always amazed by the creativity of the people around here.
Wait, we can have accounts on more than one platform?! Why has no one told me this
all 31 comments