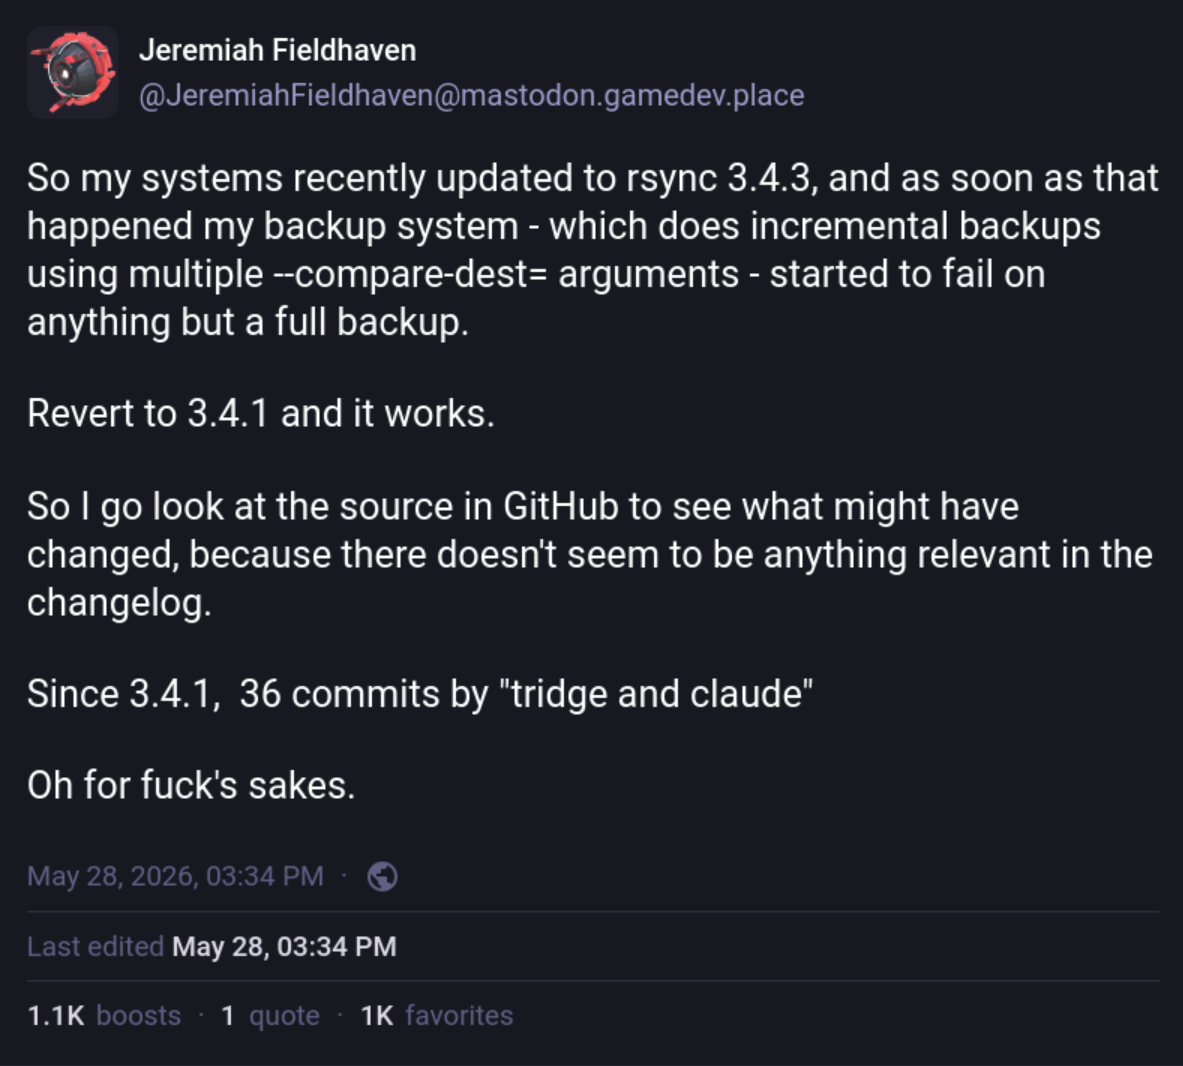
I suppose the problem is that this was evidently brought on by trying to use AI to be proactive about security risks from AI findings. So an abandoned rsync would gather cves.
It would gather CVEs, yes, but at least the codebase would not change so fast that even the maintainer themselves can no longer keep up with understanding all the changes. I've looked at a few commits and there's way too many lines of code for the maintainer to have carefully reviewed and understood them all.
But an abandoned rsync would have two great advantages:
- it would give stronger support / user interest to a fork
- distros would not face the decision whether or not to upgrade to a version with slop in it
If it’s a security issue, then… ok fine, you have to give it a try, but it looks like stirring things up to try to fix years of maybe not right, which is a risky proposition.
Also - if a tool finds a security risk, then I want a human maintainer to wrap their head around the attack vector to come up with the correct patch to counter the actual attack vector. Slop machines have zero understanding, so if you need to put out a house fire with people in it, a slop machine might as well drain all oxygen from the air. The fire will be gone after that. But so will the people.