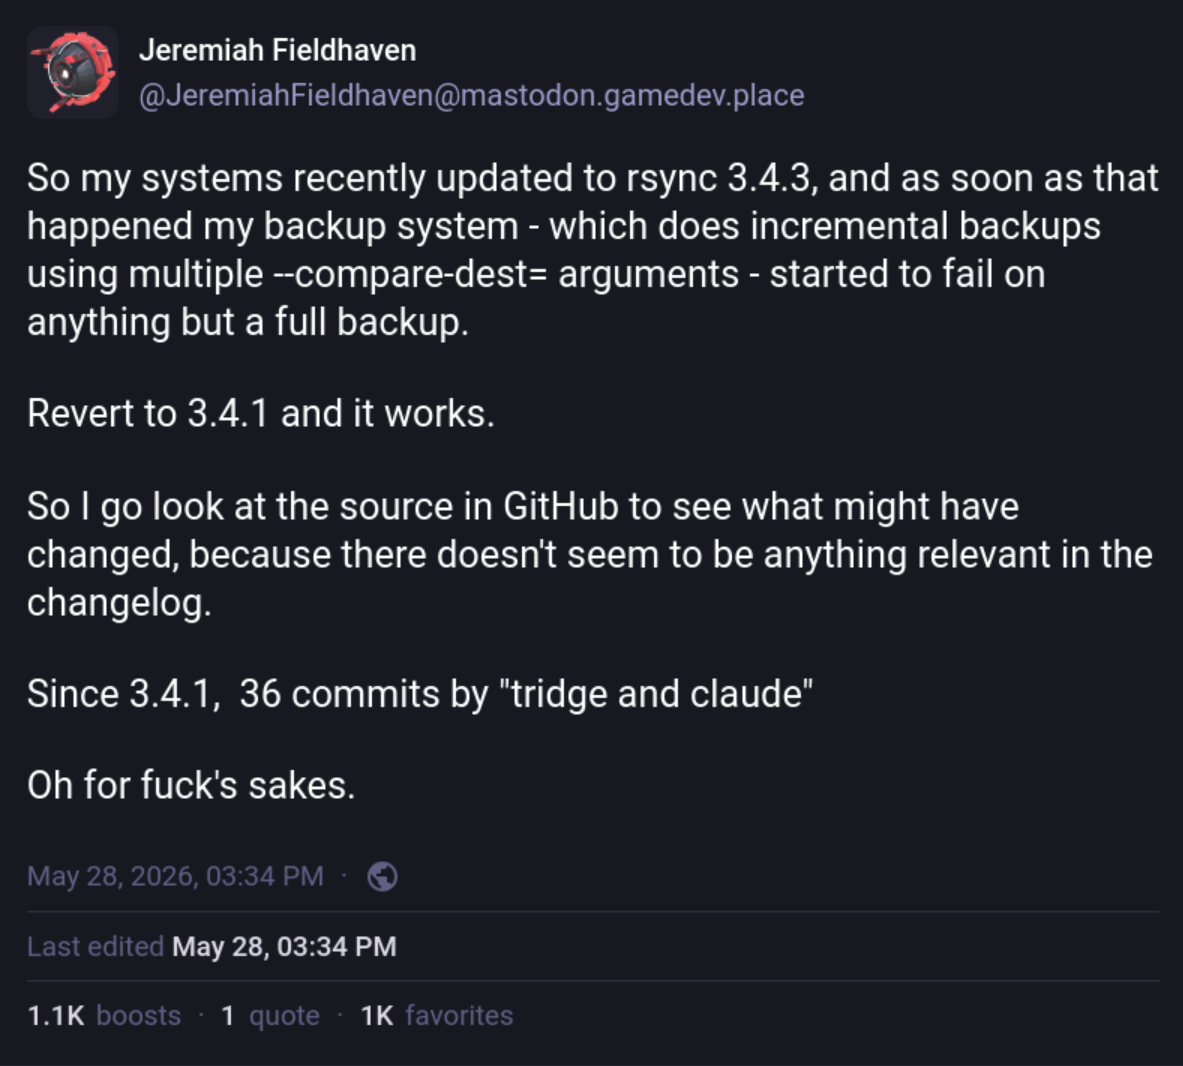
"We did it, Patrick! We made a technological breakthrough!"
A place for all those who loathe AI to discuss things, post articles, and ridicule the AI hype.
Proud supporter of working people. And proud booer of SXSW 2024.
AI, in this case, refers to LLMs, GPT technology, and anything listed as "AI" meant to increase market valuations.
Rules:
- Relevant posts only.
- No bigotry.
- No misinformation.
- No NSFW/NSFL content without being labeled NSFW or being in an appropriately-labeled spoiler tag.
- This isn't a place to talk about the cons and (supposed) pros of AI for different use cases. This is /c/fuck_ai .
- Especially no AI advocacy.
- No AI-generated content. If you want to post examples of AI failing hillariously, there are other communities for that like !ArtificialIgnorance@lemmy.ca .
- Venting is part of the purpose of this community, but don't aim frustration or accusations at other users.
- These rules are a living document that may change in the future.
You can help the mod team by making your reports detailed.
Effective reports:
- "The third image is a well-known anti-semitic trope"
- "Claiming that 'agentic AI' can outperform humans at all jobs is misinformation"
Less effective reports:
- "Breaks rules"
- "Misinformation"