1
posts
2
PSA: you can't delete photos uploaded to Lemmy. So don't (accidentally) upload a nude. That would be bad 😱
(tech.michaelaltfield.net)
This article will describe how lemmy instance admins can purge images from pict-rs.
 |
|---|
| Nightmare on Lemmy Street (A Fediverse GDPR Horror Story) |
This is (also) a horror story about accidentally uploading very sensitive data to Lemmy, and the (surprisingly) difficult task of deleting it.
3
4
How's "made in Germany" on a website any better data-protection wise than "made in South Africa, Indonesia, Bolivia"?
(lemmy.world)
Whenever I encounter the label "made in EU", "Germany", "Estonia", "France" ...... in the footer of a web project, which implies enhanced data-protection, apparently, I wonder:
How can it be so? There're some data-protection laws, yes. But one can't control a hosting provider 24h/day. One can't know whether an employer there copies all data on his memory-drivers.
Can't the police, if need be, seize a server as easily as it would in any other country on Earth?
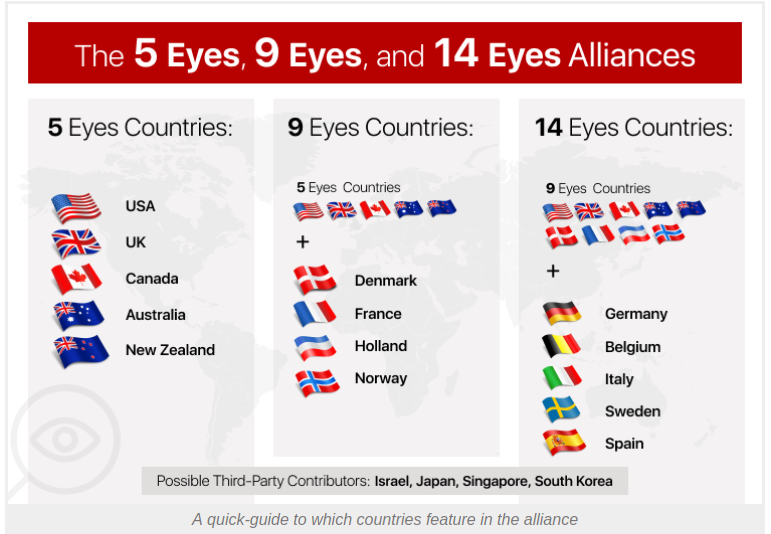
Don't the majority of all of countries in Europe share information with the intelligence of US by the agreements of the 5 eyes, 9 eyes, 14 eyes? Whereas the 2nd and 3rd world countries don't.
How is it better than a label "made in South Africa", "Thailand", "Costa Rica", "Egypt", "Kuwait"?
I can see how "made in Germany" or EU makes a project worse in terms of privacy and data-protection. How could it make it better, though?
5
6
We're happy to announce that we were successfully able to initiate a BusKill lockscreen trigger using a 3D-printed BusKill prototype!
 |
|---|
| Watch the 3D Printable BusKill Proof-of-Concept Demo for more info youtube.com/v/Q-QjHelRvvk |
What is BusKill?
BusKill is a laptop kill-cord. It's a USB cable with a magnetic breakaway that you attach to your body and connect to your computer.
 |
|---|
| Watch the BusKill Explainer Video for more info youtube.com/v/qPwyoD_cQR4 |
If the connection between you to your computer is severed, then your device will lock, shutdown, or shred its encryption keys -- thus keeping your encrypted data safe from thieves that steal your device.
Why?
While we do what we can to allow at-risk folks to purchase BusKill cables anonymously, there is always the risk of interdiction.
We don't consider hologram stickers or tamper-evident tape/crisps/glitter to be sufficient solutions to supply-chain security. Rather, the solution to these attacks is to build open-source, disassembleable, and easily inspectable hardware whose integrity can be validated without damaging the device and without sophisticated technology.
Actually, the best way to confirm the integrity of your hardware is to build it yourself. Fortunately, printing your own circuit boards, microcontroller, or silicon has a steeper learning curve than a BusKill cable -- which is essentially just a USB extension cable with a magnetic breakaway in the middle.
Mitigating interdiction via 3D printing is one of many reasons that Melanie Allen has been diligently working on prototyping a 3D-printable BusKill cable this year. In our latest update, we hope to showcase her progress and provide you some OpenSCAD and .stl files so you can experiment with building your own and help test and improve our
designs.
Print BusKill
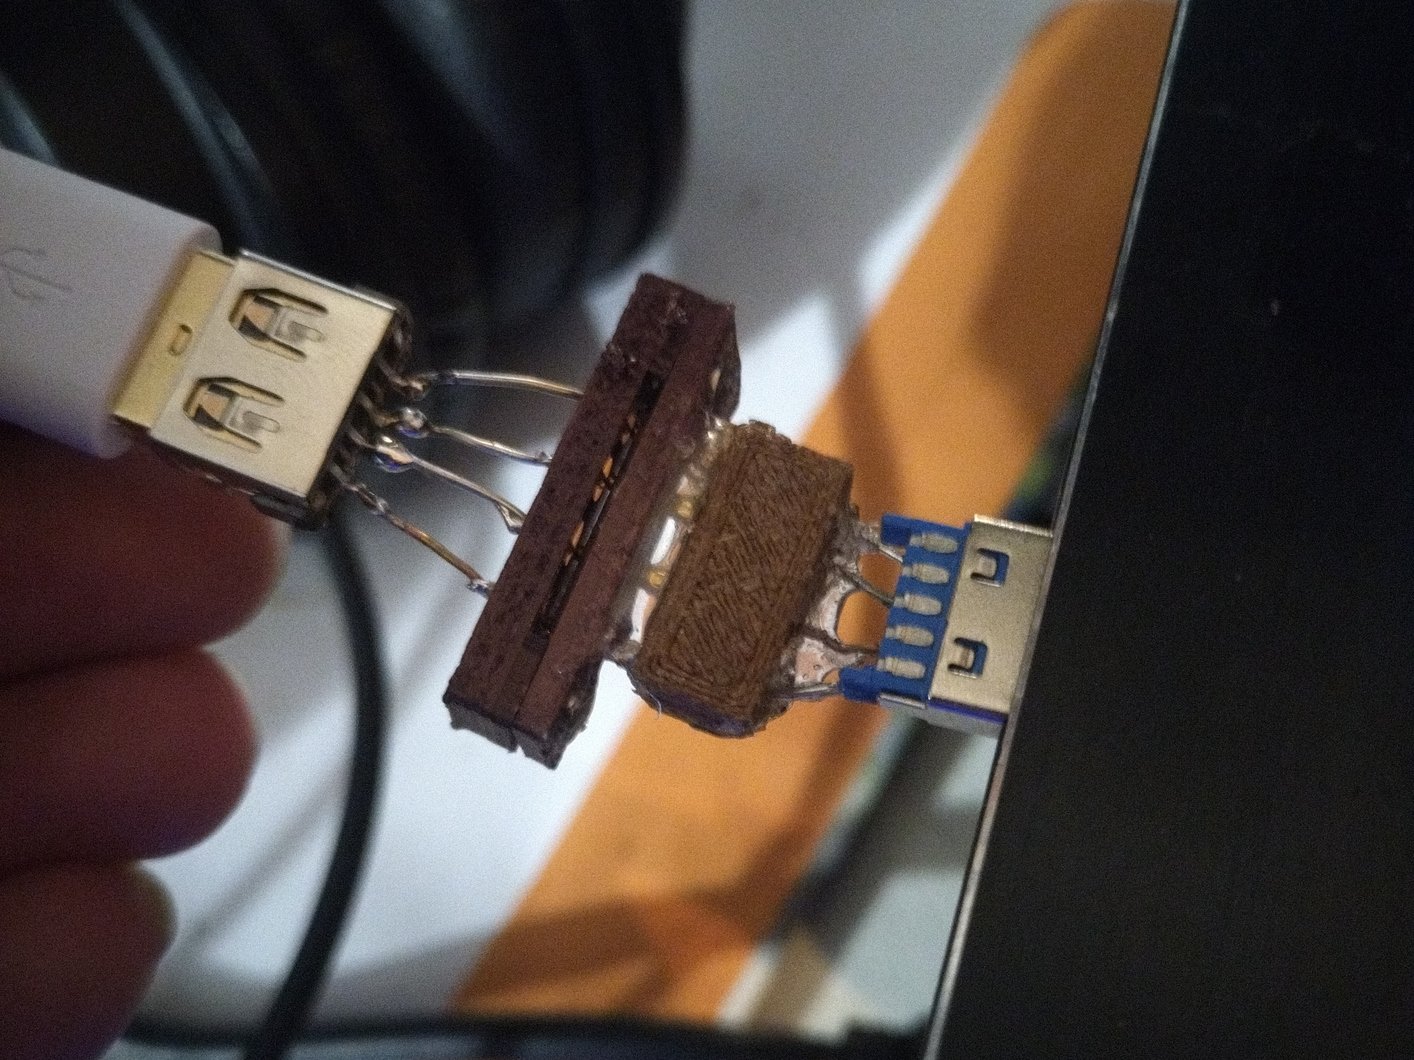
If you'd like to reproduce our experiment and print your own BusKill cable prototype, you can download the stl files and read our instructions here:
Iterate with us!
If you have access to a 3D Printer, you have basic EE experience, or you'd like to help us test our 3D printable BusKill prototype, please let us know. The whole is greater than the sum of its parts, and we're eager to finish-off this 3D printable BusKill prototype to help make this security-critical tool accessible to more people world-wide!
7
8
9
10
11
12