all 16 comments

sorted by: hot top controversial new old
[–] 29 points 3 weeks ago* (2 children)

Good to see they followed best practices by using a random number. At least it wasn't a birthdate.

a function named get random number that always returns 4 with a comment saying "chosen by fair dice roll. Guaranteed to be random"

  • source
  • hideshow 2 child comments
  • [–] 6 points 3 weeks ago

    It's amazing, I have the same combination on my luggage!

  • source
  • [–] 6 points 3 weeks ago (7 children)
  • [–] 32 points 3 weeks ago

    A security certificate authority from India had several of their keys deciphered because the numbers used to generate them were way too short. In fact one of them was simply the number 4. Because of this basically the entire internet has been put at risk because it’s trivially easy to forge keys from this trusted authority.

    https://www.theregister.com/security/2026/10/20/indian-certification-authority-emudhras-private-keys-compromised-one-of-them-was-the-number-4/5304312

  • source
  • parent
  • [–] 2 points 3 weeks ago (5 children)

    Its the same joke everyone else is making.

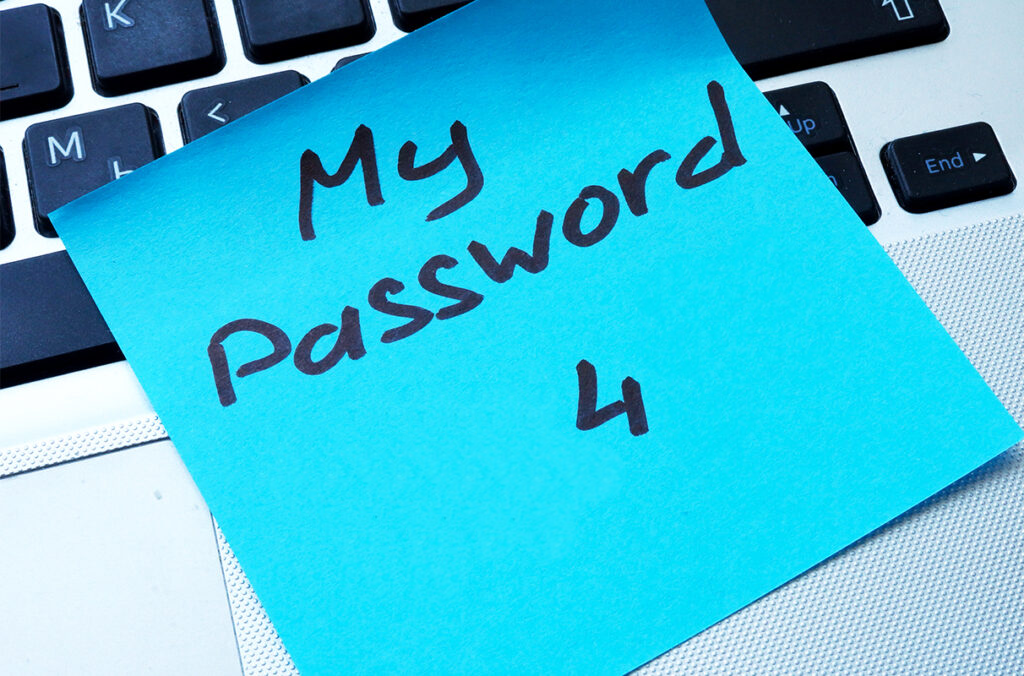
    If you open the original post URL, there is an image with a post-it note reading "My password 4". Some servers don't show the post images sometimes, I had to open the original URL to see the picture.

  • source
  • parent
  • hideshow 5 child comments
  • [–] 3 points 3 weeks ago (4 children)

    Yeah kbin.earth doesn't show it.

  • source
  • parent
  • hideshow 4 child comments
  • [–] [S] 2 points 3 weeks ago (3 children)

    Ah sorry about that the picture is necessary

  • source
  • parent
  • hideshow 3 child comments
  • [–] 5 points 3 weeks ago

    don't forget the leading 115 zeroes.

  • source
  • [–] 4 points 2 weeks ago

    We got 4 before 6

  • source
  • It's a perfect addition to the HTTPV ecosystem! https://www.youtube.com/watch?v=M1si1y5lvkk

  • source