It says "private" and "encrypted", both of which we just have to take your word for.
comments
comment on
Git as a messaging app
comment on
Git as a messaging app
it says it right there in the FAQ. im not alleging its secure at all; "this demo is provided for testing and demo purposes only. use responsibly."
comment on
Git as a messaging app
Allegedly secure, but no independent audit and closed source. Nobody should use this.
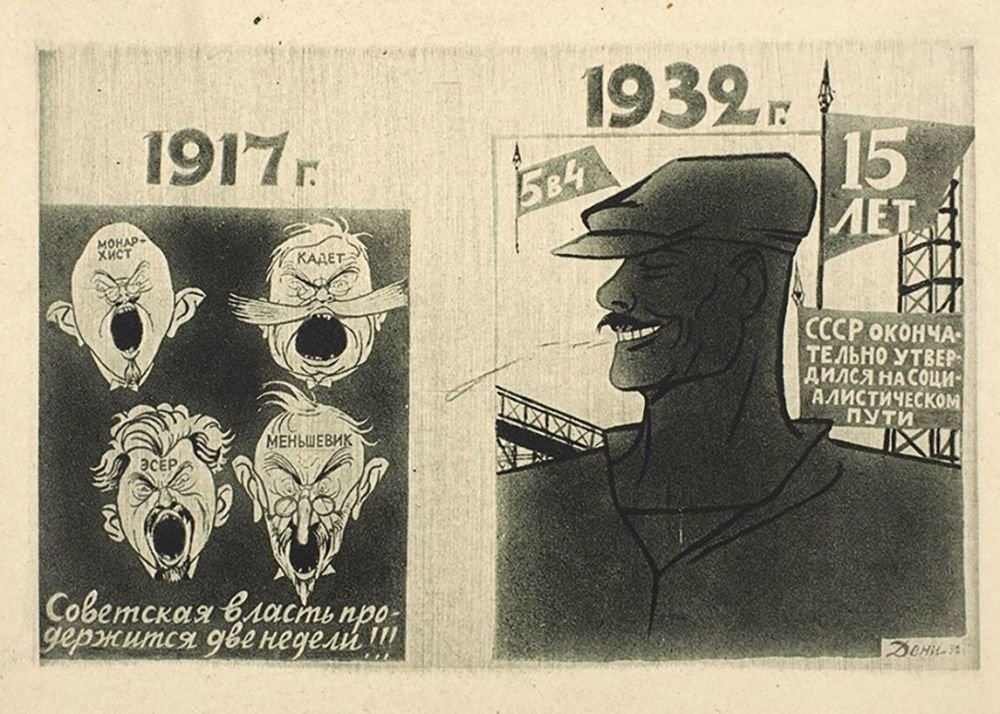
How the ancient practice of superiority bias leads bad analysis? I used the image as an exempli gratia. A “this is bait” if you will.

No I mean how is it relevant to this post?
I am still looking for the cited source of this USSR prop. Usually I take the time to do so, but Russian isn't a language I am familiar with. Bottom right has the watermark of the artist.
I am using it as a rhetorical comparison: “people that compare their work as better than others generally do not try to comprehend the validities of another perspective.”
Later I got curious to see if he makes his own website, to confirm my suspicion that he does indeed use third party libraries.
Where did this image come from? I don't see it in the article.
my curiosity got the better of me
view-source:Behold it is I, sir hypocrite!
That image says everything I need to know to ignore it.
comment on
An improved attack on 7-round AES
That’s a lot to ask! So to be clear: this scenario is completely unrealistic. There’s no practical attack here. AES remains fine.
I'm glad they stuck this nearish to the top.
...Report initially closed as Informative and out of scope...
Report reopened...
...
2026-02-16- Update requested, no response received
2026-03-03- Update requested, no response received
...
2023-03-17- Direct outreach to Cursor CISO requesting update
2026-03-18- HackerOne indicates Cursor has been contacted
2026-04-01- Update requested, no response received...
Thankfully, never used, will never use.
The attack vector highlights a critical gap in supply chain security where a single compromised write credential can pivot to force-update malicious tags. This incident underscores the necessity of implementing strict least-privilege access controls and read-only defaults for CI/CD dependencies to prevent similar credential-based pivots.
"If I can't win, I'll take us all down" Russia.
I just watched a video about this yesterday. At the start of the video I immediately thought "It's Russia".
comment on
Why Hardened Images are Suddenly Everywhere
Disclaimer: Docker, Red Hat, Bitnami by VMware/Broadcom, Google, AWS, and Chainguard are all RedMonk clients.
Real good of them to throw that in at the very end of a lengthy article promoting their products.
comment on
Why Hardened Images are Suddenly Everywhere
If NixOS could strip down its base, it could very well serve a base for other hardened images.
That's one of the reasons) why JS development is the shitshow it is.
Yes but the reality of JavaScript codebases is that you'll typically import hundreds if not thousands of dependencies fairly quickly. Last time I looked at the UI codebase at my job it was sitting at over 40k.
The 👏 death 👏 of 👏 github 👏 will 👏 never 👏 be 👏 the 👏 death 👏 of 👏 open 👏 source
IDK how other people are, but to me solving a problem with a single #include just feels right. Less code to maintain, responsibility is shifted to a dedicated person, obviously much faster.. But also constant anxiety and daily monitoring of security blogs, so I'm trying to cut back
Honestly the best solution is to have minimum amount of dependencies.
Isn't this a sane practice in programming anyway? Just don't go overboard with dependency minimalism.
Running actions on your own machine doesn't solve cache poisoning or supply chain attacks, your VM will download compromised npm package or github actions the same way GH runner does.
Version pinning/script disabling makes a compromise slightly less likely, rolling your own package server helps a lot (but who got time to maintain version whitelist).
Honestly the best solution is to have minimum amount of dependencies. You don't need a GH action to ping indexers or generic foreign key library for your backed, hammer one yourself.
That and scope all your keys so the leak won't be as devastating 🤷♀️
How do you run it on a local machine?
[deleted]
comment on
Mythos finds a curl vulnerability
... just don't read that part and miss the following:
Not using AI code analyzers in your project means that you leave adversaries and attackers time and opportunity to find and exploit the flaws you don’t find.
Daniel's saying that on a codebase already having been analyzed with good LLMs Mythos didn't additionally find much the others had missed.