I'm quite new here but it seems to be a pretty good instance. Thanks!
comments
comment on
Small Update: <10min outage
comment on
Reddthat Update: April 2026 - Lemmy v0.19.18
You don't need to worry too much about that. It was always going to happen. Backing up the database(s) as well as all other files as well as uploading of videos makes it a "cost of doing business".
Personally I'm not in financial strife and am very lucky in that regard, but who wants to pay $150/m and do extra work! No one! So any monetary help is always welcomed, and it reminds me that people actually enjoy Reddthat and want this to keep going!
comment on
Reddthat Update: April 2026 - Lemmy v0.19.18
Thank you for everything you do! I'll try to remember to shrink images more before uploading.
Wooo! 🎉
Sweet. There's another issue open on the FHF repo where someone was questioning :latest vs :main tag so, yeah, there may be some mismatch between what they're running and what they think they are running / was originally documented...
Thanks, patched and its page=2 now. (I wonder how LW never managed to see that... They must not be using that image...!
It's up and running again, but now it seems like pagination is broken. (Going to any page and clicking "Next" at the bottom returns a "there doesn't seem to be anything here" error.)
Probably has to do with page=0 being in the URL for next page links?
Edit: Looks like line 213 of state.go should be changed to q.Set("page", strconv.Itoa(p.Page+1)) -- I tagged you in the comment I made about it on the FHF repo too but not sure how well GitHub handles @ notifications.
SORTED! Ended up patching it myself. Enjoy :D
😥. I will fix it! I think because we are still going via nginx, it's still has to pass the go-away challenges, which it must be failing and thats why...
Annnd, as we just moved I also only have key access to the server and I made all new keys and don't have one on my other devices yet. (A classic)
Edit: nope, it's now attempting to connect over https to the container... I think I'll need to write a proper patch for it to allow for a override.
It also looks dead in the water/feature complete. So I've moved to FSFs container. (https://github.com/Fedihosting-Foundation-Forks/mlmym).
If I end up making a patch I'll upstream. (I'm surprised LW hasn't made one already)
...and it's down again. 🫠️
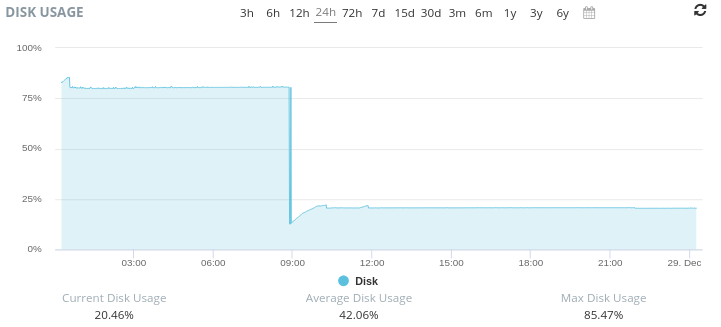
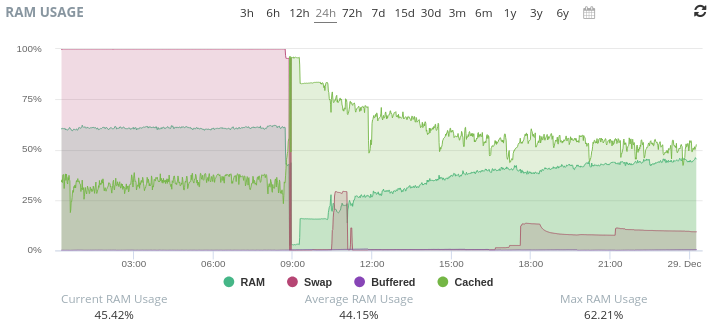
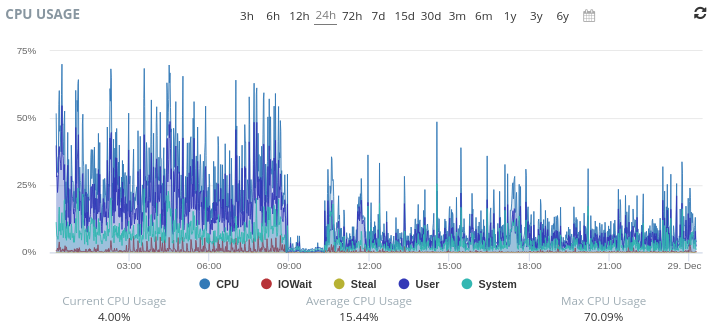
Fun Pics:
- Disk 80%->20%
- Ram from 24GB
- CPU went from 25% (average) to 7% (average)
I had to tell our main_nginx that it is "reddthat.com".
services:
  proxy:
    image: docker.io/library/nginx
    ...etc...
    networks:
      default:
      lemmy_internal:
        aliases:
          - reddthat.com
Now its: {user} -> CF -> {server_nginx} -> {frontend_nginx} -> mlmym => ((docker internal network)) -> {main_nginx} -> {{lemmy-ui/api}}
Instead of: {user} -> CF -> {server_nginx} -> {frontend_nginx} -> mlmym => CF -> {main_nginx} -> {{lemmy-ui/api}}
Thank you. It seems to be working now.
I remember having a devil of a time trying to get mlmym and lemmy to talk to each other on my local system when I was poking around at trying to fix some issues in mlmym a few months back. (I should really get back to that at some point...) They had "https://" hard-coded in front of the domain name parameter -- and I didn't want to have to change the Go source code just to get a dev environment up. I ended up working around it by modifying my hosts file (to add a .INTERNAL domain), ran things under podman with host networking, configured Apache on the host to reverse proxy into both containers, and set up a self-signed cert that I had to rebuild into the mlmym docker (by copying in the appropriate crt files + running update-ca-certificates via the Dockerfile). In retrospect, I probably should've just modified the code...
What was the workaround you had to implement to fix this one?
I believe I've fixed it.
A recent docker update no longer supports overriding hosts with hostnames. (I was telling mlmym that 'reddthat.com' is 'lemmy-ui'. Which would make it request directly to the lemmy-ui container rather than going back out to CF and back again.
(For others/if you want to know the nitty gritty). I was doing this:
    networks:
      lemmy_internal:
    extra_hosts:
      - "reddthat.com:lemmy-ui"
Which did actually work, but now it doesn't since I updated/installed docker compose v5.0.0.
(Seems the correctly enforce the host:IP format now). So I had to do a work around.
You rock too!
We've got oodles of gigabits!
:( yeah the outage notification woke me up.
As it was late I did a work around to temporarily fix it. I'll be looking at it once I've had coffee.
old.reddthat.com is currently not working (at time of posting this comment). Most pages show unable to retrieve site., although I did get dial tcp (an IP address):443: connect: connection refused. (where (an IP address) is an IP that I've redacted) on some pages.
Can we have more dedotated wam?
Thank you! Already a very noticeable difference in load times. Excellent. You rock ticoombs!
Fixed up. All seems to be working. 😪
For those of you who were watching, check out our possible new status page: https://statusv2.reddthat.com/ (it has our CPU/Ram/Disk usages on display for everyone to peruse)
Working on fixing old.reddthat.com.
Migrated Successfully!
Pictrs Test: 
For our application process, as we only require 1 piece of information which is easily scriptable from the API (if someone were to go into that level of automating). But there is at this time 1+ people who regularly signup wait a week+ and then use the account to post something , wait 2 hours and then delete the whole account. (Resulting in all links and history to be deleted).
In the recent Lemmy update that fixed the exploit where even admins would no longer be able to view the account(s).
The actual bots on the other hand are completely dumb and could be automated away, but at the end of the day, I don't want to destroy someone's account creation due to some LLM hallucination.
And some are obvious bot names, (like "holidaydestination") but still fill out the form correctly.
Reports are case by case basis with a fair amount of leeway for reddthat users as just because I am from a specific country doesn't mean I have the right to impose my biases on others.
The majority of the work results in actioning reports and ensuring we don't let bots/people not even trying to read the application process into Reddthat.
Can't you use the same tools they use to get in to filter out applications with high confidence and check the ones with low confidence with a cleverly disguised for an LLM, a 2nd appeal option.