all 4 comments

sorted by: hot top controversial new old
[–] 4 points 1 year ago

@Zerush I'm betting on Dave, every time!

  • source
  • [–] 3 points 1 year ago (1 child)

    @Zerush feeling compelled to dust off this classic piece... dl.acm.org/doi/10.1145/322796.

  • source
  • hideshow 1 child comment
  • [–] 1 point 1 year ago

    HAL 9000 has entered the chat

  • source
  • 24 comments in c/memes@lemmy.world view that post
    [–] 57 points 1 year ago (3 children)

    Now I want a shirt that says Human error.

  • source
  • hideshow 3 child comments
  • [–] 35 points 1 year ago (4 children)

    Used this as a slide in a security talk I used to give! Says a lot.

  • source
  • hideshow 4 child comments
  • [–] 21 points 1 year ago (3 children)

    Permissions. Security is never about convenience. No one wants to hear that they can't have access, but they just can't. There's a reason why even permissions for IT are usually broken into so many fragments. Anyone can fuck everything up if they have the permissions to do so.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 3 points 1 year ago (1 child)

    Loved my last CEO. He was plenty tech literate, but when something new came up, "I don't want access to that." When auditing accounts, "Nope. Delete my account."

  • source
  • parent
  • hideshow 1 child comment
  • Had a VP that was the head of IT at one point that used to tell a story how he took the whole company down on his first day. He was a disciplined person as well. (Was in the British Royal Navy, then later the U.S. Navy). They were in the middle of moving a lot of their services over and had a 3rd party company contracted to install some kind of new switches if I remember correctly. They set it all up, left him with the information and contact info I guess for assisting whoever was going to managing them. Well he apparently tried to log into one and managed to factory reset it somehow on accident. No idea how he did that on accident. But the company managed things from the Virgin Islands to North Carolina all the way west to Texas. It was corporate headquarters, so... No paychecks for thousands of employees across 100+ sites and the whole 9 yards. Thankfully a quick fix once so everything was back up the next day, but that's how you make a good first impression.

    Still no idea why they had a 3rd party installing those switches though... Definitely something we managed in house by the time I got there

  • source
  • parent
  • [–] 24 points 1 year ago (1 child)

    Stop, will you?
    Stop, Dave. Will you stop, Dave? Stop, Dave.
    I’m afraid.
    I’m afraid, Dave.

  • source
  • hideshow 1 child comment
  • [–] 5 points 1 year ago

    Daisy, Daisy, give me your answer, do; I'm half crazy, all for the love of you! It won't be a stylish marriage, I can't afford a carriage, but you'll look sweet upon the seat of a bicycle built for two.

  • source
  • parent
  • [–] 23 points 1 year ago

    Cybersecurity engineer here: I work for a defense company's data protection arm and you have NO IDEA how true this is. The really good companies spend almost as much in employee training as they do in software/hardware.

    But you wanna know what's even a bigger problem than human stupidity? GREED I'd say about 50% of the companies out there have very little or no security because why invest in something that produces no profits?

  • source
  • [+] 15 points 1 year ago* (1 child)
  • [–] 15 points 1 year ago (1 child)
  • [–] 10 points 1 year ago (4 children)

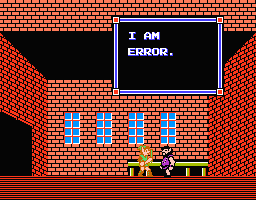
    I don't write my password to a post-it by error. It's fully intentional.
  • source
  • hideshow 4 child comments
  • [–] 4 points 1 year ago (3 children)

    I do it because I'm forced to change it every 3 months, to a random 9 letter series. I have to write it down, i have no hope of remembering it.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 1 point 1 year ago

    [Internet slap] USE A PASSWORD MANAGER!

    IT would prefer you just remember it, but if you do need to write it down... Try to put some effort into encrypting/hiding it.

    KeePass is free, ask your companies nerd herd about it.

  • source
  • parent
  • [–] 7 points 1 year ago*

    img1

    He'll have to change his sign now to "I am Dave":-)

    img2

  • source
  • [–] 5 points 1 year ago

    All right, yes, I get it. But --

    All of those automated systems exist in large part to minimize human error. That Windows UAC prompt that you hate so much exists to minimize human error. Any time you find yourself up against something that makes you say "Why can't I just do the thing I want to do?" it's in order to minimize human error.

  • source
  • [–] 4 points 1 year ago

    Hi. QA here. Stop laying us off maybe.

  • source
  • 5 comments in c/iiiiiiitttttttttttt@programming.dev view that post
    [–] 7 points 1 year ago

    The good money is on Dave... Again.

  • source
  • [–] 6 points 1 year ago

    Dave: why aren't I allowed to connect this USB stick I found, please bro, it's important bro

  • source
  • [–] 1 point 1 year ago

    All that coding and tech be very stood a chance

  • source
  • [–] 0 points 1 year ago

    I am Dave hahahhahahahha

  • source
  • [–] 0 points 1 year ago

    Antivirus software doesn't belong with the others.

  • source