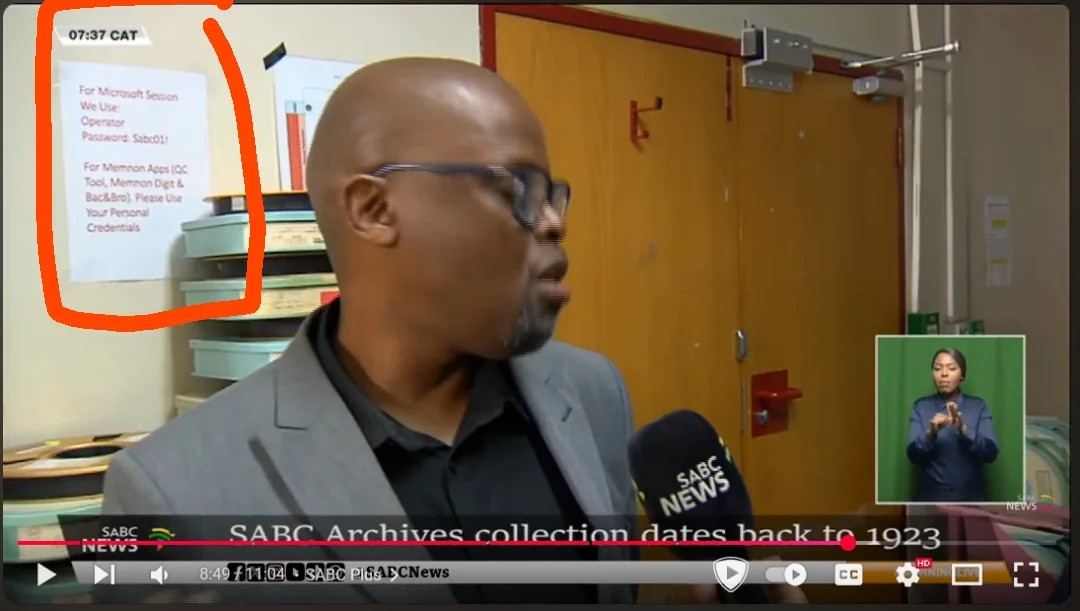
There was a common issue with a local ISP that their default wifi router passwords were based on the router's MAC address.
I scanned the wifis I could reach from my flat and found one that was vulnerable. Now I didn't know who that wifi belonged to. I would have had to knock on everyone's door, asking everyone if it's their wifi. Couldn't be bothered doing that and looking stupid doing so.
So instead I logged into their wifi and from there into their router config web page (it also had the default credentials admin/admin) and changed the SSID to [old SSID]_hacked.
The day after they had changed the SSID back and changed the password.