cross-posted from: https://lemmy.bestiver.se/post/770637
Nitter link: https://xcancel.com/hkashfi/status/1995109785679573167
cross-posted from: https://lemmy.bestiver.se/post/770637
Nitter link: https://xcancel.com/hkashfi/status/1995109785679573167
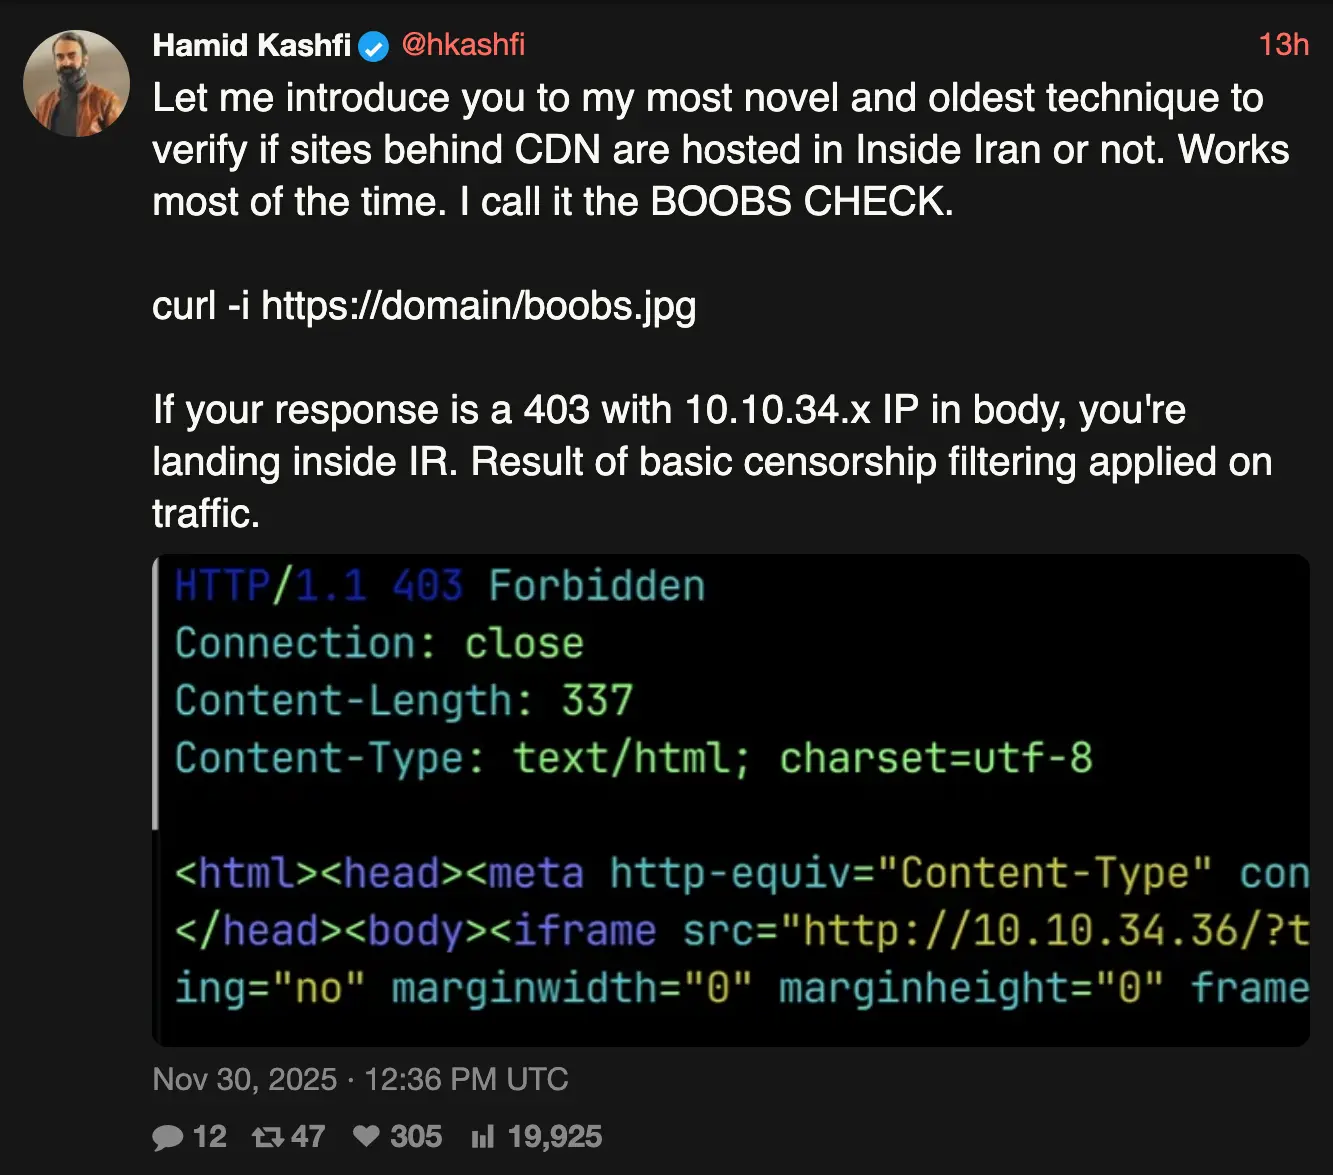
Right? If it were an unencrypted HTTP GET request, then every router on the way would see the plaintext string boobs in the URL and therefore intercept it.
If I had to guess, Iran has so few landline connections that they man-in-the-middle every TLS connection they can by either forcing every server to hand over their private key files (difficult) or by forcing a certificate authority trusted by default Web browsers (there's a lot of them) to issue certificates for every top level domain they see in SNI data attached to encrypted packet headers; the latter method need not even require participation by Iranian servers, so long as the traffic is bottlenecked for man-in-the-middle attacks and outsiders don't question unusual certificate authorities being used.