1


It's my first post. Let me know if there is a better spot for it.

2


cross-posted from: https://lemmy.sdf.org/post/57025341

I set out to determine which AMD processors do not contain the PSP (which actually compromises your security). Started down this rabbit hole. It’s turned into a shitshow of non-determinism.

So, wouldn’t nation states research which processors are spychips and which are not -- in the interest of national security? If yes, is it just a matter of requesting the info?

3


cross-posted from: https://infosec.pub/post/50218987

Karcher DAB radios are broadcasting an SSID for open Wi-Fi access. It doubles as an Internet radio, but AFAICT from the manual it’s only expected to act as a client.

So WTF is going on?

It seems like a really bad idea for consumers to connect this radio to their LANs to use to play Internet radio and podcasts when there is an always available Wi-Fi AP that enables anyone in proxity to connect to the radio. What’s the point? There is no way to disable the SSID broadcasting and it remains on even when the radio is “off” (but plugged in).

The manual shows that there is a remote control. Is the remote using wi-fi? I don’t have the remote so I have no way of verifying. In any case, this design seems like a recipe for disaster. Karcher should perhaps just stick to making pressure washers.

Google and Apple use Wi-Fi SSIDs for navigation. I boycott both companies. As such, I prefer not to have any wi-fi APs. And when I decide to run an AP, I ensure the SSID ends in _optout_nomap to opt-out of giving uncompensated help to the nav systems of Apple and Google.

Does this violate the GDPR? I cannot change the SSID, so it’s like I am being forced to share with the general public the fact that there is a Karcher radio in my home. That does not respect data minimisation.

4


Friends,

We're happy to announce that we have funding available to package BusKill in QubesOS as a contrib package.
Bounty Now Available for BusKill Contrib Package in QubesOS

Thanks to a generous donation from NovaCustom, we're offering a bounty to anyone (including you!) who packages BusKill as an official contrib package for QubesOS.

About BusKill

BusKill is a laptop kill-cord. It's a USB cable with a magnetic breakaway that you attach to your body and connect to your computer.

What is BusKill? (Explainer Video)
Watch the BusKill Explainer Video for more info youtube.com/v/qPwyoD_cQR4

If the connection between you to your computer is severed, then your device will lock, shutdown, or shred its encryption keys


thus keeping your encrypted data safe from thieves that steal your device.

About NovaCustom

In Mar 2015, Wessel klein Snakenborg (founder of NovaCustom) started selling highly-customizable Linux laptops from Europe.

In Aug 2021, NovaCustom released their first laptop (NV40) with coreboot pre-installed with Dasharo.
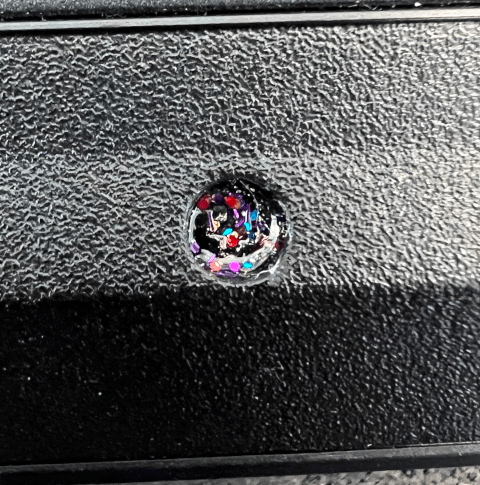
Photo of a screw that's been covered with a unique pattern of (multi-color) glitter nail polish
NovaCustom offers anti-tamper options, including glitter nail polish applied to the chassis screws (photos sent to you via Proton Mail before shipment — specify PGP key at checkout for e2ee)

Since 2023, NovaCustom has been a leader in hardware security:

And now, in Apr 2026, NovaCustom is further working to increase the accessibility of BusKill to QubesOS users, by sponsoring the submission of an official QubesOS contrib package.

Funding Available

If you'd like to claim this bounty for yourself, please

  1. Read the details of the bounty, and then
  2. Submit a proposal by commenting on this GitHub issue

Claim Bounty

opencollective.com/buskill/projects/qubes-package

Moreover, if you're a QubesOS user and you'd like to donate additional funds in support of this bounty, you can do so here.

Stay safe,

The BusKill Team
https://www.buskill.in/
http://www.buskillvampfih2iucxhit3qp36i2zzql3u6pmkeafvlxs3tlmot5yad.onion/

5


cross-posted from: https://lemmy.sdf.org/post/50981571

2fa.directory catalogs services that use multifactor authentication. Of course the idea is to inform consumers of which services satisfy a basic standard of security. Services that are centralised on Cloudflare appear with a green checkmark, as if there is nothing wrong with sharing all your login details with a privacy abusing fiefdom in a country without privacy safeguards through a MitM arrangement.

If one of the auth factors has a MitM, that’s effectively 1 factor less. 2fa becomes like 1fa.

It’s a gross oversight and the bug tracker is limited to MS Github users. A Github user should raise an issue to point this out.

6
7


A bank’s privacy policy lists a lot of data they collect, including customers’ MAC addresses. I was dumbfounded. How is that possible? The router on your LAN obviously knows your device’s MAC address. And I guess the ISP’s router would know your gateway’s MAC address. But from there wouldn’t the bank only see your IP address from the WAN?

Then it occurred to me-- the bank has a smartphone app. So the app likely demands perms to get the phone’s MAC. But then what would the likely purpose be? To check vendor consistencies (to block VMs) and raise impostor flags if your MAC changes?

(update) Another question: instead of using the bank’s shitty phone app, you use their shitty web app instead. I would assume the JavaScript engine is naturally blocked from obtaining your MAC address and transmitting it. But I would like a sanity check.. anyone know for certain?

8


cross-posted from: https://lemmy.sdf.org/post/45188081

I am locked out of Github because the disposable email address I was willing to trust Microsoft with is no longer reachable. Every single login into GH requires an email confirmation. So if you cannot enter the 1-time access token, you’re fucked.

You might think a big corporation like Microsoft would not make such an amateurish mistake.

9


cross-posted from: https://lemmy.sdf.org/post/41050620

Spy chips are:

  • Intel CPUs after ~2008
  • AMD CPUs after ~2013
  • Arm CPUs (not sure when they started the trustzone stuff but likely around 2013 since AMD uses trustzone)

I believe IBM Power9 chips are spy chip free, but not sure about the successors.

Anyway, the question is about Apple chips. Web searches are lousy these days. I find nothing to confirm or deny the presence of management engines in Apple (Motorola?) CPUs.

Intuitively, I don’t think it would make business sense for Apple to do that because a majority of their customers are non-corporate individuals (unlike intel). OTOH, if that were sound logic then it would seem to contradict Arm chips which are also largely bought by non-corporate individuals.

Anyway, if anyone knows plz mention it here, ideally with a source.

Thanks!

10


cross-posted from !emailprivacy@fedia.io: https://lemmy.sdf.org/post/39872278

  • 2013: MS critisized Google for snooping on email for advertising (and had negative ad campaign called scroogle). MS (rightfully?) had a reputation for not snooping on email for ads.
  • 2021: MS bought Xandr (a surveillance advertising company).
  • today: MS’s privacy policy seems vague, which is apparently due to user configuration options. There is an opt-out page, but that’s vague too.

I am NOT a Microsoft patron or user. These privacy policies are directed at MS’s own users, not outsiders whose email payloads are exposed to MS in comms with MS users. So as an outsider, I do not have the privilege of knowing what settings my correspondent has chosen. I have to assume the worst settings.

When Bob-whoever@outlook.com talks via email to Alice-whoever@disroot.org, can anyone confirm or deny whether MS/Xander collects data about Alice the outsider?

update: this page shows Microsoft denying that they scan email for ad data, but there is cause for doubt from what the user is saying.

11


Some obnoxious piece of shit scumbag has been non-stop attacking Debian testers with a flood of spam the past several days.

Why attack a harmless charity? Why not target a shitty expoitive platform like MS Github instead? It’s choosing to target an organisation that just helps people. It would be like entering a public library and taking a shit on the carpet, when you could have just as well taken a shit on the hood of Elon Musk’s car hood instead, for example.

This is not just a rant. I want a serious answer. I have a vague notion of why spam exists. It’s not just malice without purpose. Cyber criminals build botnets to effectively create powerful supercomputers for very little money by hijacking their victim’s CPU cycles and the energy that drives them. Then they sell supercomputing access on the black market, or they mine cryptocurrency. Those criminal botnets need to be controlled surreptitiously.

Spam somehow facilitates the command and control of the botnets. Supposedly… though I struggle to understand why. When spam is sent to some arbitrary recipient, how does that serve as a command signal? Is it perhaps a mechanism that only serves the botnet if the spam recipient happens to be unwittingly part of the botnet? Thus everyone who is not on the botnet who receives spam, it’s just a waste for everyone?

Surely there are more clever ways to anonymously control a botnet without shitting on the world with spam. Surely the rage spam causes motivates intelligence agencies to shut them down, no?

1990s botnets were clumbsy. The greed was unhinged so they would steal as many CPU cycles from each PC as possible. When someone’s PC is so sluggish it’s intolerably dysfunctional, it was a big red flag. The victim reinstalled Windows to overcome and thus shrinks the botnet, which increases the botnet owner’s burden of having to reinfect more PCs. So they got more clever.. they only steal enough processing to go unnoticed. I’m not seeing how spam fits into modern day clever crimes.

spoiler


12


Before sharing my email address with some person or some org, I do an MX DNS lookup on the domain portion of their email address. It’s usually correct. That is, if the result is not of the form *.mail.protection.outlook.com, then that recipient is not using Microsoft’s mail server.

But sometimes I get stung by an exception. The MX lookup for one recipient yielded barracudanetworks.com, so I trusted them with email. But then they sent me an email and I saw a header like this:

Received: from *.outbound.protection.outlook.com (*.outbound.protection.outlook.com…

Is there any practical way to more thoroughly check whether an email address leads to traffic routing through Microsoft (or Google)?

13


The knee-jerk answer when an app pushes designed obsolescence by advancing the min Android API required is always “for security reasons…” It’s never substantiated. It’s always an off-the-cuff snap answer, and usually it does not even come from the developers. It comes from those loyal to the app and those who perhaps like being forced to chase the shiny with new phone upgrades.

Banks, for example, don’t even make excuses. They can just neglect to be mindful of the problem and let people assume that some critical security vuln emerged that directly impacts their app.

But do they immediately cut-off access attempts on the server-side that come from older apps? No. They lick their finger and stick it in the air, and say: feels like time for a new version.

It’s bullshit. And the pushover masses just accept the ongoing excuse that the platform version must have become compromised to some significant threat -- without realising that the newer version bears more of the worst kinds of bugs: unknown bugs, which cannot be controlled for.

Banks don’t have to explain it because countless boot-licking customers will just play along. After all, these are people willing to dance for Google and feed Google their data in the first place.

But what about FOSS projects? When a FOSS project advances the API version, they are not part of the shitty capitalist regime of being as non-transparent as possible for business reasons. A FOSS project /could/ be transparent and say: we are advancing from version X to Y because vuln Z is directly relevant to our app and we cannot change our app in a way that counters the vuln.

The blame-culture side-effect of capitalism

Security analysis is not free. For banks and their suppliers, it is cheaper to bump up the AOS API than it is to investigate whether it is really necessary.

It parallels the pharmacutical industry, where it would cost more to test meds for an accurate date of expiry. So they don’t bother.. they just set an excessively safe very early expiration date.

Android version pushing is ultimately a consequence of capitalist blame-culture. Managers within an organisation simply do not want to be blamed for anything because it’s bad for their personal profit. Shedding responsibility is the name of the game. And outsourcing is the strategy. They just need to be able to point the blame away from themselves if something goes wrong.

Blindly chasing the bleeding-edge latest versions of software is actually security-ignorant¹ but upper management does not know any better. In the event of a compromise, managers know they can simply shrug and say “we used the latest versions” knowing that upper managers, shareholders, and customers are largely deceived into believing “the latest is the greatest”.

¹ Well informed infosec folks know that it’s better to deal with the devil you know (known bugs) than it is to blindly take a new unproven version that is rich in unknown bugs. Most people are ignorant about this.

Research needed

I speak from general principles in the infosec discipline, but AFAIK there is no concrete research specifically in the context of the onslaught of premature obsolescence by Android app developers. It would be useful to have some direct research on this, because e-waste is a problem and credible science is a precursor to action.