1
submitted 6 hours ago by to c/linux@lemmy.ml


Currently running mint on a 15+ year old HP laptop but I want to update to a 'modern' second hand Thinkpad. The second hand market is just full of different model numbers and I'm not sure how to filter to what I'm after.

I get most tech basics (ram, ssh) but I'm not sure what all the models numbers, generations or processors mean.

Looking for something with a memory card spot, HDMI output and ideally touchscreen.

I don't use it for gaming but have an ultra wide screen high res monitor (possibly 2k cant quite remember) that I'd like to take advantage of.

Larger SSD and 16gb ram wouldn't hurt too but I assume I can upgrade them.

I don't need the Yoga tablet style folding.

2


TUXEDO Computers has just announced that its upcoming Debian-based TUXEDO OS has entered the final stage of its open beta. That brings the Linux distro right up to the point of being fully transitioned away from Ubuntu.

The new edition, known as TUXEDO OS “Continuous Debian,” replaces the distribution’s traditional Ubuntu foundation with Debian Testing. The change denotes a significant shift for TUXEDO OS, which is developed by German Linux hardware manufacturer TUXEDO Computers.

Open beta testing started in August, and since then the dev team has issued five beta ISOs. The company has reported a large number of bug reports as a result of the testing, as well as a lot of positive feedback from users who have been running the new system without any issues.

As for the software, the current beta runs KDE Plasma 6.7.4 on Wayland, alongside KDE Frameworks 6.30, Qt 6.11.2, and Linux kernel 7.2. Unlike Debian itself, which periodically promotes its Testing branch to Stable, TUXEDO OS will remain permanently based on Debian Testing.

TUXEDO Computers will also continue maintaining its own package repositories and providing updates for key components, including the kernel, graphics drivers, and KDE Plasma.

Throughout November, the development team is concentrating on handling outstanding bug reports and handling remaining issues before the first stable release. Users participating in the testing program are encouraged to report not previously identified bugs or unanticipated behavior as soon as possible.

However, bug fixing is not the only thing left to do. TUXEDO Computers also needs to establish and validate a suite of structured, automated QA test procedures. Those tests have to be run before they can actually set a release date.

As for when the stable Debian-based TUXEDO OS will be arriving, the developers have not given us a date at this point. They do, however, expect to be able to release it fairly soon once the final testing and QA are complete.

For additional information, see the announcement.

Those interested in testing the upcoming Debian-based TUXEDO OS before its stable release can download the latest beta ISO images from the preview download directory.

3
submitted 5 hours ago by to c/linux@lemmy.ml


asking seriously. because i installed kubuntu after setting up luks2 encryption in installer and it all seemed fine. until i booted into ubuntu and saw grub menu asking for commands . i asked chatgpt it gave complex fixes and stuff. so im now installing windows 11 again and deleted kubuntu.

now im not blaming linux. but this is a genuine question. is linux hard?

i had bitlocker encryption working perfectly on windows 11 no boot issues.

4


Clarification: I normally physically log on to and play media on host A using mpv, displaying the video on an external monitor HDMI-A-2 and playing the audio from host A's headphone jack connected to external speakers. Today, I tried not physically logging on to host A, but remotely logging in from host B (my phone) using ssh from the same network and running the mpv command from host B. mpv then displays the video on the expected display HDMI-A-2, but it doesn't play any audio.

Symptomatically, if I haven't logged on physically to host A, mpv only displays video, plays no audio and throws errors. Why do I need to be physically logged on to host A for mpv to be able to access audio? You'd think a video feed would be more guarded than an audio one. But maybe this isn't about security at all? Please enlighten me! 😊

5


I got a pc that suffers from severe heating problems because of its poorly designed passive cooling case. I tried several strategies to put temperature under control, did a lot of tests with thermald, but ended up hacking a fan into the case. However, I still have problems with ssd temperatures.

Right now, as I write this, the nvme ssd is at 67ºC and easily goes beyond 80 or 90 during data transfers. I already lost 2 ssds before realizing this was the problem, because I was controlling just the cpu temperature.

There's no physical way to force airflow where the ssd is, so I was wondering if there's some way to throttle data transfer of something to prevent the ssd temperatures from reaching a threshold. All I could find was a vibecoded github repository. I don't care if data transfer gets ridiculously slow, as long as the ssd remain safe, and I can't consider getting any new hardware right now.

I'm currently running fedora 44 on that machine

Edit: I thought there was an easier software mitigation to that, but apparently, solutions will tend to the hardware side, so here are the hardware details:

  • It's an unbranded chinese cheap mini pc with a heat dissipation case that doesn't dissipate well
  • The ssd is mounted on the back of the motherboard. The model is a sandisk M.2 1TB 2280
    Here's a photo of the case, for the reference (don't judge me lol):
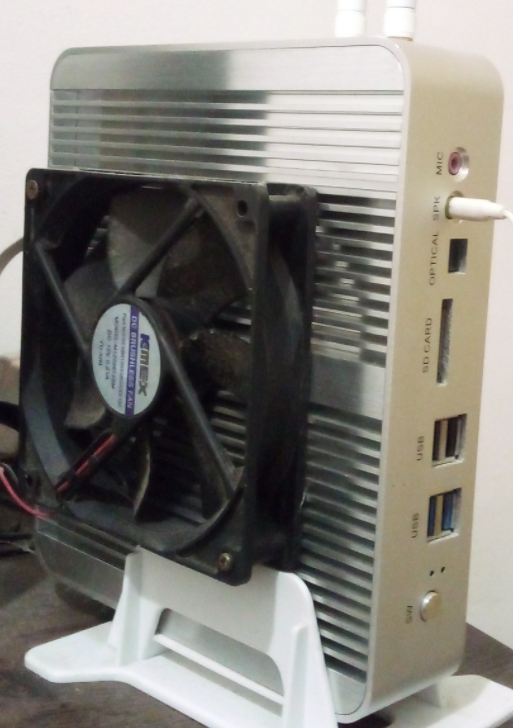
image

6
7


Timestamps:

00:00 Intro

00:38 Sponsor: Internxt

02:43 Affinity confirms Linux version is coming

04:33 Proton apologizes, publishes Al manifesto

08:10 Cutefish runs native macOS apps now

11:20 SUSE to let go of 10% of their workforce

13:24 Fedora 45 released

14:56 Linux Mint shows more of their new apps

17:08 OpenAl found about 1000 flaws in the kernel

19:07 Nvidia drivers update with better Wayland support

20:23 Discord ditches electron for their client, for Rust

21:46 News publishers sue Brave for selling heir content to Al providers

23:37 Macs get their Apple Silicon Proton in the form of Hadron

25:55 Sponsor: Tuxedo Computers

Links

Affinity confirms Linux version is coming

https://www.omgubuntu.co.uk/2026/11/affinity-linux-release-confirmed

Proton apologizes, publishes Al manifesto

https://www.techradar.com/vpn/vpn-services/proton-apologizes-to-community-after-internal-memo-shows-force-behind-proposed-ai-use-in-building-its-privacy-products

https://proton.me/blog/ai-manifesto

Cutefish runs native macOS apps now

https://cutefish.org/blog/running-mac-apps/

https://cutefish.org/blog/mac-apps-first-milestone/

SUSE to let go of 10% of their workforce

https://www.theregister.com/software/2026/11/02/suse-to-cut-one-in-ten-employees-because-of-ai/5306950

Fedora 45 released

https://fedoramagazine.org/announcing-fedora-linux-45/

Linux Mint shows more of their new apps

https://blog.linuxmint.com/?p=5093

OpenAl found about 1000 flaws in the kernel

https://www.phoronix.com/news/OpenAI-948-Linux-LPE-Bugs

Nvidia drivers update with better Wayland support

https://9to5linux.com/nvidia-620-linux-graphics-driver-released-with-wayland-improvements

Discord ditches electron for their client, for Rust

https://www.theverge.com/news/1027379/discord-ditching-electron-web-app

News publishers sue Brave for selling heir content to Al providers

https://techcrunch.com/2026/11/02/new-york-times-and-other-outlets-sue-web-browser-brave-over-alleged-content-scraping/

Macs get their Apple Silicon Proton in the form of Hadron

https://github.com/Broyojo/hadron

8


Embracing ABI compatibility, AlmaLinux OS branches out with new features and capabilities while maintaining compatibility with RHEL.

9


Unredacted hardened Kernel

Hardened debian kernel built on top of graphene os patches by the redacted non profit . Details for apt repo are here.

https://git.unredacted.org/unredacted/linux-hardened-unredacted

Figured Id share for those interested. Text below copied from git readme.

What this kernel changes

On top of upstream Linux, this build applies the anthraxx/linux-hardened patch set under a kernel .config composed from anthraxx's own Arch packaging config.x86_64 (pinned by sha256 + signed-commit-verified in configs/upstream-seed.toml) layered with our project overlay (configs/intent.common.config plus the x86-only configs/intent.x86_64.config; per-symbol rationale in configs/POLICY.md). Each build re-fetches the pinned seed, verifies its signature, merges our intent, runs olddefconfig, and aborts unless every intent line lands — so new hardening features anthraxx adopts flow through automatically, while regressions on the symbols we explicitly pin fail fast at configure time. Full design in docs/operators/config-architecture.md. The hardening falls into four buckets: memory-safety (heap and stack zero-init, stack-erase-on-return, hardened usercopy, FORTIFY_SOURCE, slab freelist hardening and canaries, KASLR, KFENCE); integrity (W^X for kernel and module text, forced module-signature verification, integrity-mode lockdown under Secure Boot); attack-surface reduction (/dev/mem, /proc/kcore, kexec, and several legacy syscalls removed); and restrictive sysctl defaults (unprivileged user namespaces off; perf, BPF, and ptrace restricted to root).

That hardening comes with friction worth knowing before you install:

  • Out-of-tree modules (NVIDIA, ZFS, VirtualBox) must be rebuilt against our headers and signed. DKMS is designed to do this with a machine-local MOK key you enroll once at reboot (not yet validated against a published release — see docs/users/dkms.md).
  • Rootless containers (Docker, Podman), the Chromium sandbox, Snap, and Flatpak depend on unprivileged user namespaces, which are off by default. Re-enable them via the opt-in in docs/users/incompatibilities.md.
  • kexec/kdump, hibernation, and /dev/mem-based tools do not work.
  • Every module must be signed. An unsigned out-of-tree module will not load (MODULE_SIG_FORCE).

Per-symptom workarounds are in docs/users/incompatibilities.md. Keep your distro's stock kernel installed as a recovery fallback; both coexist and GRUB lists both.

10
11
Can I update now? (lemmy.today)
submitted 1 day ago by to c/linux@lemmy.ml


System SpecificationsOperating System: CachyOS Linux

KDE Plasma Version: 6.8.0

KDE Frameworks Version: 6.31.0

Qt Version: 6.12.0

Kernel Version: 7.2.11-1-cachyos (64-bit)

Graphics Platform: Wayland

Processors: 12 × 12th Gen Intel® Core™ i5-12450H

Memory: 8 GiB of RAM (7.5 GiB usable)

Graphics Processor 1: Intel® Graphics

Graphics Processor 2: NVIDIA GeForce RTX 3050 Laptop GPU

Several days ago, I tried to update my CachyOS system. And seen the below warning from Pacman itself

Update notice: Kernel 7.3.0-2 has issues with amdgpu particularly causing black screen on AMD dGPUs

At first, I was like gonna do the update, because I don't have an AMD CPU/GPU. Then I went to check on the internet and found lots of issues with both Kernel 7.3 and KDE Plasma 6.8.1. Even affecting NVIDIA GPU.

Some of the examplesLinux 7.3 - GPU idle increased from 10 W to 60. Anyone else?

Partial upgrade for ca-certificates-mozilla

Plasma 6.8.1 update: fullscreen games choppy (fine in windowed), desktop animations laggy - fixed by downgrading to 6.8.0

Choppy frame pacing in CS2 and Deadlock (300–500 FPS) after 2026-10-22 update (linux 7.3.0, linux-firmware-amdgpu 20261019, Plasma 6.8.1) – RX 6600 XT, Wayland – fixed by snapshot rollback

Steam games broken after updating from kernel 7.2.11-1 -> 7.3.0-2 (not fixed by 7.3.0-3)

linux-cachyos 7.3.0-4: amdgpu “Fence fallback timer expired” causes game crashes (RX 6600 XT) (Monster Hunter Wilds)

Cachyos kernel upgrade to 7.3.0 - fails on AMD

After latest update to cachyos-rate-mirrors the speeds are horible

GPU and CPU Fans Running at Double Speed under 7.3.1

Cachy kernel version 7.3.1 breaks the dual display (DisplayLink device) (KDE Plasma) (Kwin)

Cannot login after the latest update from kernel 7.2.10-1 -> 7.3.0-2 (presented with a frozen screen)

Nvidia-open 615.78.08: dGPU runtime D3 “Not supported” on linux-cachyos 7.3.0-4, works on LTS 6.18.55-2

Steam games broken after updating from kernel 7.2.11-1 -> 7.3.0-2 (not fixed by 7.3.0-3)

Is there a reason that the BORE kernel is stale (7.2.10 vs. 7.3.0)?

After Recent Update, Shut Down Takes Over 1 Minute - User Manager Issue?

Behringer UMC404HD - fail with Kernel 7.3.0

LACT power cap write fails with “Operation not supported (os error 95)” on 7.3.0-3-cachyos

Plasma 6.8.1: immediate screen tearing / flickering shadows / black areas on GTX 1650 Ti (HP Pavilion Gaming 15-dk1xxx) - 6.8.0 is fine

Updating to 7.3.0-3-cachyos causes UMC204HD Audio Interface to be unusable

Issue with AdaptiveSync kernel 7.3+

Keyboard Backlight Not Working With 7.3 Kernel

Kernal 7.3.0-3 - AMD / NVIDEA

Should i stay at linux-cachyos 7.2.11-1?

After update audio is is wery crapy and not loud

Audio echo in FAudio/Proton games on launch — regression starting linux-cachyos 7.3

Severe display artifacts and flickering on NVIDIA HDMI output after today’s first upgrade (2026/10/22)

Update causing KDE Plasma crash or blackscreen at boot

After KDE 6.8 update, Desktop Animations lag and Games run on 48fps

7.3.0-2 on RX 9070 XT: no black screen, but a DCN401 MCM LUT warning on HDR enable (Plasma 6.8.0)

After update lost fps

Not every link I shared is completely relevant to me, but the amount of issues on Kernel 7.3 and KDE Plasma 6.8.1. Even affecting NVIDIA GPU made me hesitant.

Because of this hesitation, I also didn't update Firefox CA-Certificates security update.

Should I update now?

12


I have 2 monitors, 2 keyboards, 2 mice, and 1 computer. How can I set it up for shared use?

I know this was possible on X but with Wayland maturing I assume it's moved over.

13
14
Do good things (lemmy.world)
submitted 4 hours ago by to c/linux@lemmy.ml
 
 
15


I am running DietPi on a RPI in my network with some docker containers on it.

I recently got the idea to switch off containers when not needed, e.g. during the night, since this will allow my hard drive to switch off and saves a bit of energy.

I do not recall how I found out, but for some reason what I did was to just edit the /etc/crontab file that DietPi has with sudo. Worked like a charm, I had my containers stopped and started just as specified.

But then I wanted to make some changes, change some times, add some other stuff. I did it the same way, edit the /etc/crontab file with sudo. Didn't work, none of my new additions worked.

I searched online and figured out the better way to do this is use the command "crontab -e", edit stuff there, then also check with "crontab -l" right after. That worked, now my new containers are all behaving as they should.

But how do I now get rid of the stuff I defined in /etc/crontab? I removed it all from that file, saved it, restarted the system, nothing removed these, they are somehow persisting. I know they do because I use a different log file for these and that log file still gets generated now. How can I fix this?

Bonus question about log files, how can I make them more useful in terms of information? Right now they just name the command, not even a timestamp or anything.

Thanks!

16
 
 
17
18
19


The Artix Linux development team released Artix Linux 2026.11 today as the official ISO refresh for this Arch Linux-based, systemd-free distribution, which features multiple editions and init systems.

Coming six months after Artix Linux 2026.04, the Artix Linux 2026.11 official ISO release is powered by the Linux 7.2 kernel series, namely Linux kernel 7.2.14, and ships with the Wayland-only KDE Plasma 6.8 desktop environment for the Plasma edition, along with KDE Frameworks 6.31 and KDE Gear 26.08.2.

According to the devs, only the Plasma edition of Artix Linux has full Wayland support. Other editions are in various stages of implementing Wayland support, but it’s not yet ready for daily use. Therefore, even if you see a Wayland session on the login manager, it will probably not work well or at all.

The user services have matured, and Artix Linux 2026.11 is fully implementing them for both OpenRC and dinit init systems. The devs said that they can also be enabled for the runit and s6 init systems via userspawn, but, for the time being, this task is left to the end user.

Among other noteworthy changes, Artix Linux devs keep working on the Plasma Gaming and Xfce Gaming editions, which are currently being offered as beta versions, and they will remain in the weekly downloads section for further testing. Check out the release announcement for more details.

You can download Artix Linux 2026.11 right now from the official website as live ISO images with the aforementioned desktop environments and init systems for 64-bit machines. Of course, these new ISO images are here only for new deployments or those who want to reinstall their Artix Linux systems.

Since Artix Linux follows a rolling release model, existing users need only to update their installations by running the sudo pacman -Syu command in a terminal emulator or by using a graphical package manager on their favorite desktop environment, such as Plasma Discover or one of the many pacman GUIs.

20


Edit2: Solved! Thank you all! 🥰 I was supposed to put quotation marks around the command argument variable/substitute within the script, as in scanimage -d [device] –format=png -p -o “$1”

Edit: turns out it's not the accented character, but the whitespace character in front of július.png, since the script doesn't accept julius.png either.

#!/bin/bash  
# name of the script is SCAN.bash  
scanimage -d [device] --format=png -p -o $1  

I have tried ' ', " " and to escape it with \

./SCAN 'anyu 1988 július.png'  
./SCAN "anyu 1988 július.png"  
./SCAN anyu\ 1988\ július.png  

But it throws argument without option. It works fine if I type it out instead of scripting.

The target language is Hungarian and I have generated the necessary locale.

21


"We are happy to announce the general availability of Fedora Asahi Remix 45. This release brings Fedora Linux 45 to Apple Silicon Macs. What’s included

Fedora Asahi Remix is developed in close collaboration with the Fedora Asahi SIG and the Asahi Linux project. This release incorporates all of the exciting improvements brought by Fedora Linux 45. Like previous releases, Fedora Asahi Remix 45 supports Apple M1 and M2 systems. In addition, this release includes out of the box initial support for Apple M3, M3 Pro and M3 Max. Asahi Linux upstream now officially supports these new systems. The GPU drivers enabling performant 3D acceleration on the M3 systems are not included at this point. They will be available via a Mesa update in the future.

Fedora Asahi Remix offers KDE Plasma 6.8 as our flagship desktop experience. All of the new and exciting features brought by Fedora KDE Plasma Desktop 45 are included.

A GNOME variant is also available, featuring GNOME 51, with both desktop variants matching what Fedora Linux offers. Fedora Asahi Remix also provides a Fedora Server variant for server workloads and other types of headless deployments. Finally, we offer a Minimal image for users that wish to build their own experience from the ground up. Installation

You can install Fedora Asahi Remix today by following our installation guide. Follow the usual Fedora Linux upgrade process for existing systems running Fedora Asahi Remix 43 or 44. Upgrades via GNOME’s Software application are unfortunately unavailable. Either KDE’s Plasma Discover or DNF’s System Upgrade command must be used."

22
submitted 4 days ago by to c/linux@lemmy.ml
 
 
23
Kitty 0.50 (sw.kovidgoyal.net)
submitted 4 days ago by to c/linux@lemmy.ml
24
submitted 3 days ago by to c/linux@lemmy.ml


i've been configuring my system and when i checked my PATH there were duplicates. so i started trying to deduplicate it for tidiness, so far i've been messing around with 90-user.conf and .profile files. i also did some other stuff in my nushell configs but that's because of how nushell works, so i don't have much doubts about that.

i'll try to be as clear, concise as possible, but since i've started doing this stuff very recently i might not exactly know where to aim my question. so i guess i have doubts regarding if this is a correct way to handle PATH declaration and deduplication. from what i understand, i need to define it in various places because having a correct path depends largely on where you're inheriting it. so maybe your GUI session has a proper PATH, but if you log in through a TTY or similar you might have a different one. also different files also add their own stuff. so should i only care about these 2 files to have a proper file or is there something else i should keep in mind? is the reasoning correct?

if you need some other file just let me know and i'll share it if it's useful. below is system information in case it's relevant.

❯ fastfetch

╭─ システム                    [ghost-user]
│
│ os Fedora Linux 43
│ kernel 7.2.13-100.fc43.x86_64
│ age 345 days
│ uptime 8 hours, 10 mins
│ shell nushell 0.99.1
│ de GNOME 49.10
│ wm Mutter (Wayland)
│ cpu AMD Ryzen 5 5600G 4.46 GHz
│ memory 5.23 GiB / 7.05 GiB (74%)
│
│                                過去を殺せ
╰──────────────────────────────────────────

#90-user.conf

EDITOR=hx
BROWSER=firefox
XDG_DATA_HOME=$HOME/.local/share
XDG_CONFIG_HOME=$HOME/.config
XDG_CACHE_HOME=$HOME/.cache

PATH=$HOME/.local/bin:$HOME/.cargo/bin:$HOME/.opencode/bin:/usr/local/go/bin${PATH:+:$PATH}
PKG_CONFIG_PATH=/usr/lib64/pkgconfig
#.profile

export _DOTFILES_PROFILE_SOURCED=1

case ":$PATH:" in *":$HOME/.opencode/bin:"*) ;; *) PATH="$HOME/.opencode/bin:$PATH" ;; esac

[ -f "$HOME/.cargo/env" ] && . "$HOME/.cargo/env"

case ":$PATH:" in *":/usr/local/go/bin:"*) ;; *) PATH="$PATH:/usr/local/go/bin" ;; esac

if [ -n "$PATH" ]; then
    pinned=""
    IFS_OLD=$IFS
    IFS=:
    for _d in $PATH; do
        [ -z "$_d" ] && continue
        case ":$pinned:" in *":$_d:"*) continue ;; esac
        [ "$_d" = "$HOME/.local/bin" ] && continue
        pinned="${pinned}${pinned:+:}${_d}"
    done
    IFS=$IFS_OLD
    unset _d
    export PATH="$HOME/.local/bin:$pinned"
fi

verification:

#bash

❯ echo "$PATH" | tr ':' '\n'
/home/ghost_user/.local/bin
/usr/lib64/ccache
/home/ghost_user/.cargo/bin
/home/ghost_user/.opencode/bin
/usr/local/go/bin
/usr/local/bin
/usr/bin
#nushell

❯ $env.PATH
╭───┬────────────────────────────────╮
│ 0 │ /home/ghost_user/.local/bin    │
│ 1 │ /usr/lib64/ccache              │
│ 2 │ /home/ghost_user/.cargo/bin    │
│ 3 │ /home/ghost_user/.opencode/bin │
│ 4 │ /usr/local/go/bin              │
│ 5 │ /usr/local/bin                 │
│ 6 │ /usr/bin                       │
╰───┴────────────────────────────────╯
25
Bazzite 45 is here! (universal-blue.discourse.group)
submitted 4 days ago by to c/linux@lemmy.ml
view more: next ›